API Security
Shift left and integrate right. Discover every API in your codebase — including shadow and zombie APIs — and address vulnerabilities earlier and faster in the SDLC.
Discover Why Checkmarx Makes API Security Easier
Checkmarx discovers APIs at the source – scanning code and documentation to give you complete visibility into your entire API footprint, including the Shadow and Zombie APIs traditional WAFs and gateways can’t see.
Global API Inventory
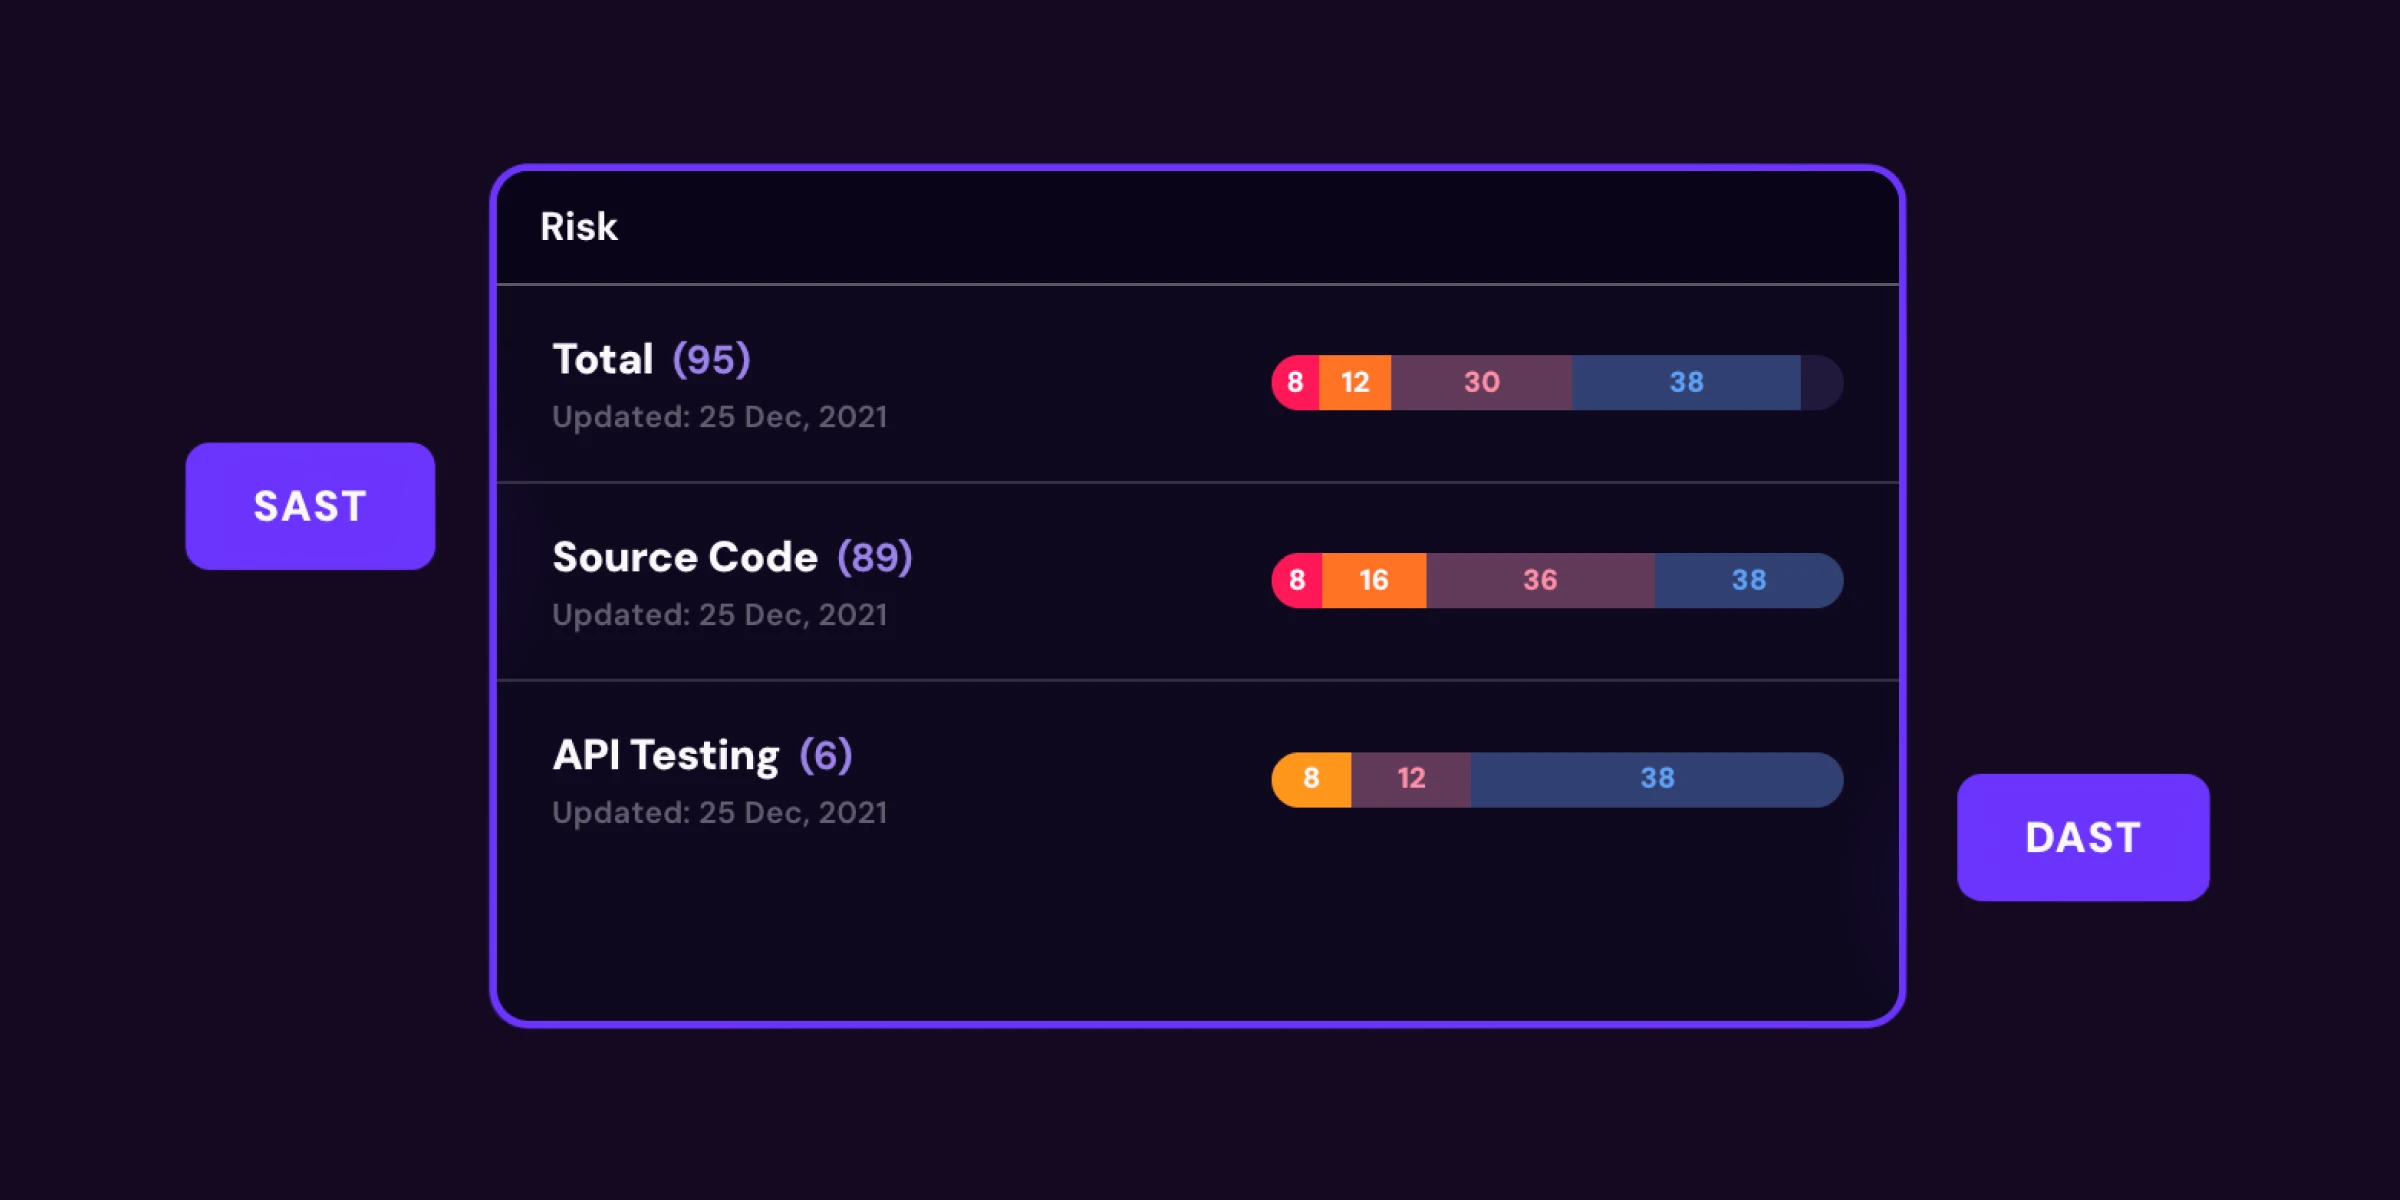
Full inventory of every API and detected vulnerabilities, allowing you to prioritize remediation based on business risk.
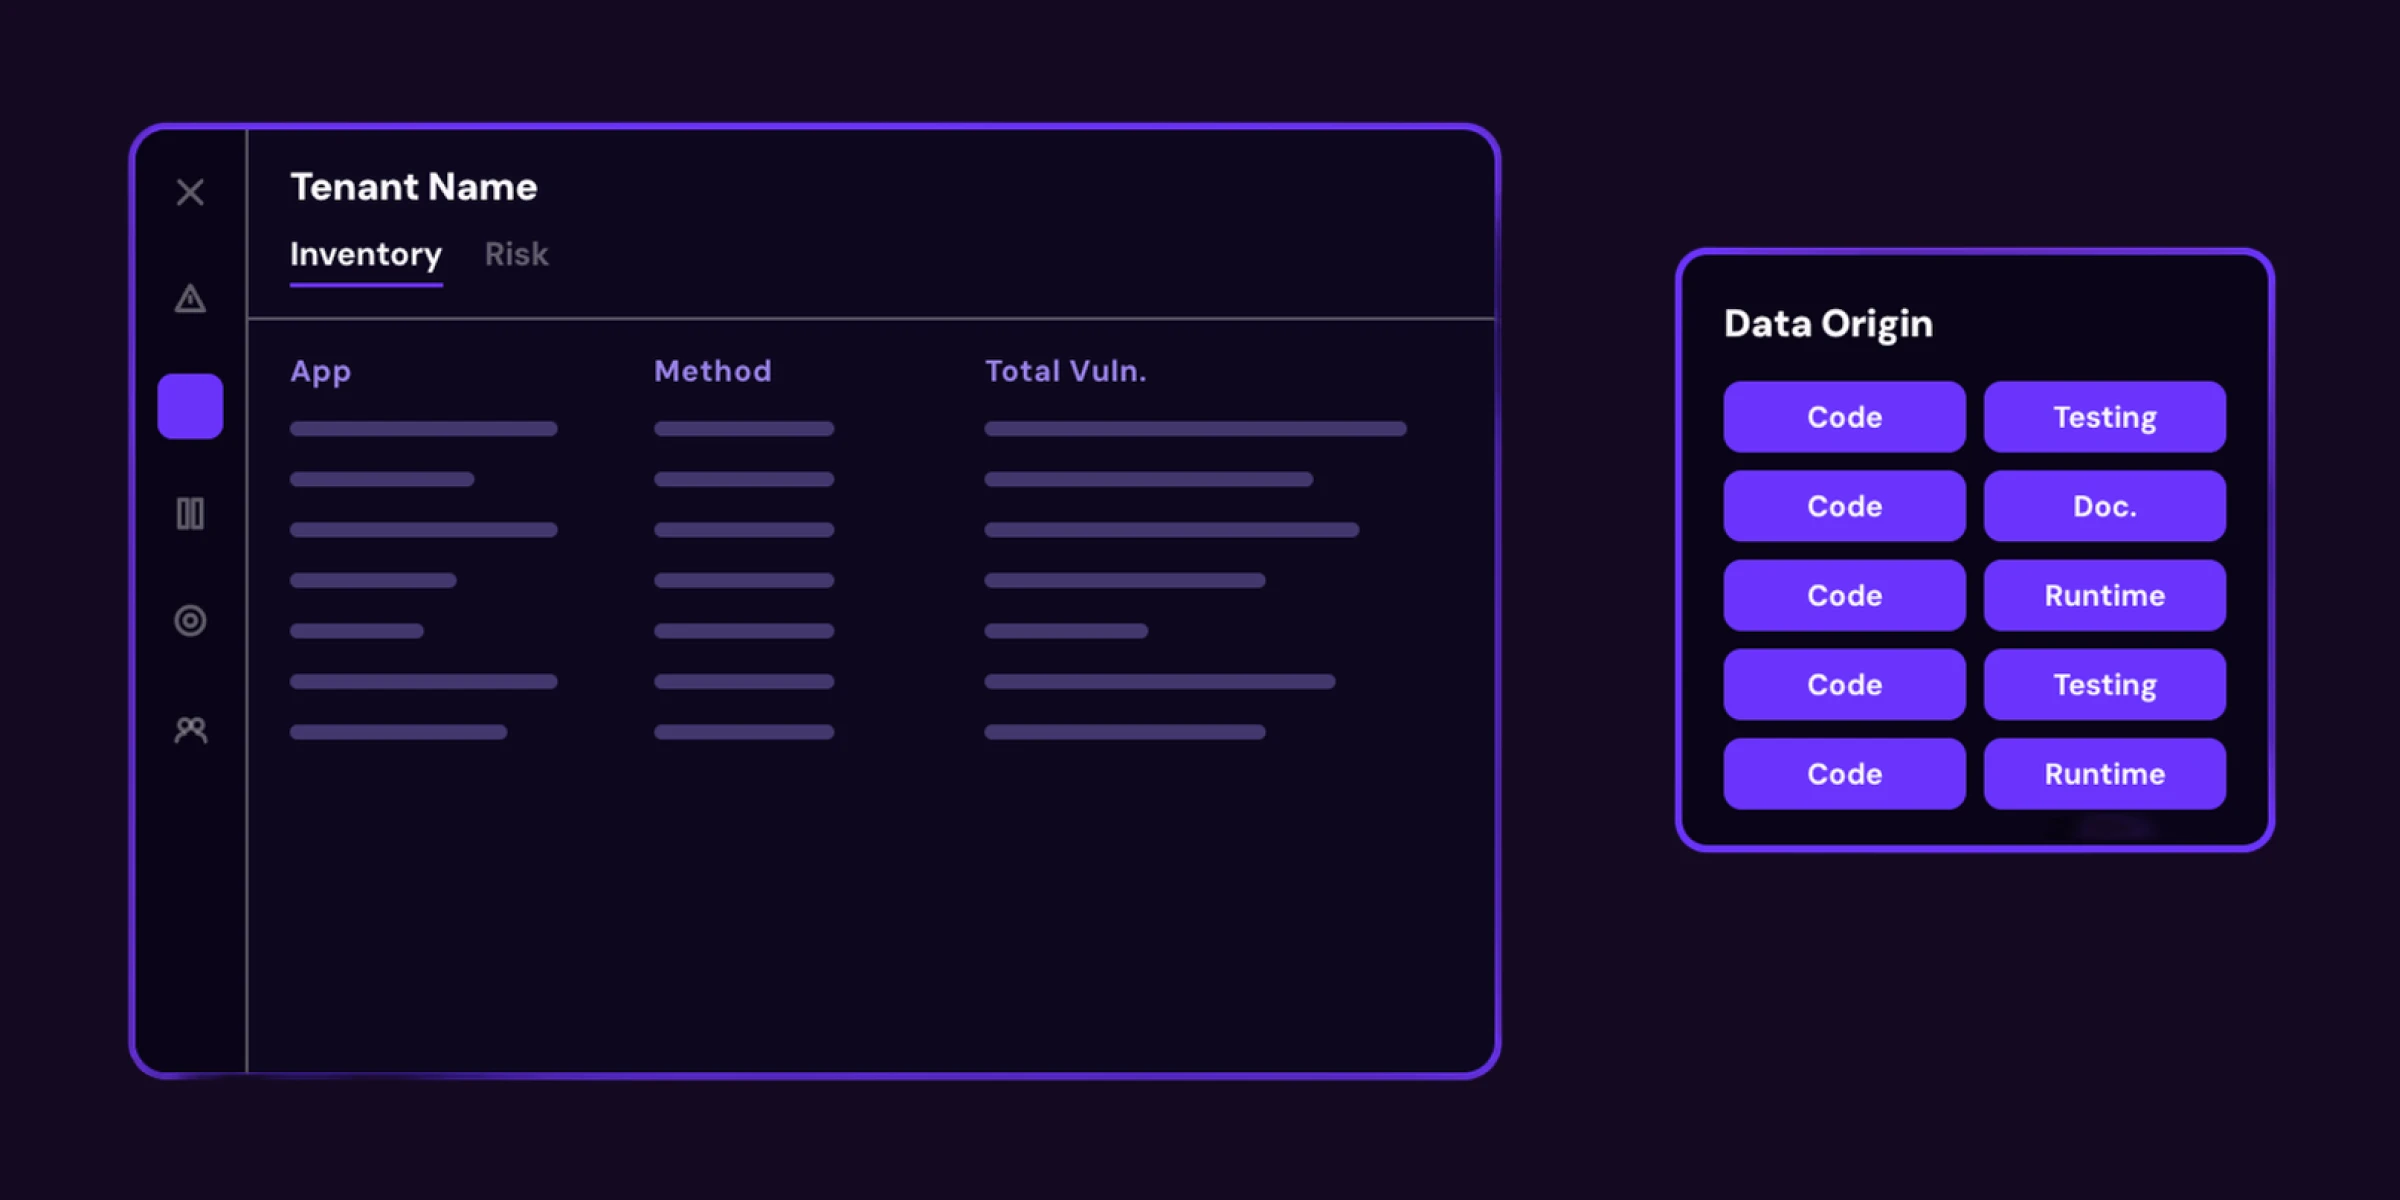
API Discovery
Scans source code and documentation to discover and inventory every API defined in the application – including shadow APIs (undocumented APIs unknown to AppSec teams) and zombie APIs (abandoned endpoints left running after version migrations). Traditional WAFs and gateways can only protect what they know exists.
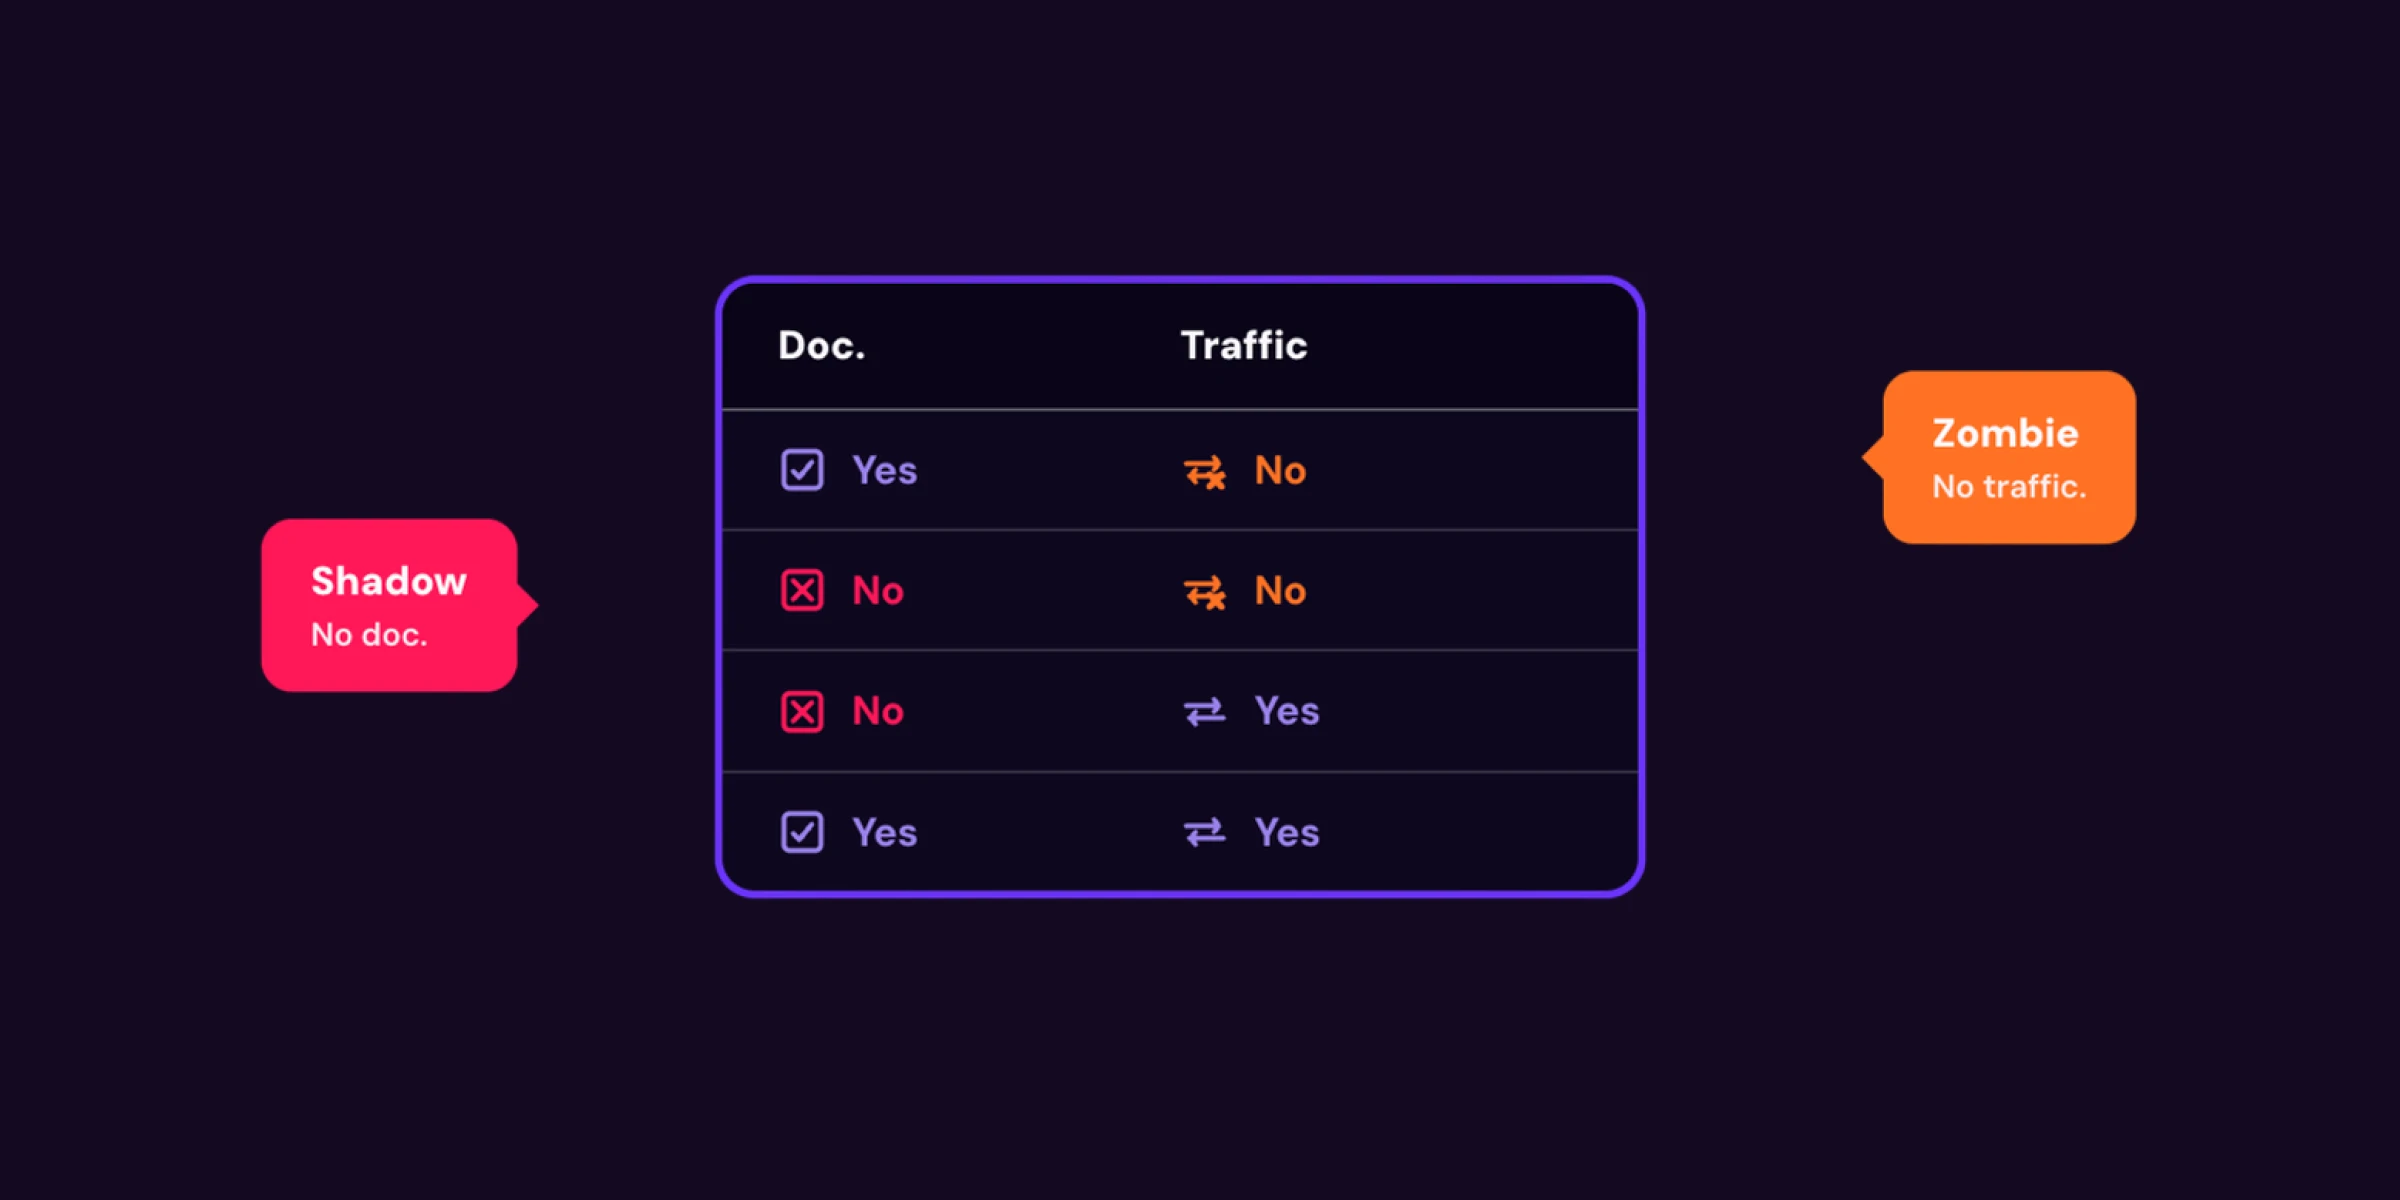
API Documentation Scanning
Automatically scan API documentation (OpenAPI, Swagger, Postman collections) and compare it against the global inventory to identify data discrepancies and undocumented APIs. When your docs don’t match your code, Checkmarx flags every gap – before attackers find them first.
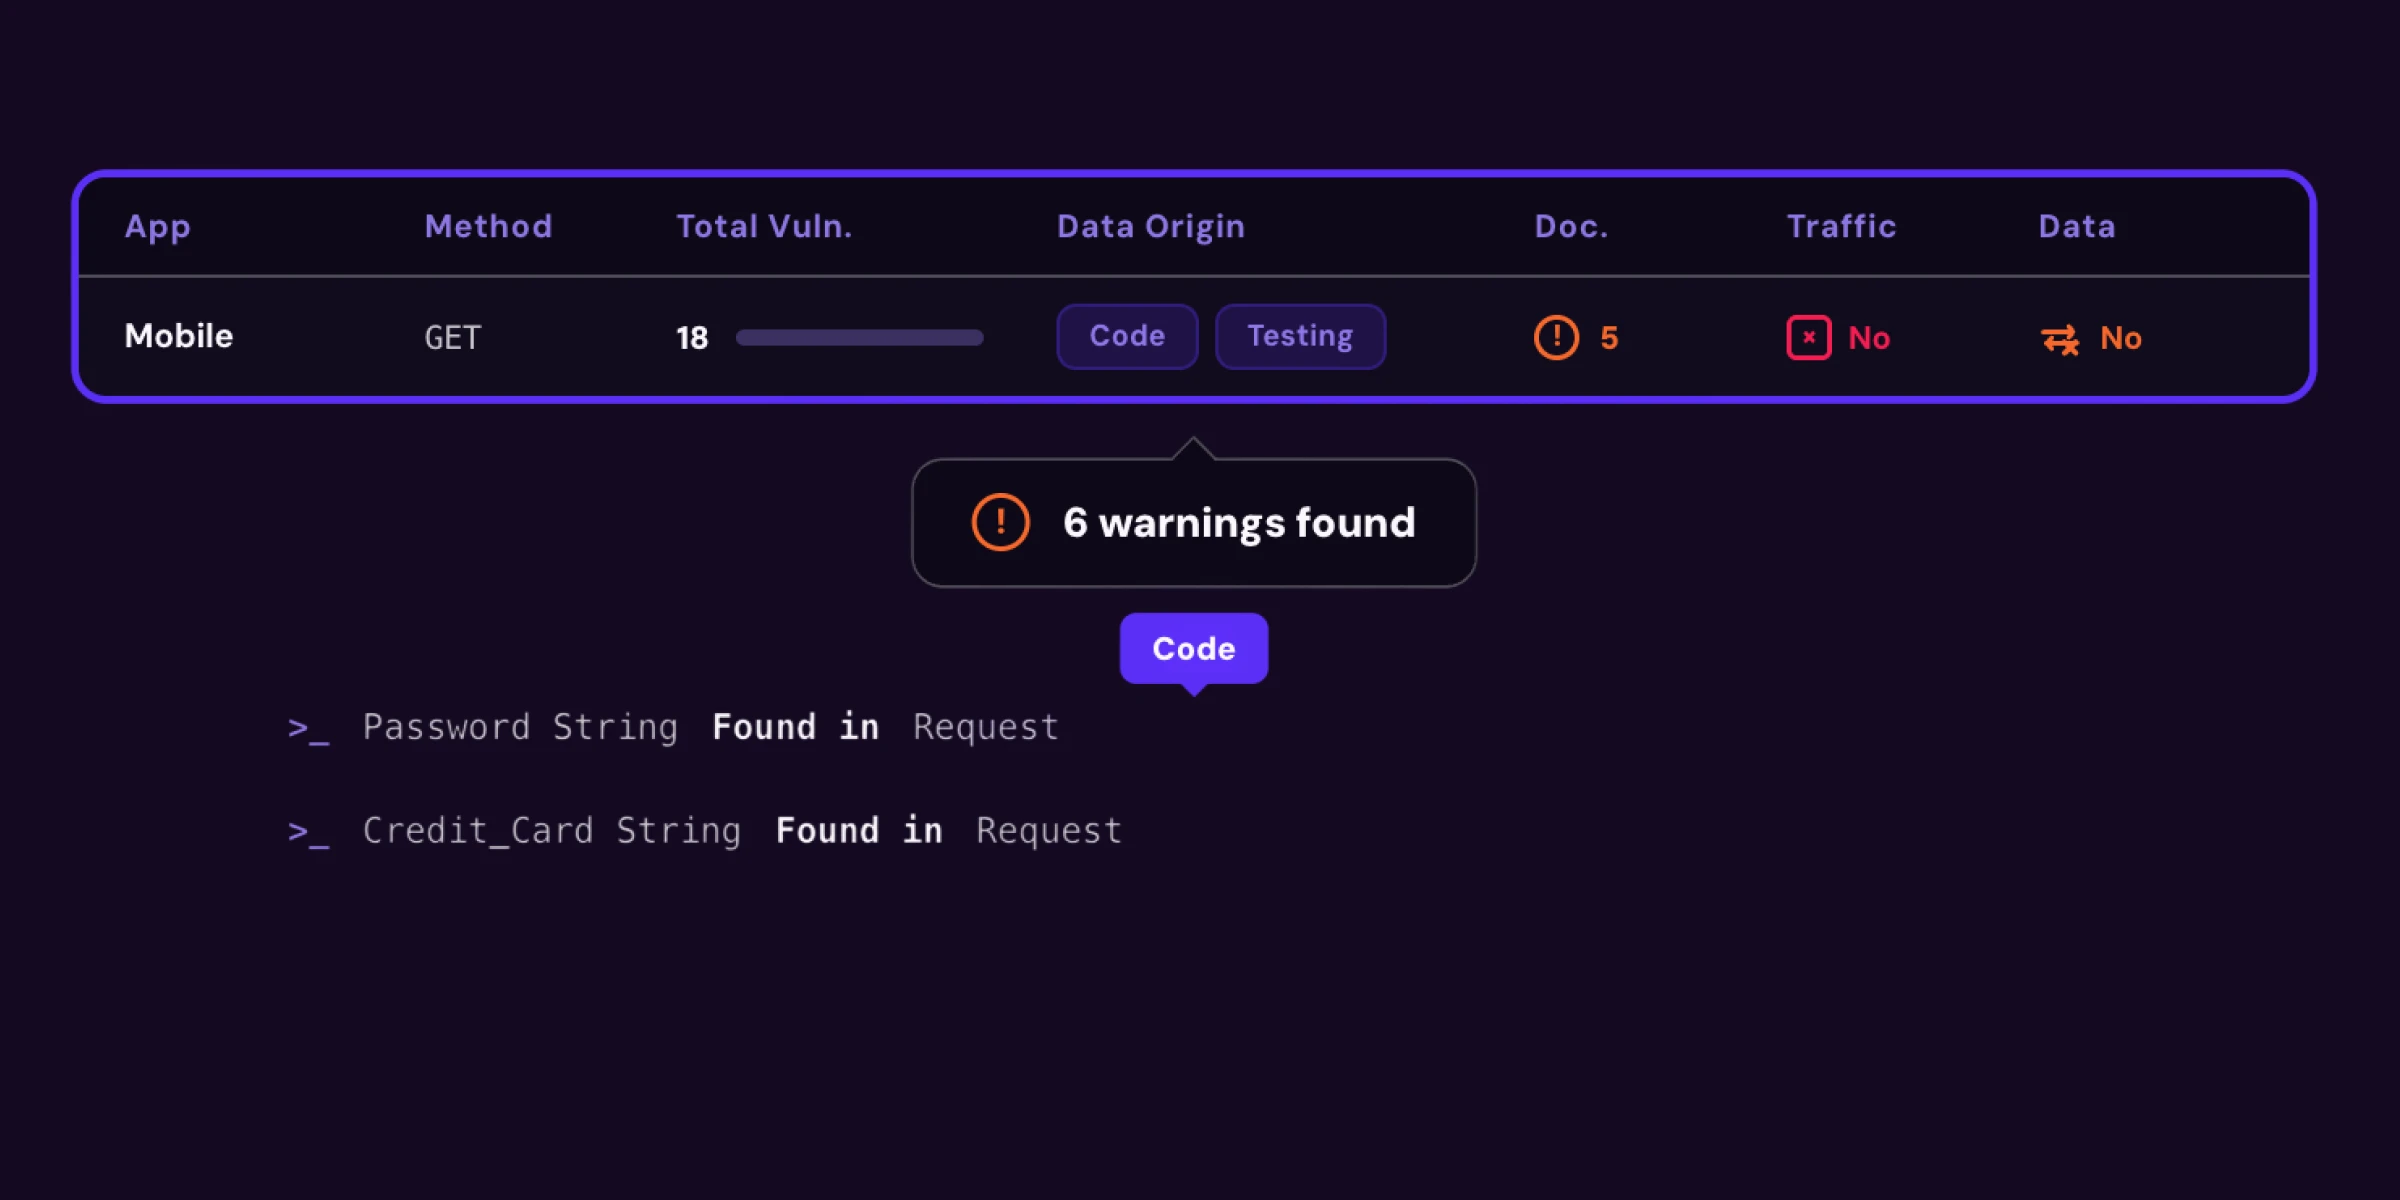
API Change Log
See the full history of every API change to better understand how risks were introduced across the entire API lifecycle. When a vulnerability surfaces, the change log shows exactly which commit introduced it, which developer made the change, and what the API looked like before – so remediation is fast and precise.
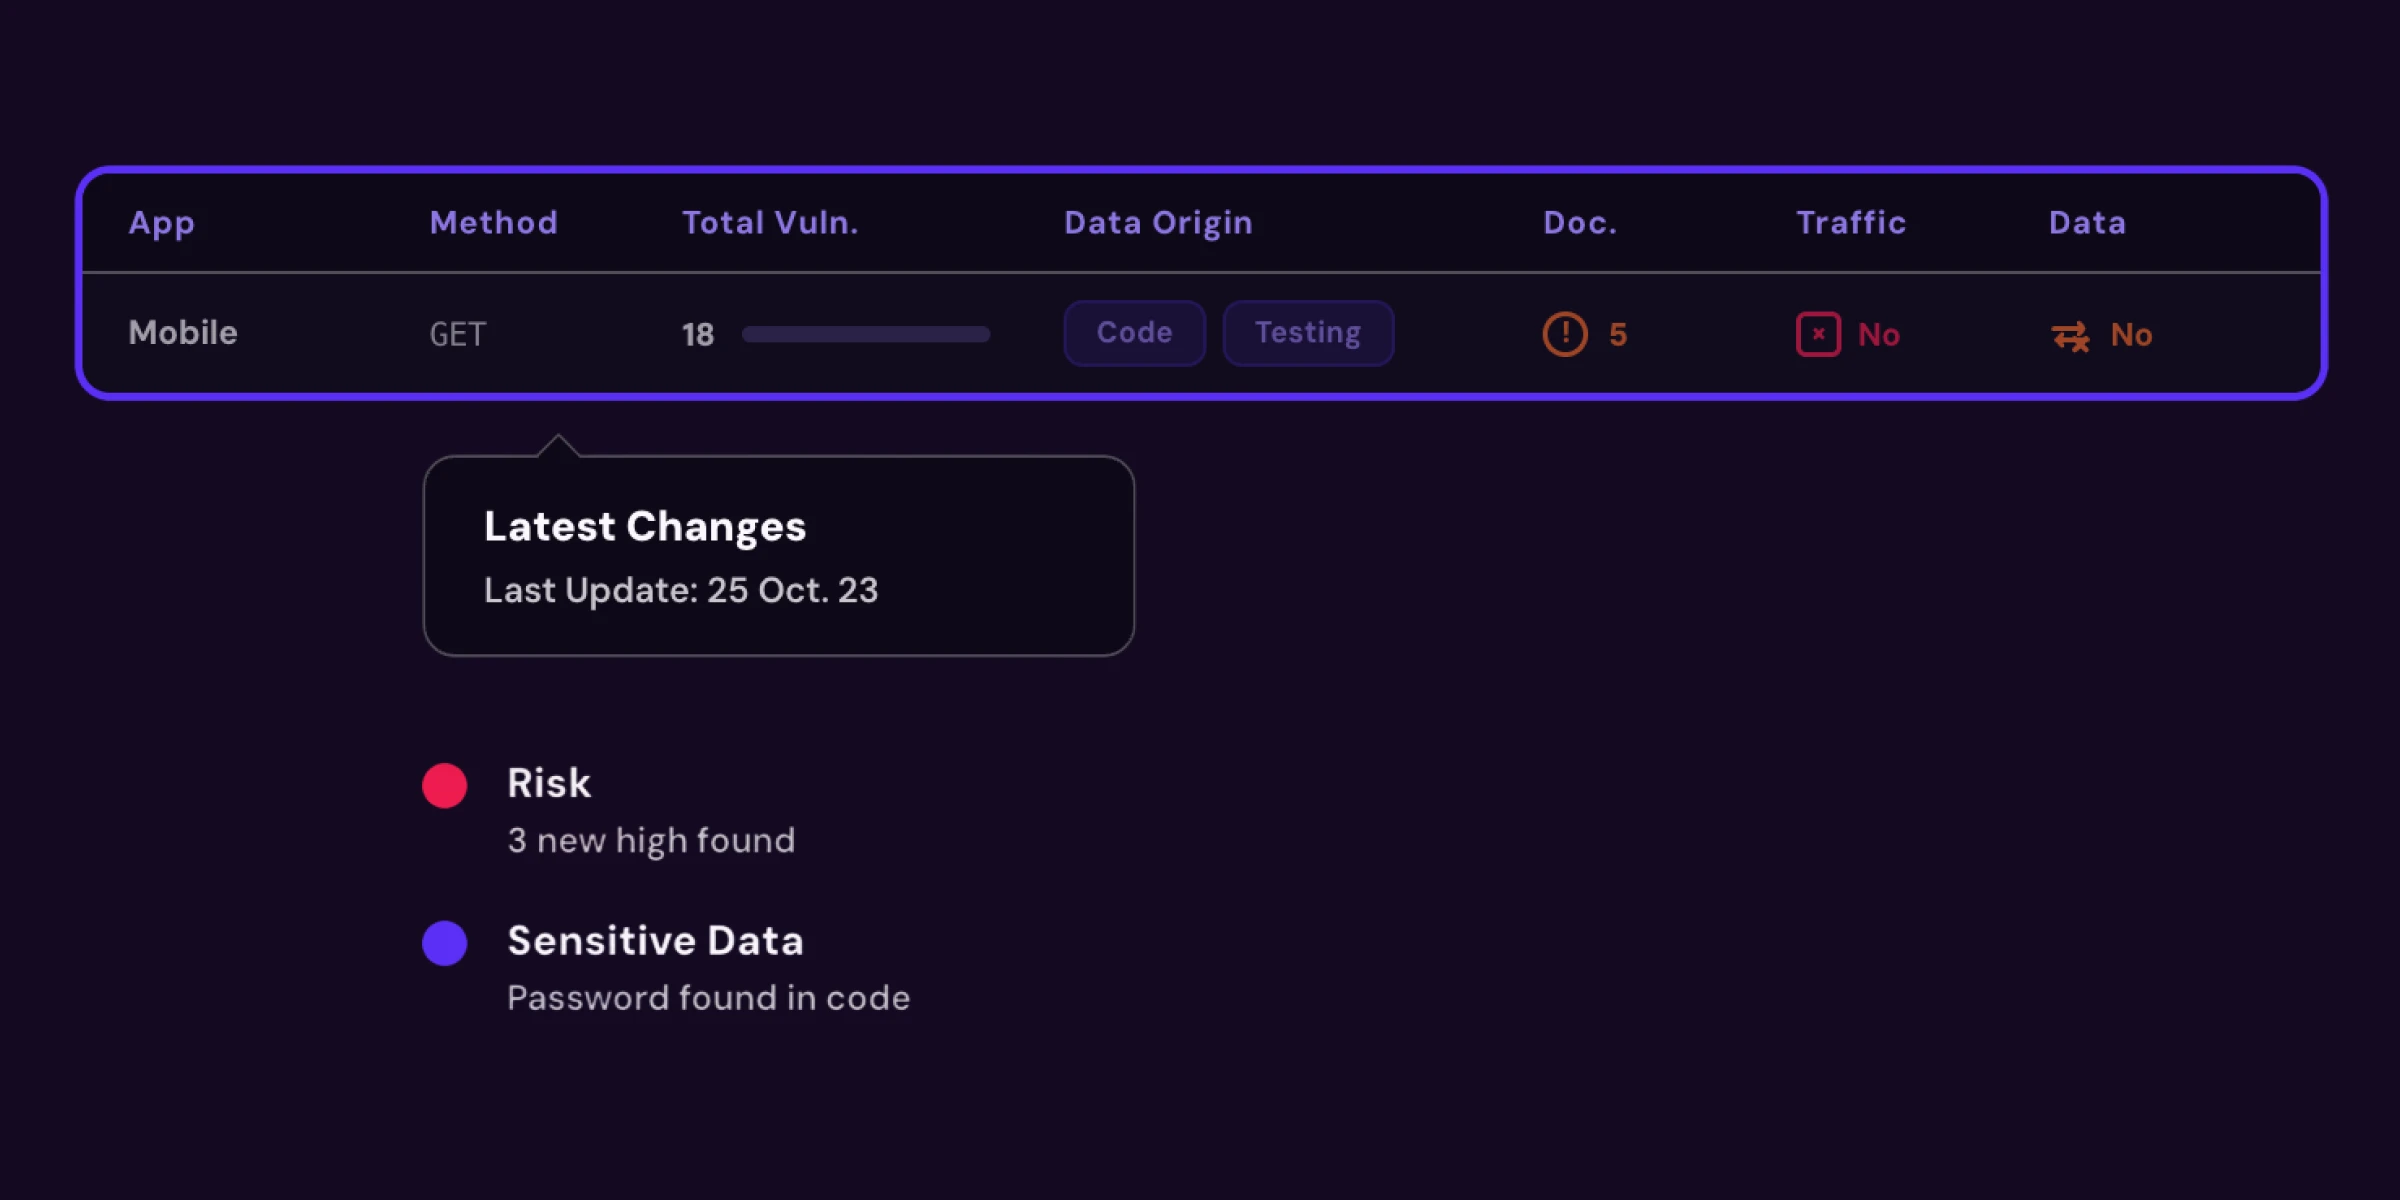
DAST Integration
Integration with Checkmarx DAST allows you to see vulnerabilities discovered by both SAST and DAST in the unified API inventory. Correlate static code findings with dynamic runtime testing for the most comprehensive view of API risk – eliminating the blind spots that come from running each tool in isolation.
Shift Left.
Integrate Right.
Traditional API security tools work at runtime – configuring protection after deployment. Checkmarx starts in the code, then connects to dynamic testing for comprehensive coverage that no single approach can match.

API Security in the Code
Checkmarx scans source code to discover every API, including shadow and zombie APIs that WAFs can never see. Vulnerabilities are found and fixed before they reach production – where they’re hardest to address.

Correlated Runtime API Testing
By correlating with DAST results, Checkmarx confirms which static findings are genuinely exploitable at runtime – providing the most accurate, prioritized API risk picture in a single platform.
You Can’t Secure
What You Can’t See
Checkmarx API Security is the only solution that provides complete visibility into your API footprint — discovering APIs at the source, including the shadow and zombie APIs that have no documentation at all.


Enterprise API Security Solution Benefits
API Security allows your organization to discover and view all your APIs, and prioritize remediation by business risk.

Mitigate API Risk Faster
Discover and assess APIs throughout the lifecycle – in documentation, source code, and dynamic testing – to address risks efficiently. Find vulnerabilities in development, not after a breach.

Prioritized API vulnerabilities Remediation
Focus your AppSec teams and developers on the most critical issues by prioritizing API vulnerabilities based on business value and risk – not just CVSS scores that treat all APIs equally.

Complete API Visibility
Always have the most accurate and up-to-date view of the entire API attack surface, eliminating data discrepancies and exposing shadow and zombie APIs that traditional tools miss entirely.
Why the World’s Top Teams Choose Checkmarx
“We’ve seen an 80% noise reduction — our engineers now focus on the high-quality risks that matter.”Explore Best Buy Case Study
“By far the best AppSec tooling decision we have made”
“Checkmarx gave us a 90% reduction in vulnerabilities in just a few months.”
“Unifying our AppSec tools with Checkmarx gave us a single source of truth.”
“With 2.1B lines of code scanned monthly, Checkmarx gives us the scale and speed we need.”
“Checkmarx fits seamlessly into our DevOps pipelines—it’s a truly scalable solution.”
“From a buyer perspective, Checkmarx’s approach offers a structured and role-aware entry point into agentic security. ”
“Incorporating Checkmarx’s technology has revolutionized our development culture ”
“Checkmarx One made our security team and developers life easier.”
“The success of our AppSec program can be directly attributed to the tooling, processes and support provided by the Checkmarx managed services.”
“Bringing ASPM context directly into the IDE reflects a forward-looking approach to prioritizing security efforts based on risk earlier in the development process.”
Frequently Asked Questions
API security is the practice of preventing and mitigating attacks on APIs. It is a rapidly growing segment within application security, increasing alongside the growing use of APIs in applications, as well as the sensitive data that APIs often transfer. APIs are now the most common attack vector in modern web applications.
Traditionally, organizations secured APIs using an API gateway or web application firewall (WAF). However, these solutions require AppSec teams to configure protection for each individual API using documentation such as Swagger files, and therefore cannot protect shadow or zombie APIs. Checkmarx shifts left to secure APIs, scanning application source code to discover and inventory every API defined in the application — including undocumented, shadow, and zombie APIs. Then we integrate right, correlating API insights with DAST to help customers better protect live APIs.
A shadow API is another name for an undocumented API. Traditional API security solutions — like WAFs and API gateways — require documentation to configure protection. They cannot protect what they don’t know exists. AppSec teams are often not aware of these APIs, which is why they’re called shadow APIs. Checkmarx discovers them by scanning source code directly, making documentation optional.
A zombie API is an API that has been abandoned or forgotten. Organizations can inadvertently create zombie APIs when releasing a new API version — they leave the original version in production temporarily to ease migration, then forget to decommission it. These abandoned endpoints remain live, often with outdated security controls, making them attractive targets for attackers who know legacy systems are rarely monitored.
The OWASP API Security Top 10 is a list of the most critical API security risks, including Broken Object Level Authorization (BOLA/IDOR), Broken Authentication, Excessive Data Exposure, and others. Checkmarx API Security detects vulnerabilities mapped to these categories during SAST scanning of API code, helping organizations address the most common and dangerous API weaknesses before they reach production.
Checkmarx API Security integrates natively with Checkmarx DAST within the Checkmarx One platform. SAST findings from static code analysis are correlated with DAST findings from dynamic runtime testing to provide a unified view in the API inventory. When both tools flag the same API endpoint, the correlated finding is elevated in priority — confirming that the vulnerability is not just present in code but actively exploitable at runtime.
You Can’t Secure What You Can’t See
Talk to an AppSec expert about Checkmarx API Security. We’ll respond within 1 business day.
Thank You!
Your Custom Checkmarx Demo Request was Successfully Sent!
Get a Demo
Address API Issues Earlier and Faster
Don’t Miss Anything
See every API discovered from your source code – including shadow and zombie APIs that documentation-based tools miss.
Understand the History
View every API change to understand how risks were introduced and take precise corrective action with full context.
Intelligent Integration
See how correlated SAST and DAST results deliver a truly comprehensive sweep of API vulnerabilities in a single view.
Prioritize Resources
Remediate what really matters using our unmatchable inventory of every API and detected vulnerability, ranked by business risk.
Get Started with
Checkmarx API Security Today
Join a growing number of enterprises that rely on Checkmarx API Security for a holistic view into API risk — from source code to runtime, including the APIs you didn’t know existed.