
Secrets Detection
Minimize the risk of cyberattacks by preventing exposure of hardcoded passwords, access tokens, keys, and other sensitive credentials.
Detect Every Hardcoded Secret,
Before It Becomes a Breach
Checkmarx Secrets Detection goes beyond surface-level scanning – covering your entire repository history, CI/CD pipelines, IDE, and runtime environments with unmatched precision.
Powerful Secret Detection Across 170+ Types
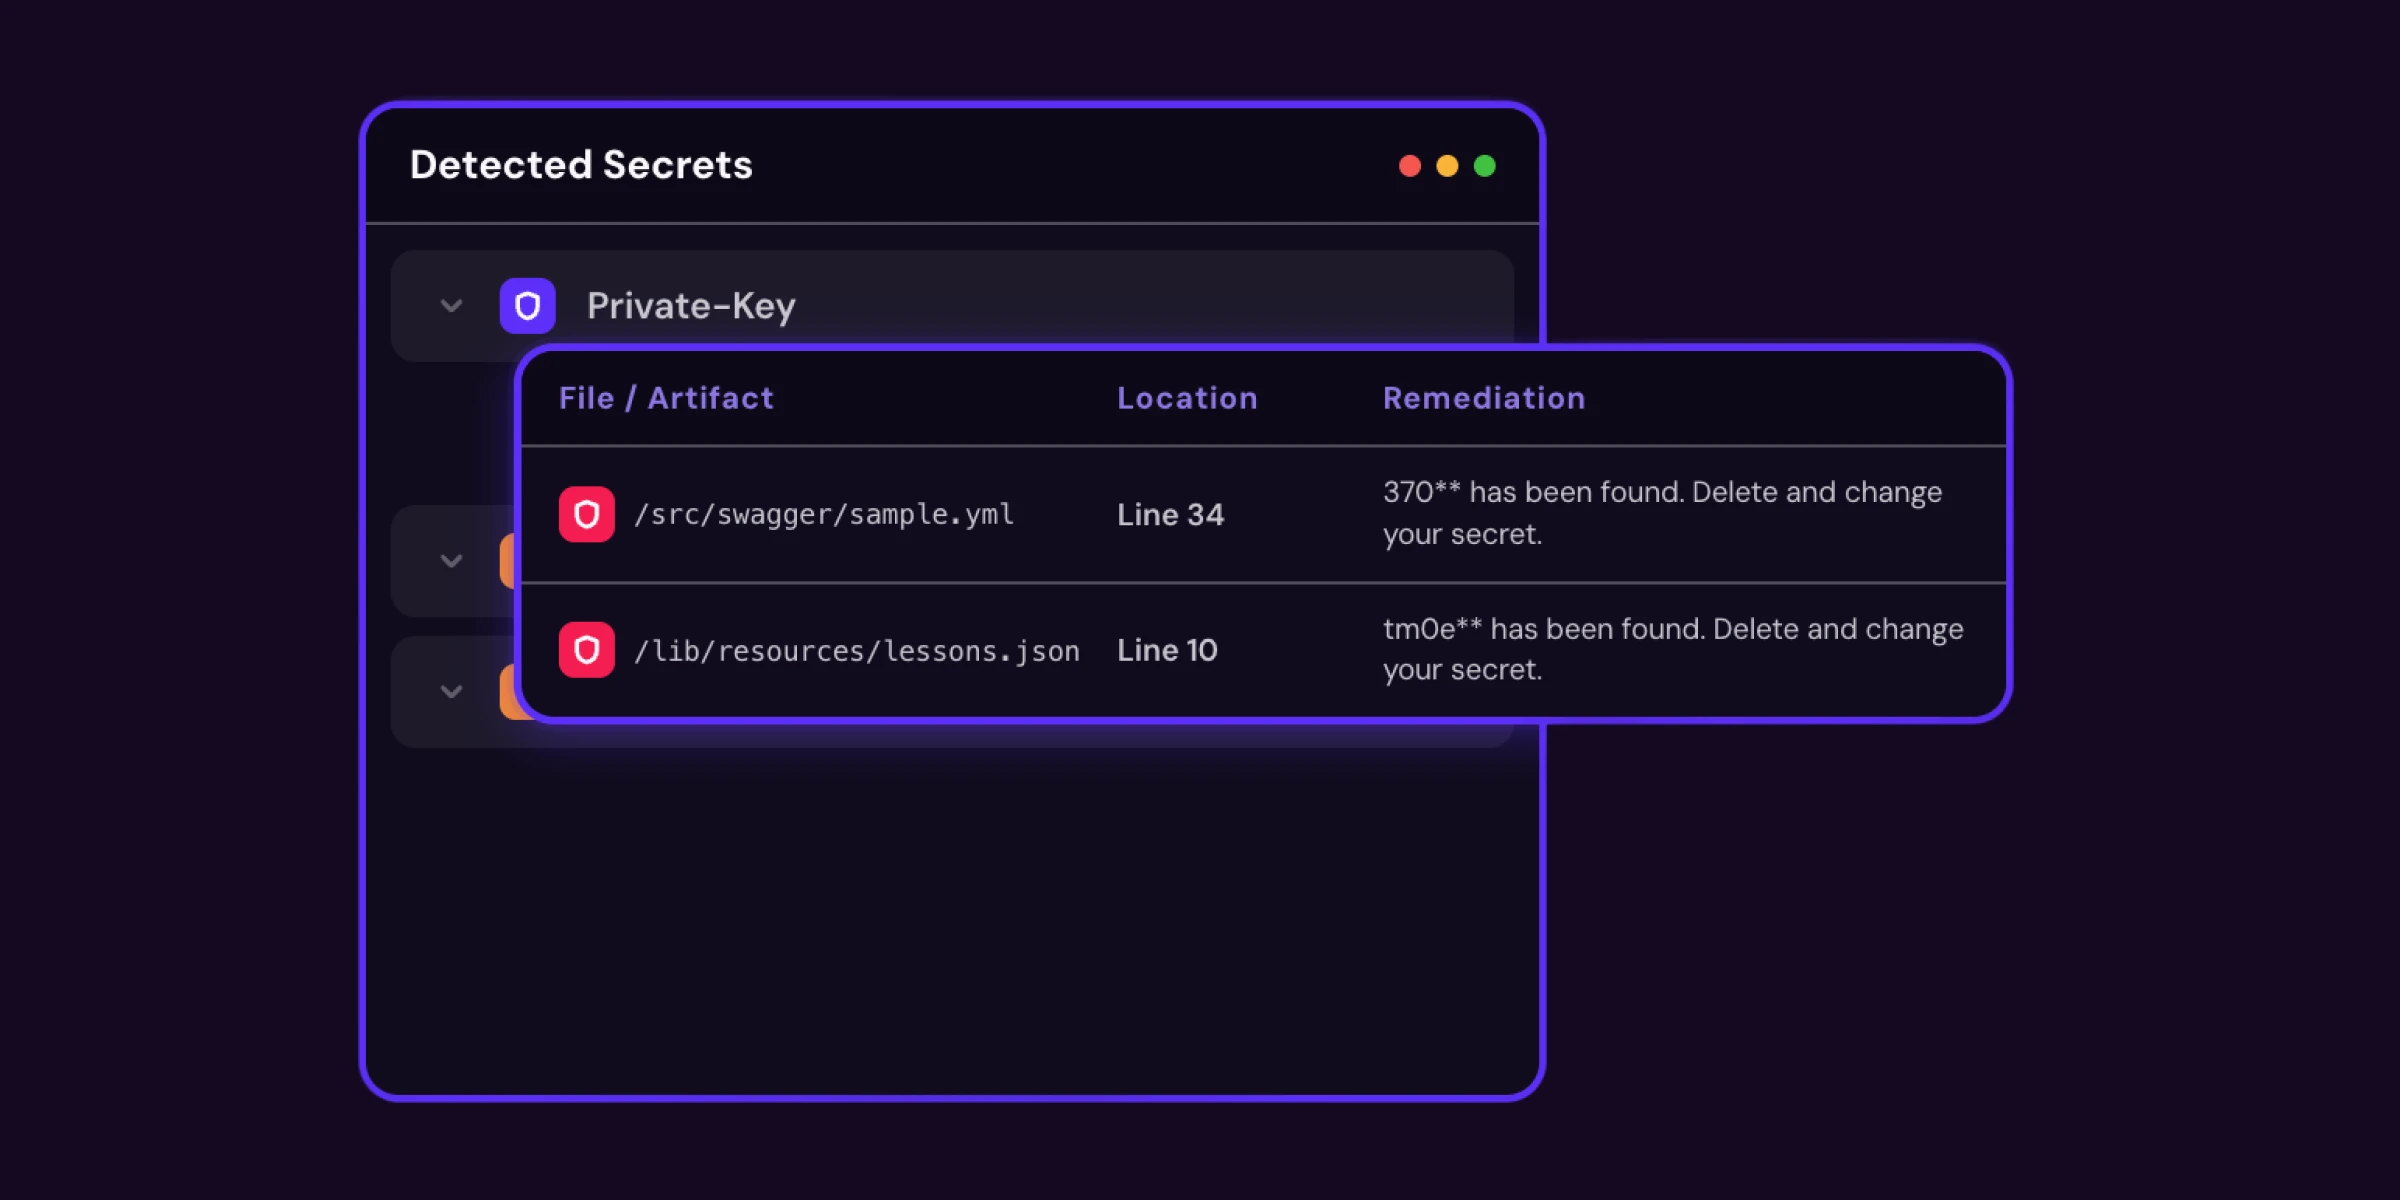
Checkmarx accurately identifies 170+ different types of login credentials, access tokens, encryption keys, API keys, SSH keys, webhook URLs, and other unsecured sensitive information.
Live Secrets Validation
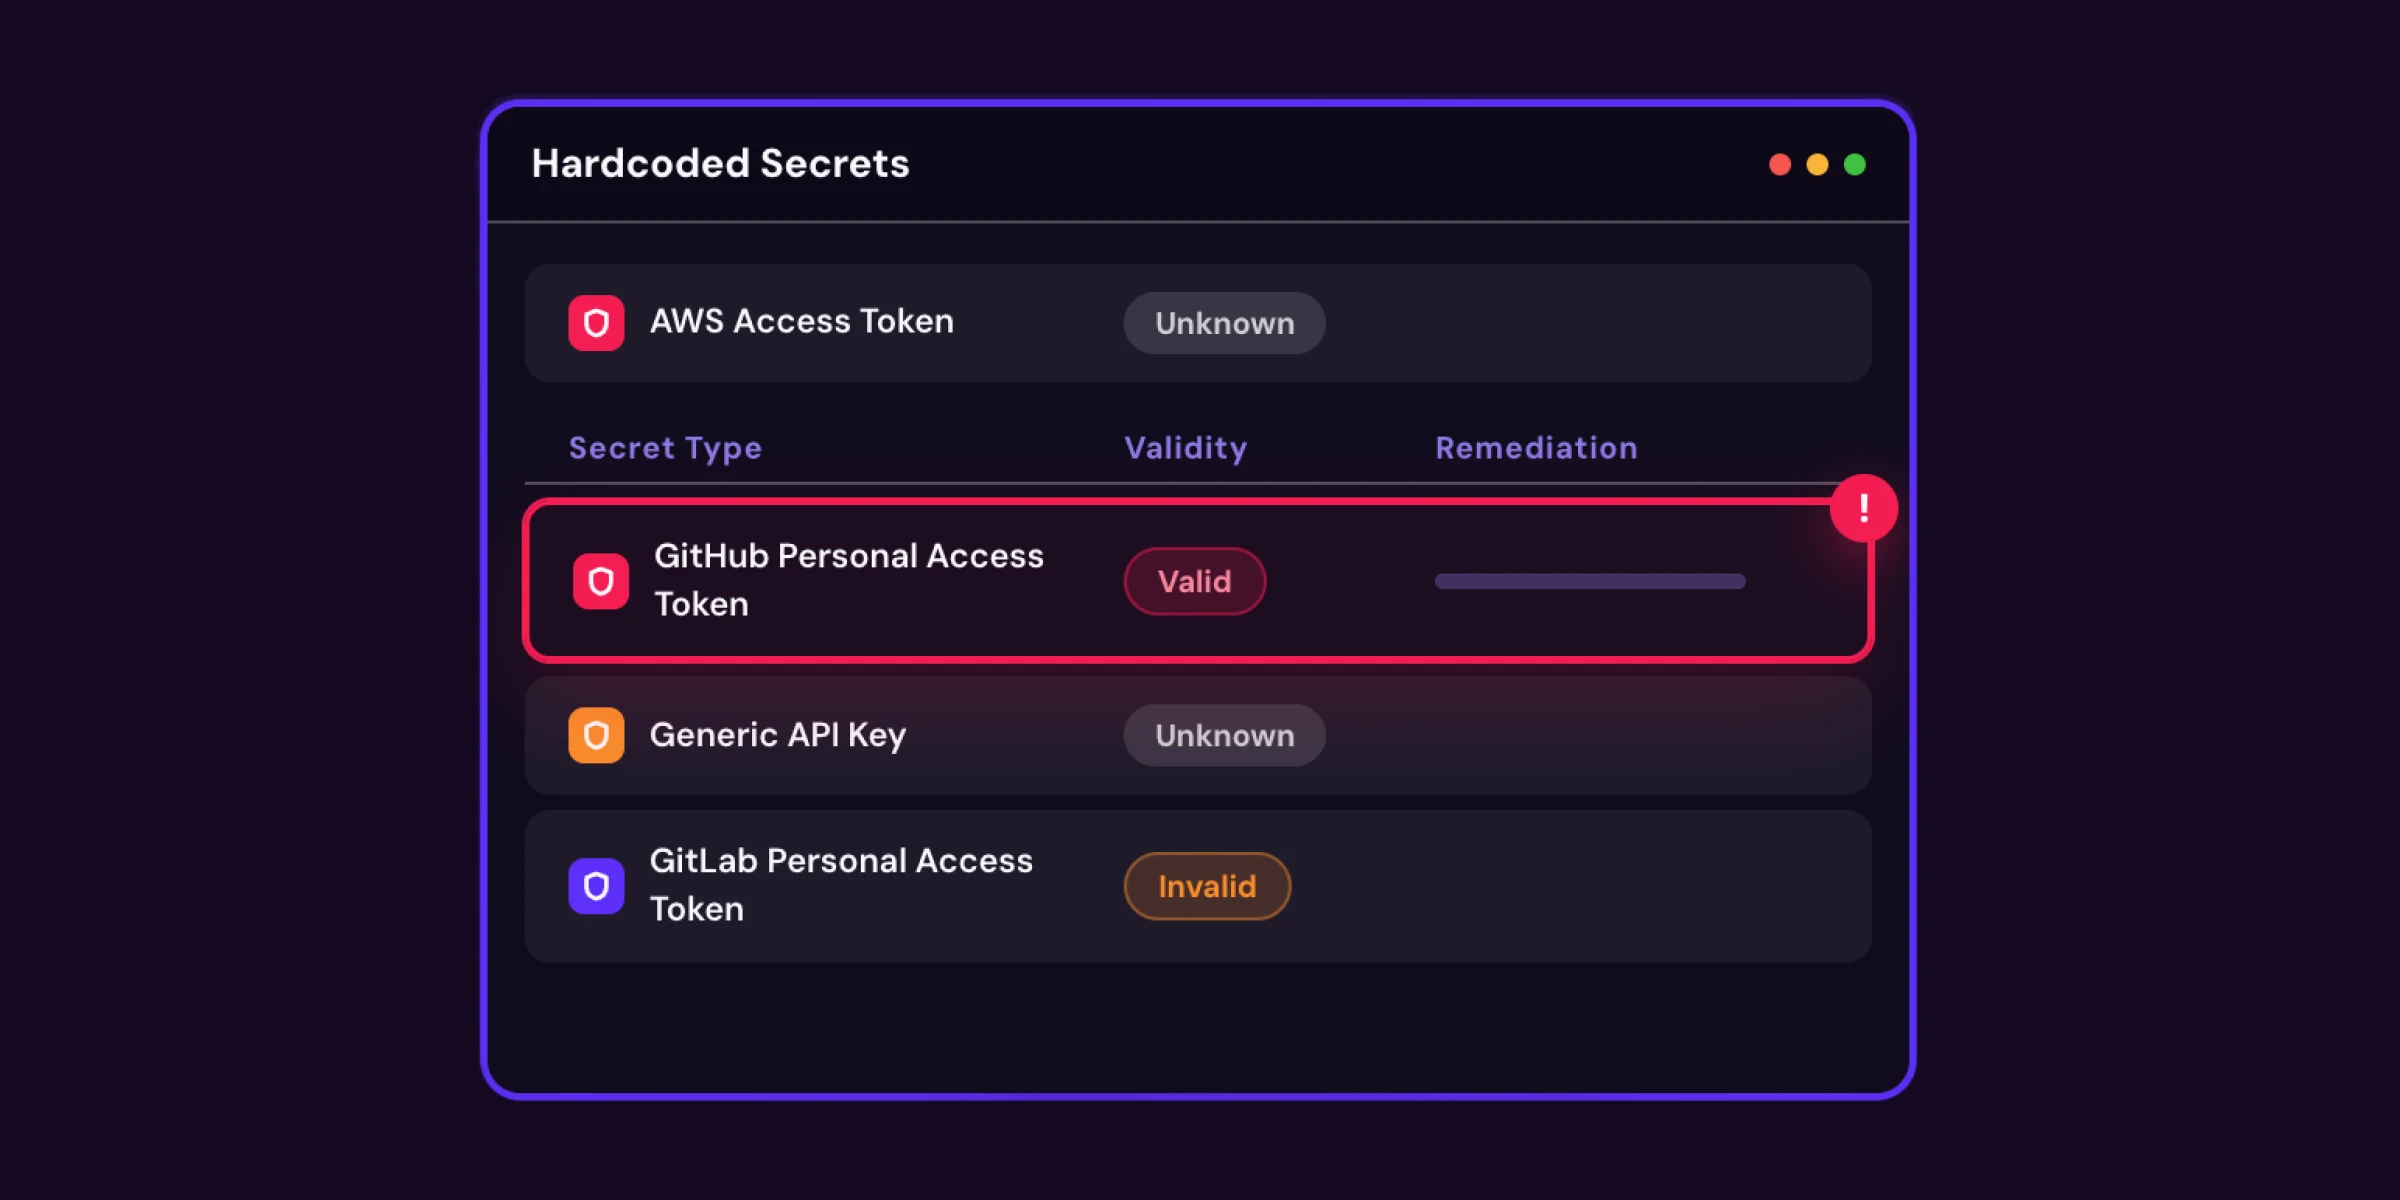
To prioritize remediation efforts, the system automatically attempts to determine if discovered secrets are still valid and thus potentially exploitable.
Pre-Commit Secrets Exposure Prevention in the IDE
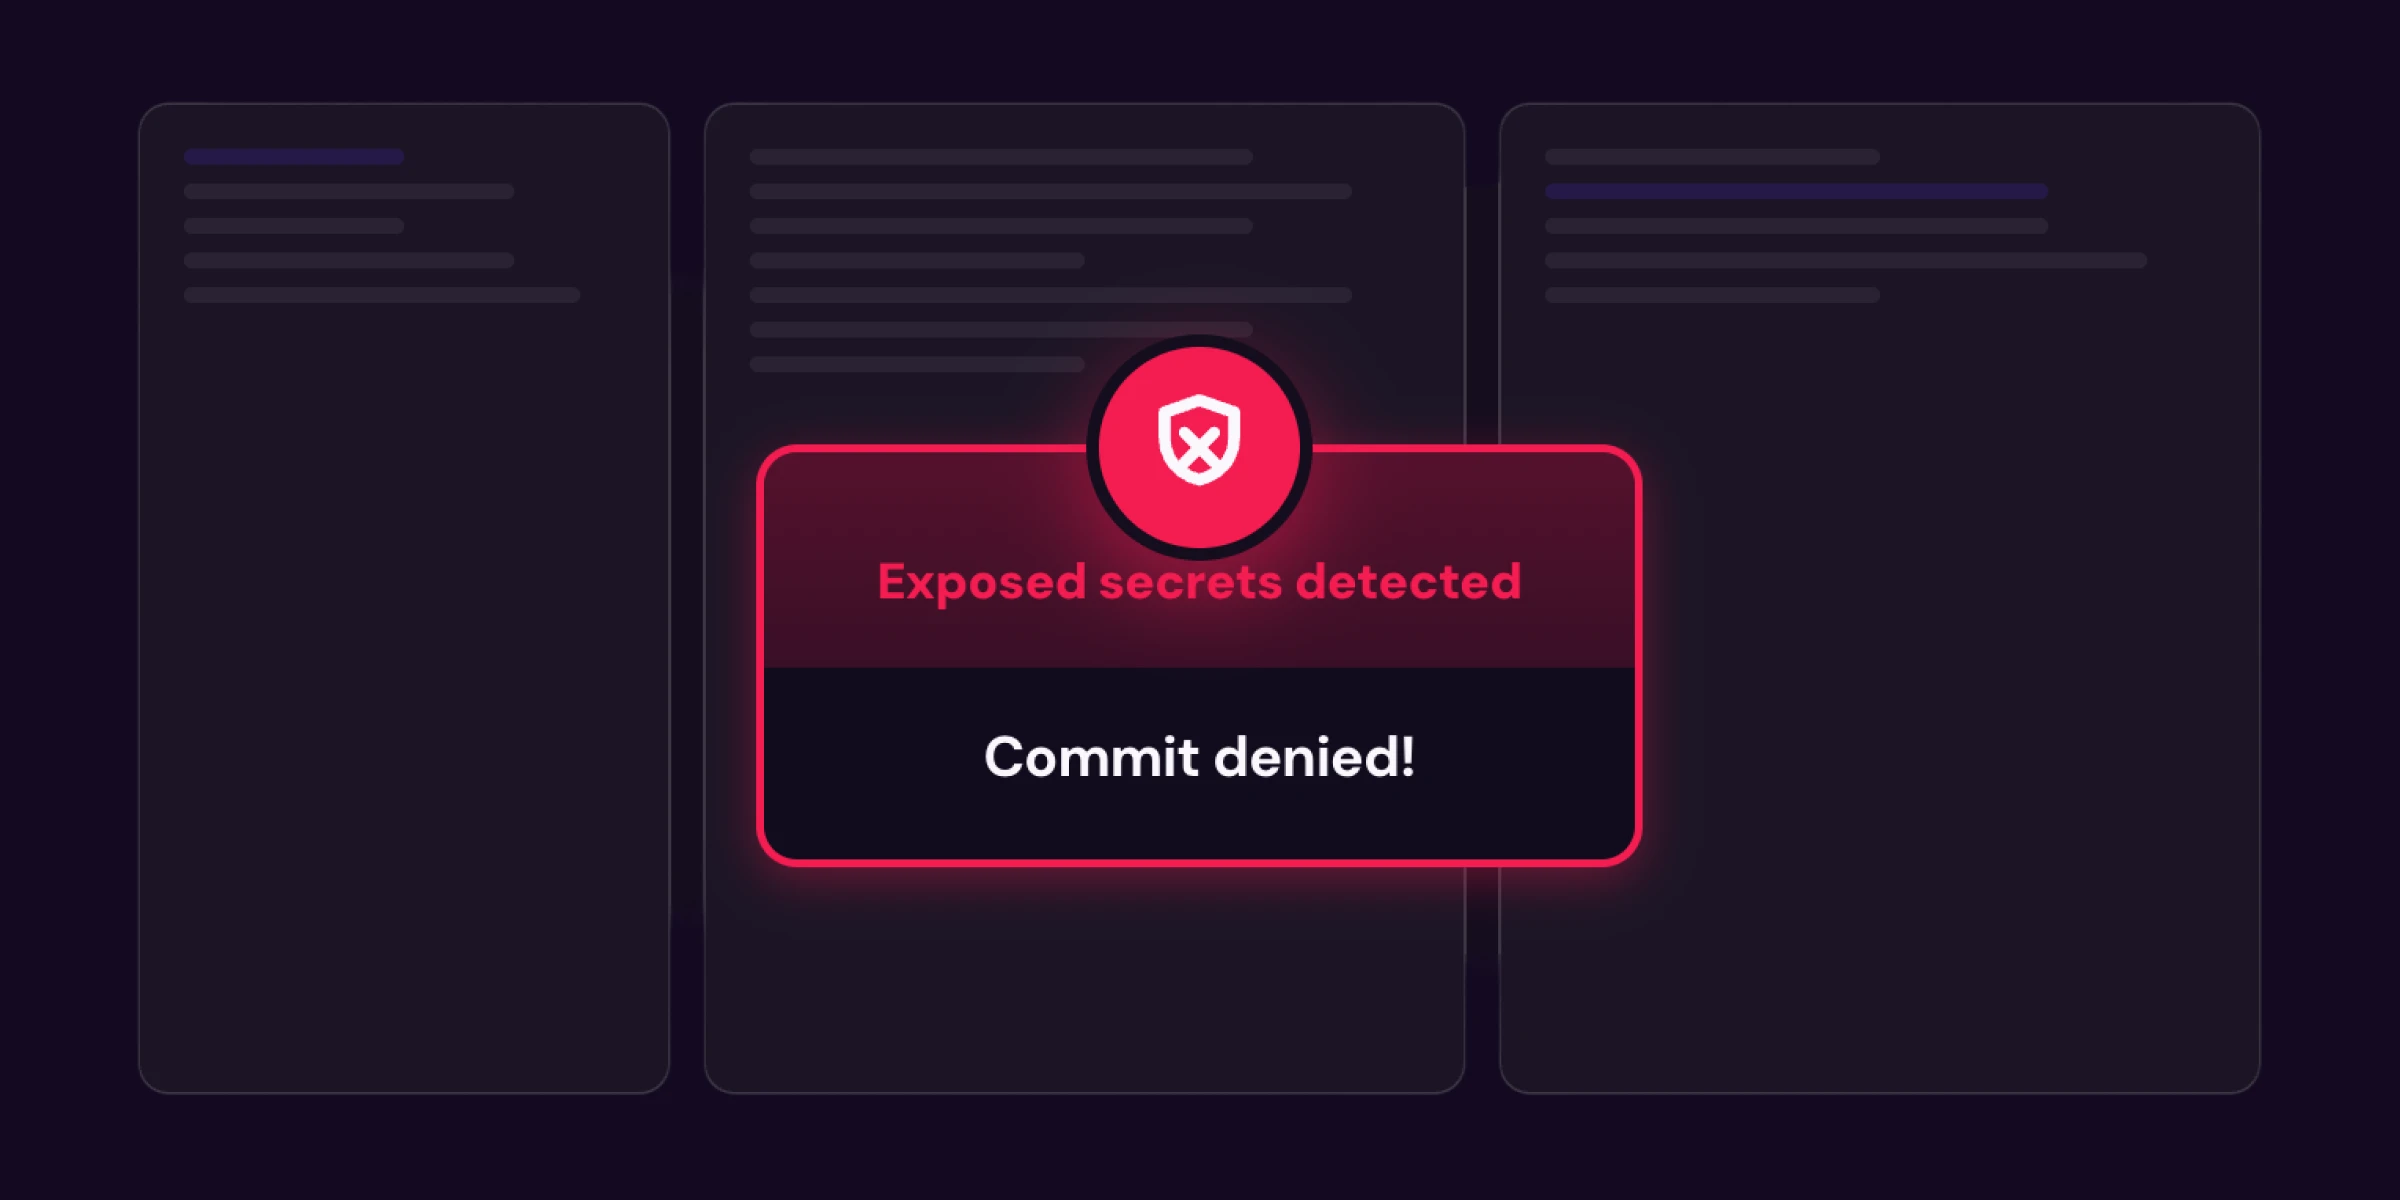
The best time to catch a secret is before it ever touches version control. Checkmarx Secrets Detection integrates directly into VS Code, IntelliJ, and other major IDEs – and into your Git pre-commit hooks – so developers are warned in real time and commits containing secrets are automatically blocked.
History Secrets Scanning
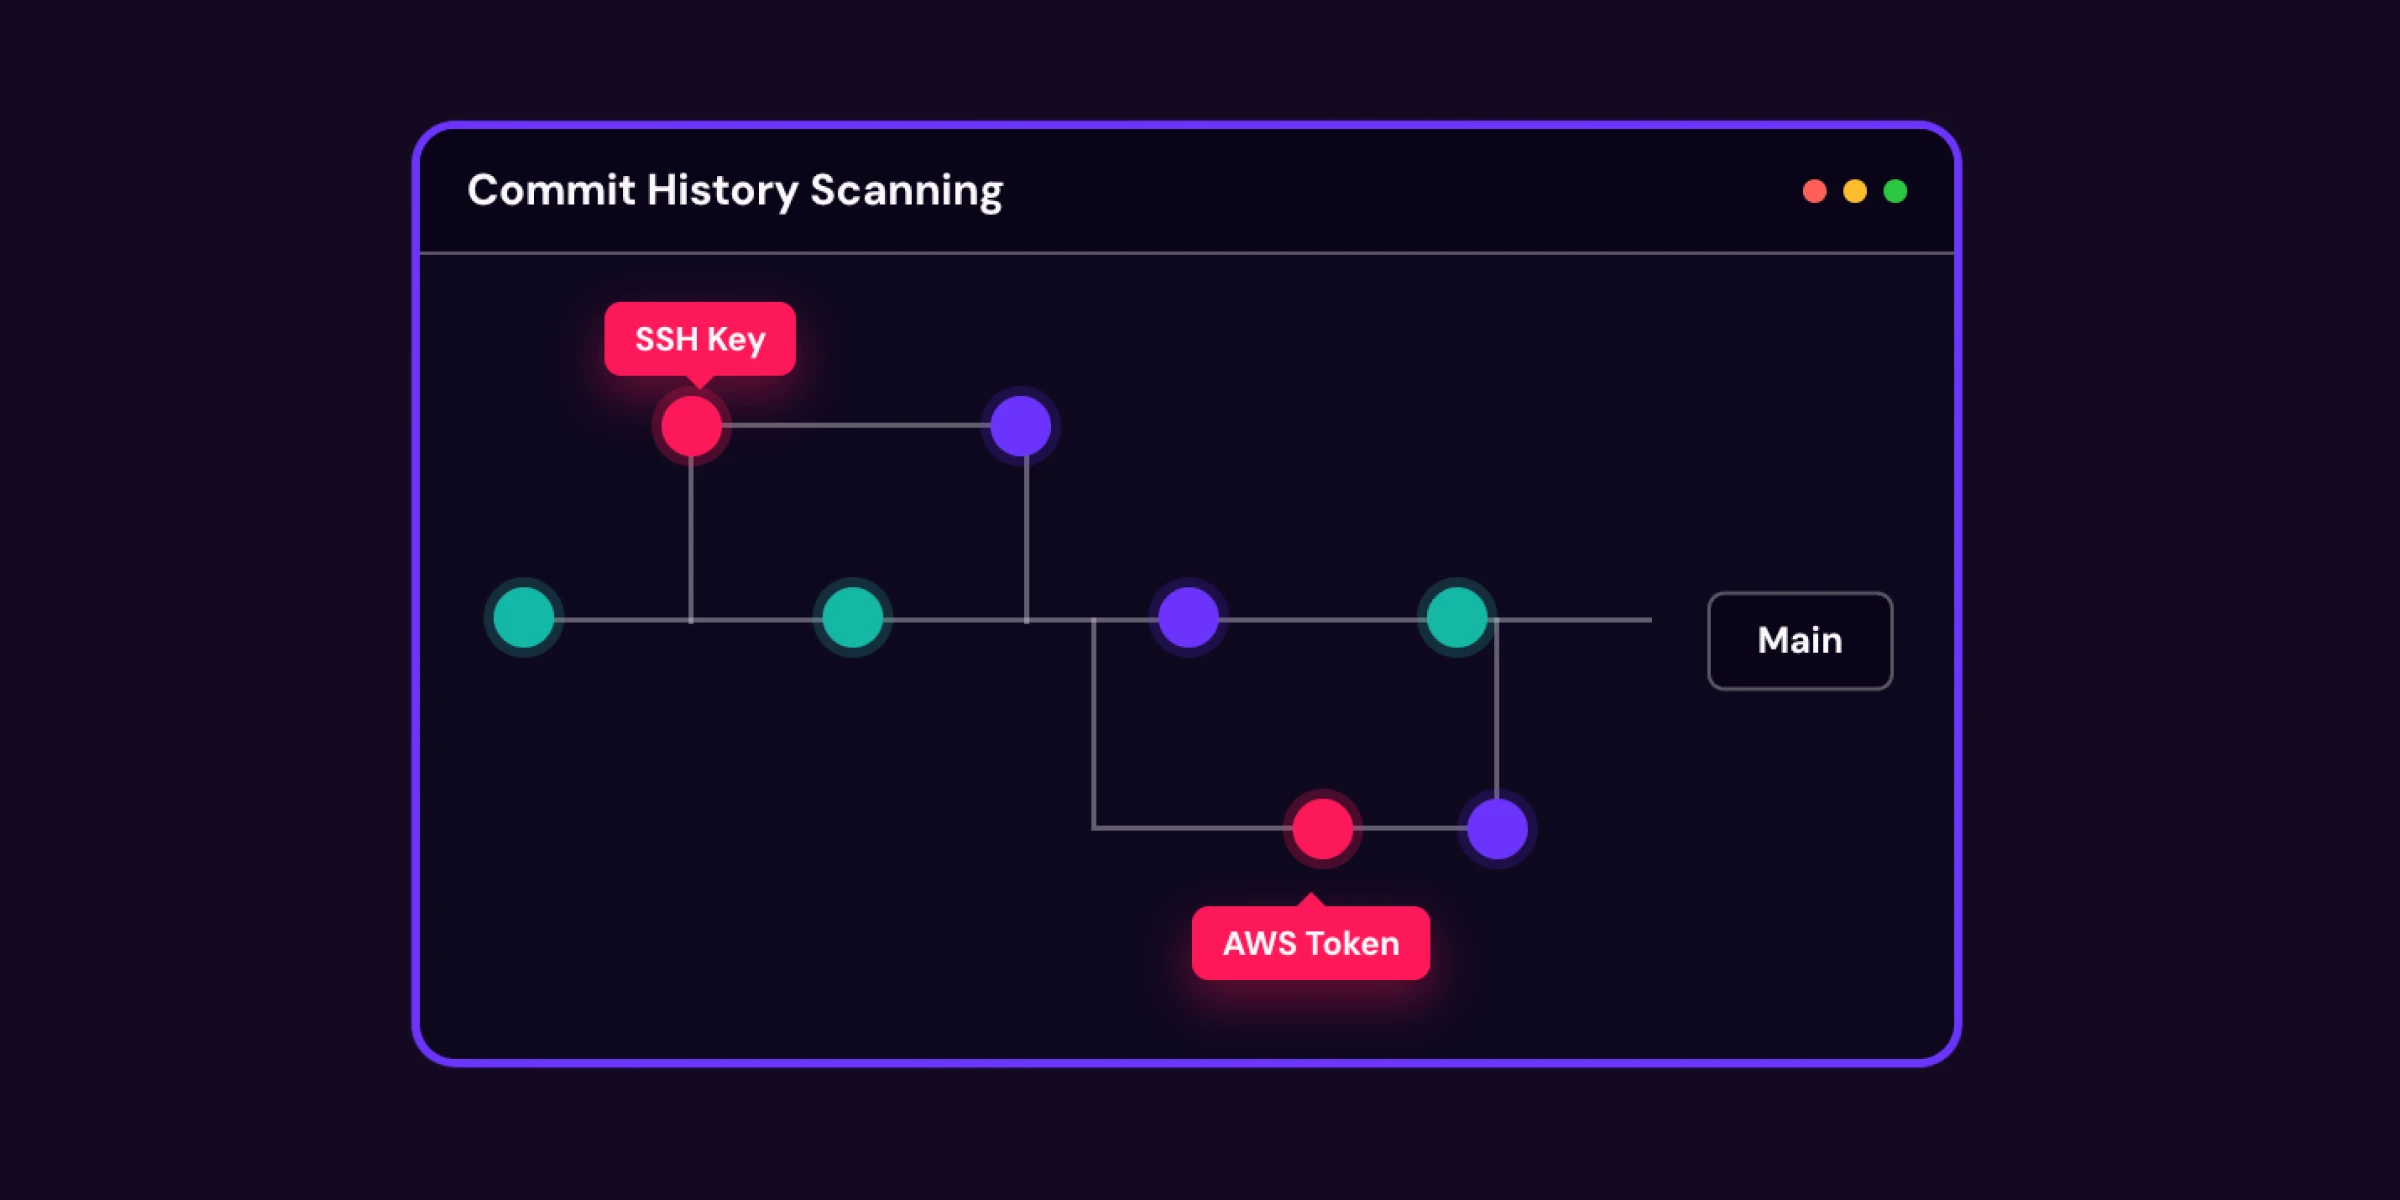
In addition to scanning current source code, Checkmarx also detects secrets hidden in historical Git commits, across both server-hosted and local developer repositories.
Developer-Friendly Workflows
Developers can initiate scans for exposed secrets, review results, and receive remediation guidance – all within their IDE. Checkmarx provides actionable, step-by-step remediation guidance for every secret type — including direct links to rotate credentials in AWS IAM, GitHub, Stripe, and other platforms — so developers can fix the issue in minutes, not hours.
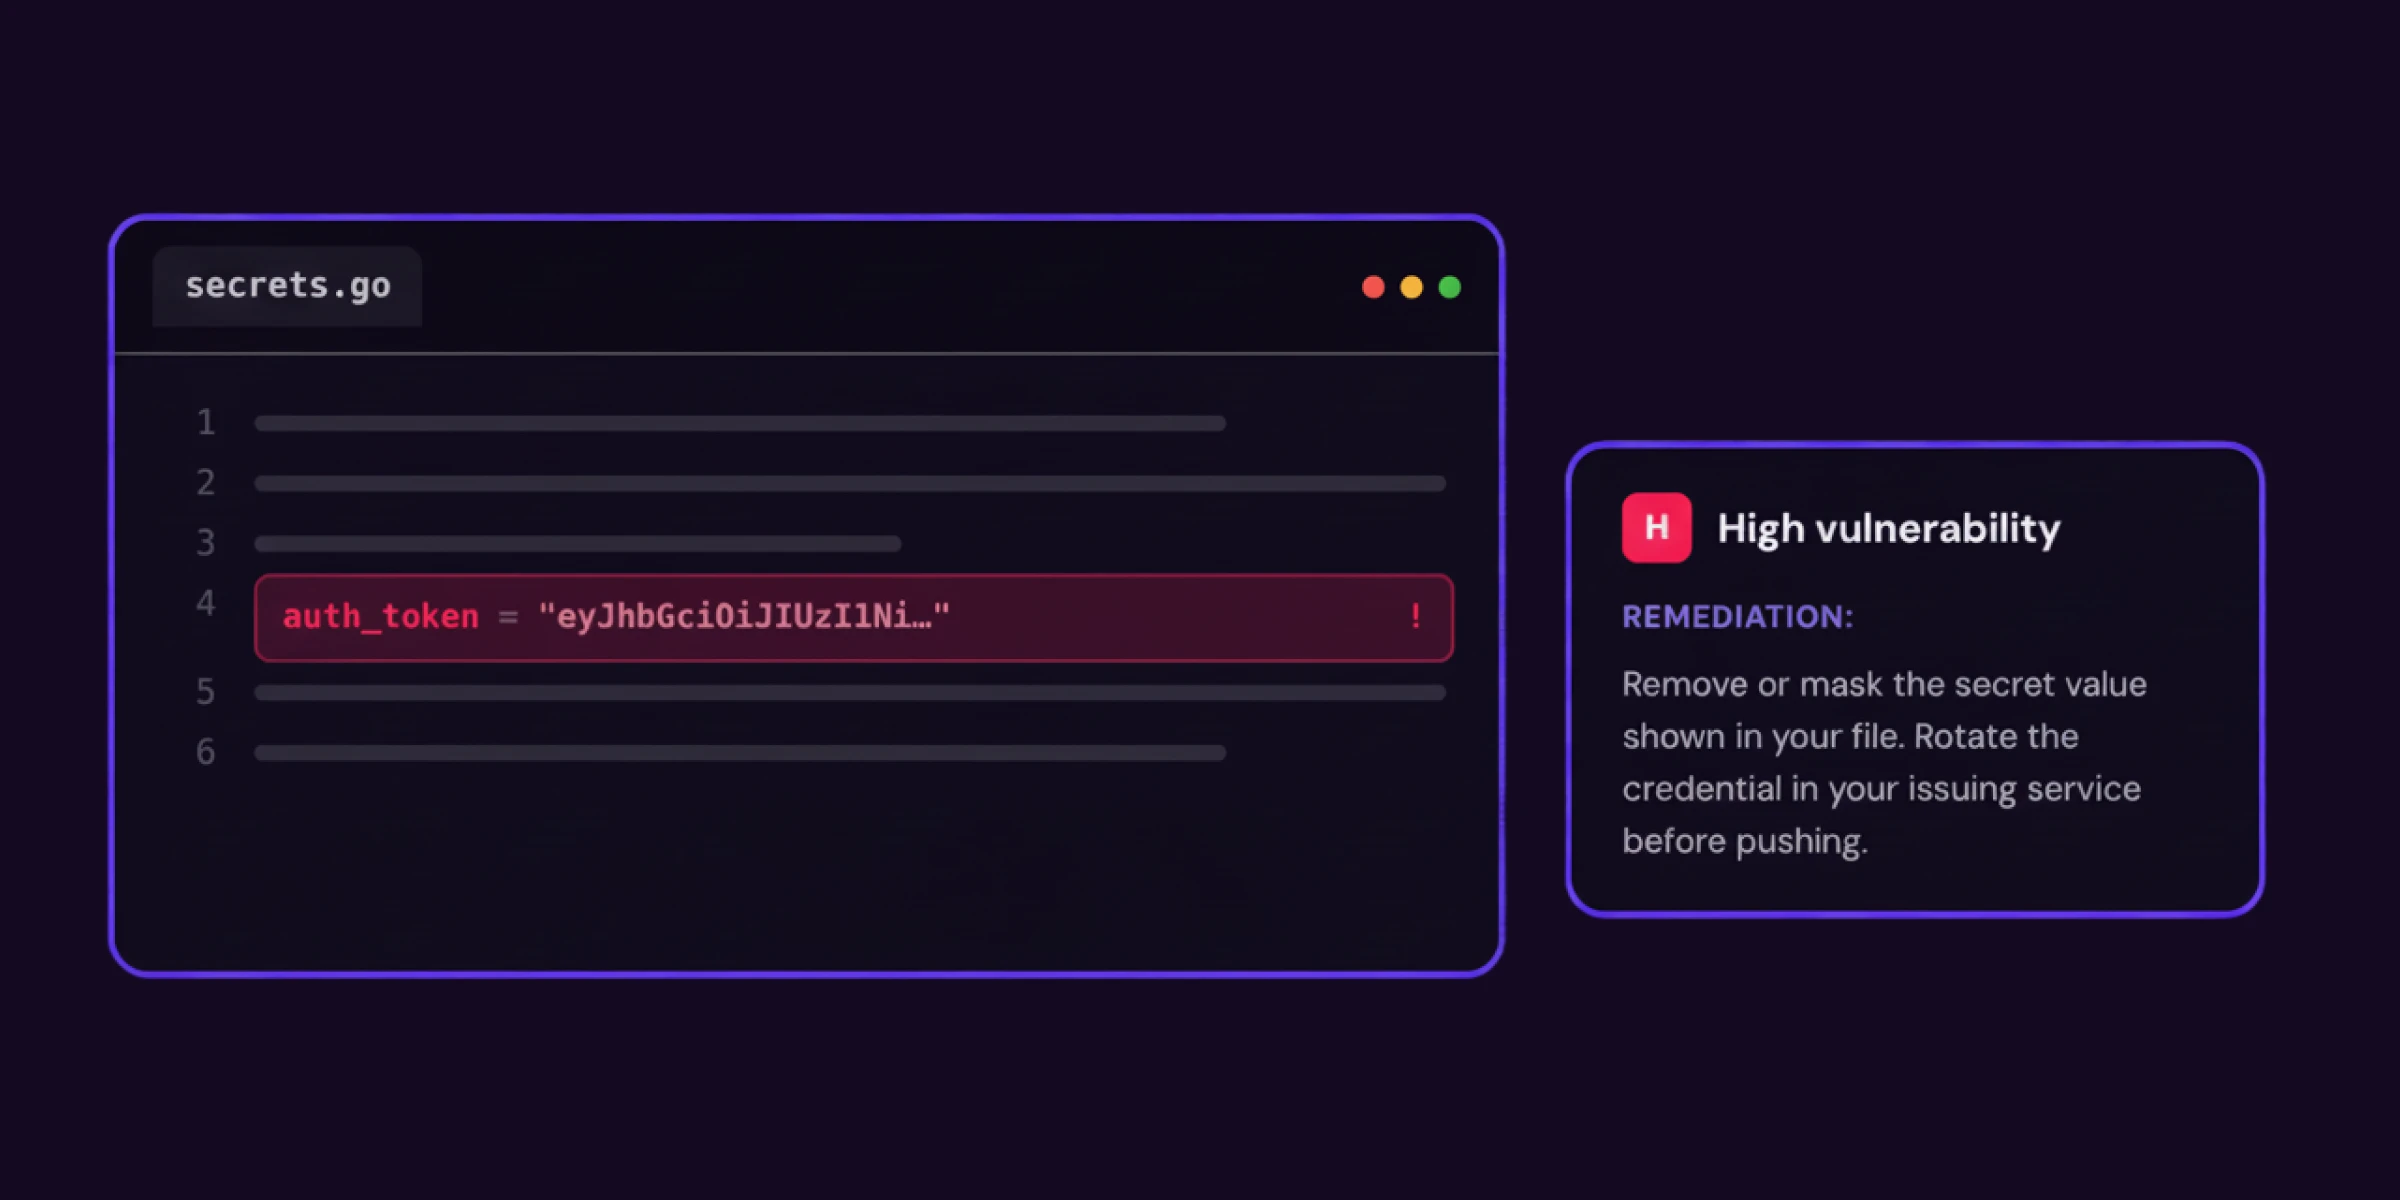
Policy Enforcement – Block PRs, Break Builds
Define policies by secret type, severity, or repository – then let Checkmarx enforce them automatically across your CI/CD pipelines. High-severity secrets block merges outright; medium findings trigger alerts and create Jira tickets for tracked remediation.
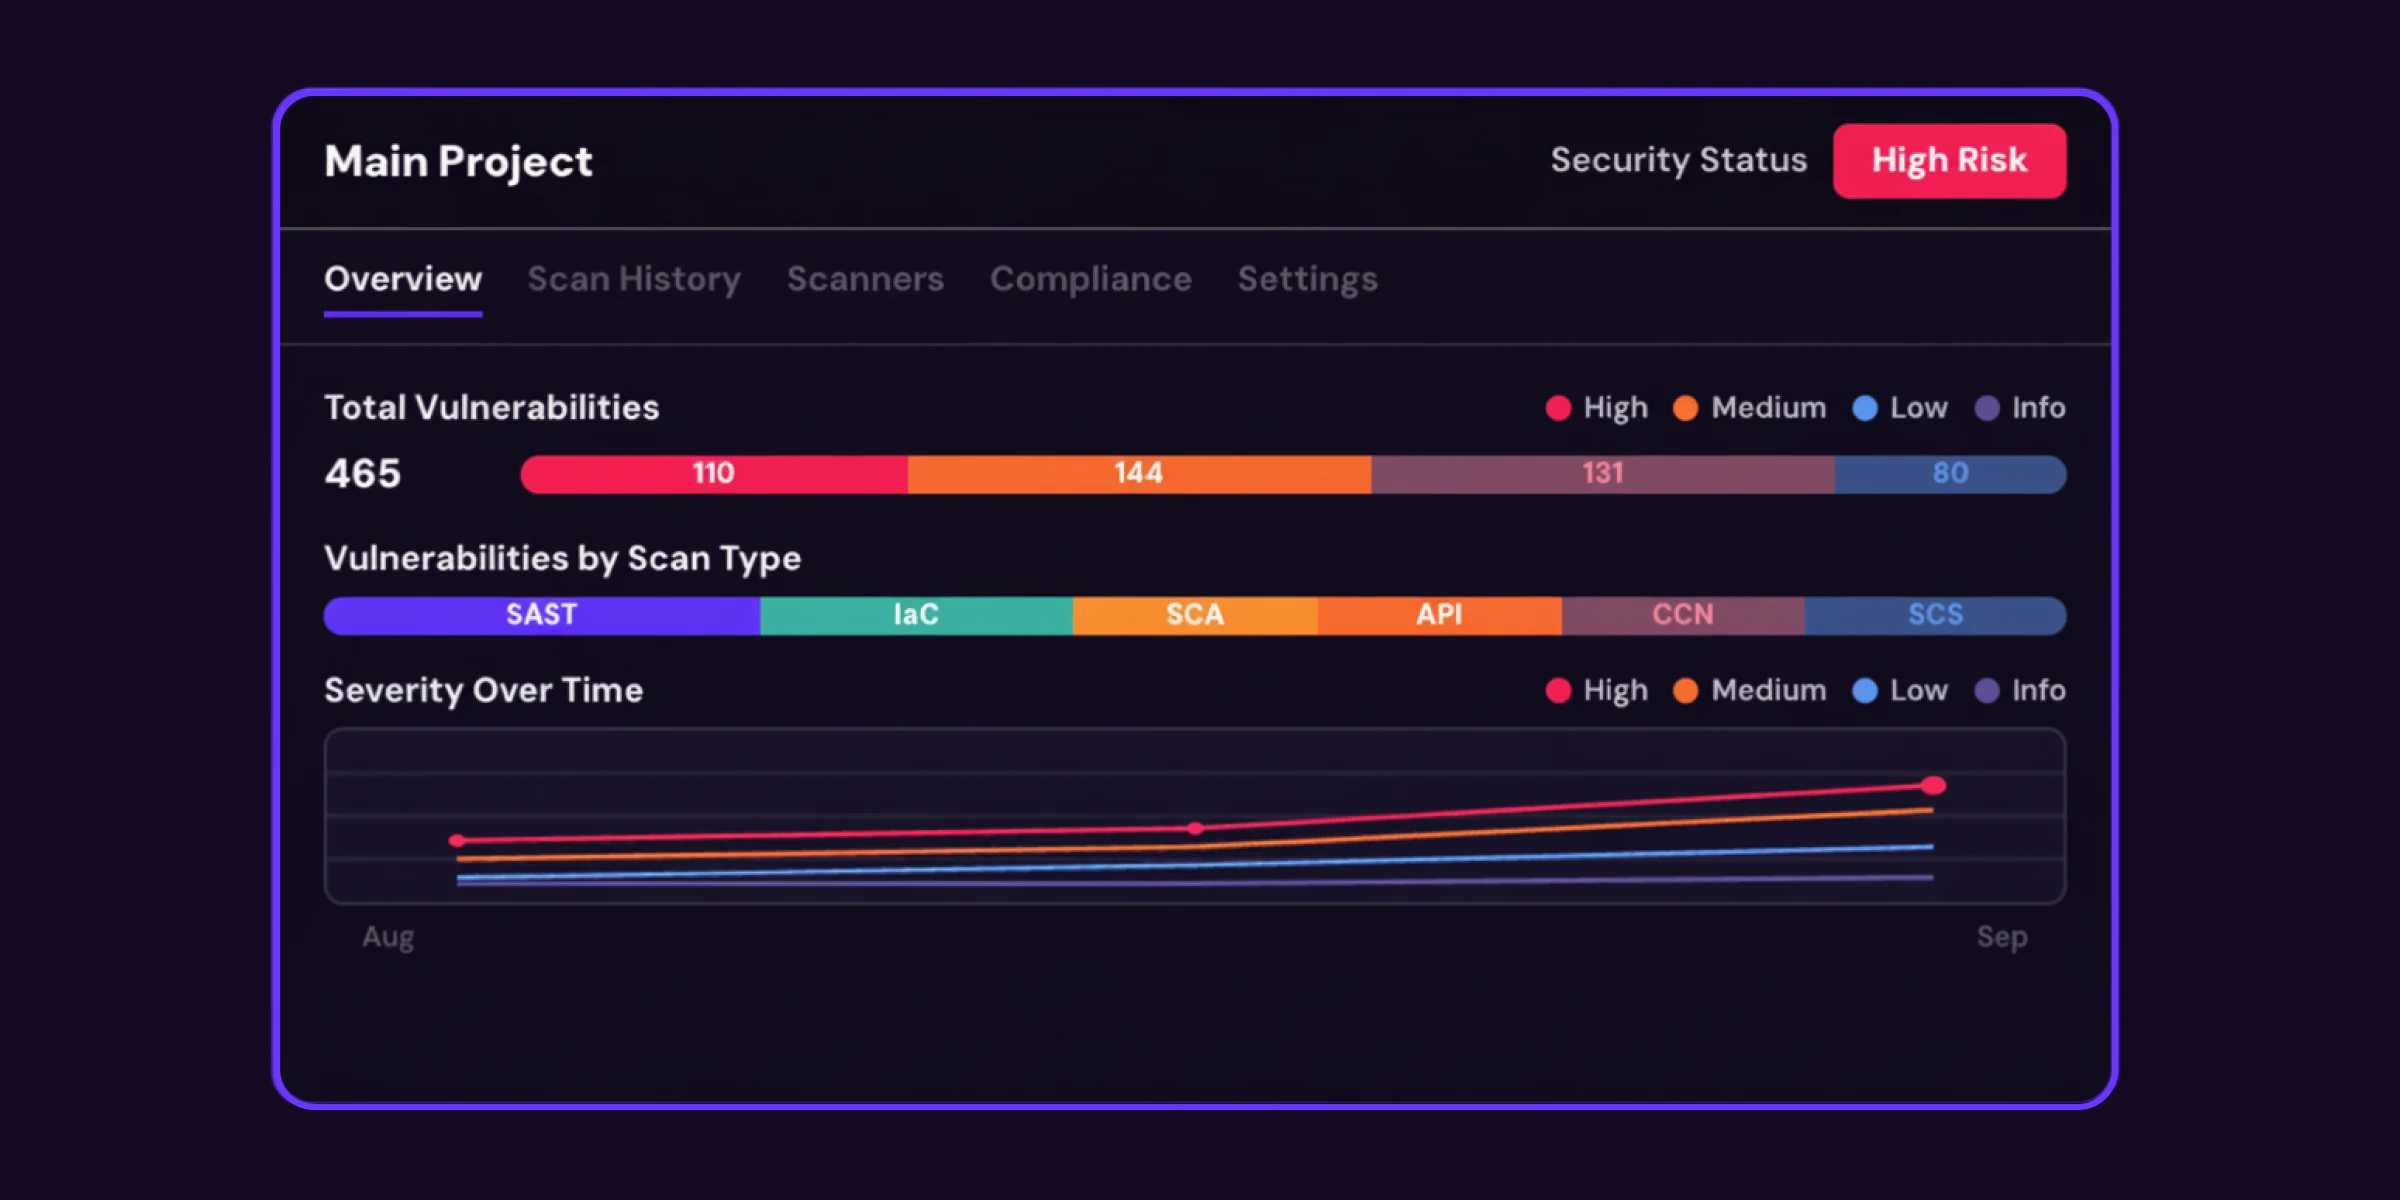
Comprehensive & Actionable Reporting
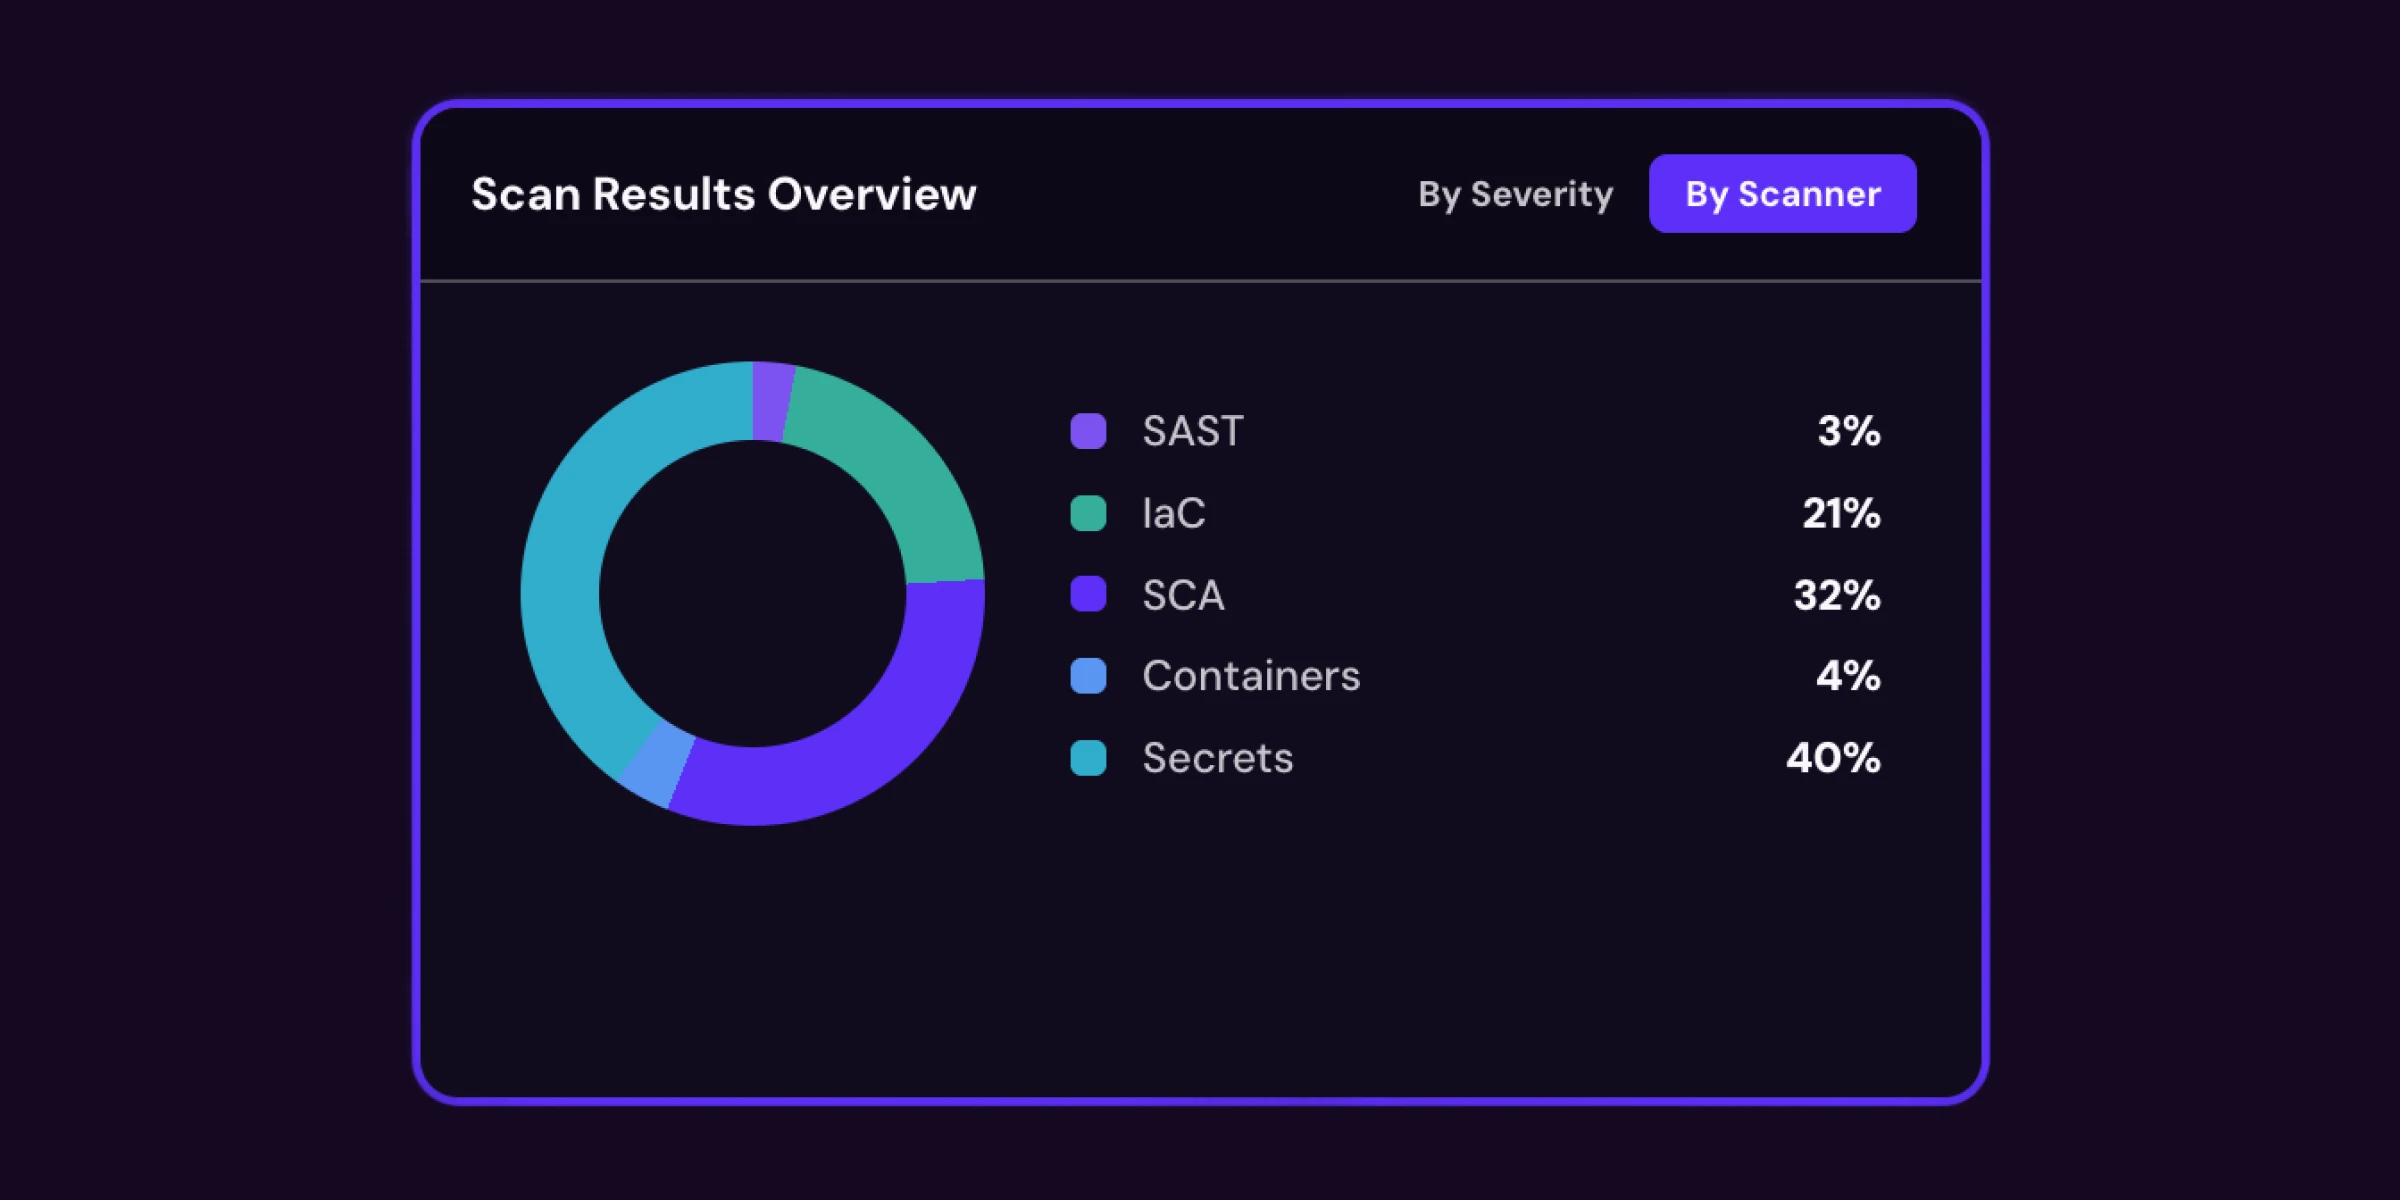
Detailed reporting includes insights on detected secrets to provide clear and actionable guidance to efficiently address risks.
We Find Secrets
Across Your Entire SDLC
Secrets don’t just live in your main branch. They hide in test files, config backups, CI scripts, container images, and years of Git history. Checkmarx scans everywhere attackers would look.


Secrets Exposed in Code Are
the #1 Cause of Cloud Breaches
Hardcoded credentials remain in Git histories for years after deletion. The average time to detect an exposed secret is 197 days – Checkmarx finds them in minutes.


Easily Detect and Remediate Exposed Secrets
Minimize security risks and strengthen your security posture by ensuring that no unsecured secret credentials are not making your organization vulnerable to attack.

Keep Your Secrets Secret
Prevent the unintended exposure of sensitive credentials, tokens, keys, certificates, or URLs that can endanger your organization.

Secure your Supply Chain
Make secrets leakage prevention a core component of your comprehensive software supply chain security (SSCS) strategy.

Improve Regulatory Compliance
Avoid fines and reputational damage by fully meeting regulations that require organizations to safeguard sensitive data (e.g., GDPR, HIPAA, PCI DSS, SOX, FISMA, CCPA).
Related Resources
 Solution Brief
Checkmarx Secrets Detection Solution Brief
Learn how to minimize the risk of cyberattacks by preventing exposure of hardcoded passwords, access tokens, certificates, encryption keys, API keys, and other sensitive credentials.
Learn More
 Blog
The Dangers of Exposed Secrets – and How to Prevent Them
Learn More
Blog
Secret Sprawl: The Silent Threat to Enterprise Security
Learn More
Why the World’s Top Teams Choose Checkmarx

“We’ve seen an 80% noise reduction — our engineers now focus on the high-quality risks that matter.”Explore Best Buy Case Study
“By far the best AppSec tooling decision we have made”
“Checkmarx gave us a 90% reduction in vulnerabilities in just a few months.”
“Unifying our AppSec tools with Checkmarx gave us a single source of truth.”
“With 2.1B lines of code scanned monthly, Checkmarx gives us the scale and speed we need.”
“Checkmarx fits seamlessly into our DevOps pipelines—it’s a truly scalable solution.”

“From a buyer perspective, Checkmarx’s approach offers a structured and role-aware entry point into agentic security. ”
“Incorporating Checkmarx’s technology has revolutionized our development culture.”
“Checkmarx One made our security team and developers life easier.”
“The success of our AppSec program can be directly attributed to the tooling, processes and support provided by the Checkmarx managed services.”

“Bringing ASPM context directly into the IDE reflects a forward-looking approach to prioritizing security efforts based on risk earlier in the development process.”
Frequently Asked Questions
Secrets detection is the practice of scanning source code, configuration files, Git history, and CI/CD pipelines for hardcoded credentials — API keys, passwords, tokens, certificates, and private keys. These exposed secrets can give attackers direct access to cloud infrastructure, databases, and third-party services, making them one of the highest-risk vulnerabilities in modern software development.
It is important to identify any private or sensitive information that could potentially be used in an attack or data breach. This includes credentials (such as usernames or passwords that can grant a user or system access to resources or services), API keys or tokens (unique identifiers to authorize access to an API or web service), private keys or encryption keys (such as those used to encrypt/decrypt sensitive data or secure communication protocols), certificates (codes used to establish trust between two entities, such as between a server and a client), and private endpoint/webhook URLs.
Secrets can be exposed in a wide variety of places, including source code, configuration files (e.g., IaC files), CI/CD pipelines, developer productivity tools, collaboration tools, wikis, and generative AI tools. To minimize potential vulnerabilities, any secrets exposed in any non-private location must be identified, removed, and changed.
An effective secrets detection solution algorithm must exhibit high precision and high recall. High precision means a low number of false alerts. In other words, high precision means that a high percentage of identified secrets are actual secrets that are at risk of exposure. High recall means that a low number of secrets are missed. Given that even one undetected credential can introduce a large amount of risk, it is often considered preferable to have to investigate some false alerts to ensure that no real exposed secrets are overlooked.
There are many techniques that can prevent the exposure of secrets; when developers and DevOps professionals are aware of the dangers and available solutions, the incidence of exposed secrets drops sharply. Secrets can be stored in environment variables or separate files instead of hardcoding them (these files should be included in .gitignore to ensure that they are not synced to a repository). Another option is to encrypt all secrets, using a dedicated secrets management tool, and implement two-factor authentication (2FA) for any repositories that still might contain secrets. In all cases, automated scanning technology should be used to detect hardcoded secrets in source code and prevent them from being pushed to code repositories from where their leakage is more likely.
When a developer commits a secret and later deletes it, the credential still exists in every previous commit in the repository’s history. Anyone with Git access — including contractors, open-source contributors, or attackers who gain access — can retrieve it. Scanning only the current codebase misses these historical secrets entirely. Checkmarx scans the complete Git history to find credentials that have been “deleted” but never actually rotated.
Checkmarx combines multiple techniques to minimize false positives: high-entropy analysis to distinguish random-looking real credentials from placeholder values, contextual analysis to recognize test files and example code, structural pattern matching against known credential formats (e.g., AWS key prefixes), and allowlisting for common test credential patterns. The result is a high-confidence finding set that developers can act on immediately without drowning in noise.
Checkmarx detects 100+ secret types out of the box, including: AWS, Azure, and GCP credentials; GitHub, GitLab, and Bitbucket tokens; payment provider keys (Stripe, PayPal, Square); communication platform tokens (Slack, Twilio, SendGrid); RSA/DSA/EC private keys; JWT secrets; database connection strings with passwords; and many more. Custom patterns for internal secrets and proprietary systems are also configurable.
Checkmarx integrates at multiple points in the development lifecycle: IDE plugins for VS Code and IntelliJ provide real-time alerts as developers write code; pre-commit hooks prevent secrets from entering Git at all; CI/CD integrations with GitHub Actions, Jenkins, Azure DevOps, and TeamCity scan on every push and pull request; and the Checkmarx One platform provides a unified dashboard for security teams to monitor and manage findings across all repositories.
Any time an exposed secret is discovered, it is advisable to immediately revoke/replace the secret to remove the risk of the secret being used in an attack or breach. This is especially important if the secret was exposed in a public platform (such as GitHub), because once posted it might never be possible to completely remove it. And, of course, do not repeat the mistake and include the new secret in an exposed manner.
Checkmarx provides step-by-step remediation guidance for every finding. The general approach is: (1) immediately rotate the credential in the issuing service — do not just delete it from code; (2) update all environments using the old credential; (3) replace the hardcoded value with an environment variable or secrets manager reference; (4) audit access logs to check for unauthorized use during the exposure window. Checkmarx provides direct links to the rotation interface for each supported provider.
Yes. Secrets Detection is a native capability within Checkmarx One, the unified cloud-native AppSec platform. It integrates with SAST, SCA, DAST, and ASPM findings in a single dashboard — providing correlated risk prioritization so security teams can see which repositories have both code vulnerabilities and exposed credentials, and understand the combined blast radius.
You Can’t Secure What You Can’t See
Talk to an AppSec expert about Checkmarx Secrets Detection. We’ll respond within 1 business day.
Thank You!
Your Custom Checkmarx Demo Request was Successfully Sent!
Get a Demo
See Secrets Detection in Action
Scan Your Actual Repos
Connect your repositories in minutes and see real findings — not synthetic demos — during your evaluation.
Surface Historical Secrets
See credentials buried in your Git history that no other tool or control has ever flagged.
IDE Integration Live
Watch real-time secret detection in VS Code and IntelliJ — stopping credentials before they’re committed.
Step-by-Step Remediation:
See how Checkmarx guides developers to rotate credentials correctly in under 5 minutes per finding.
Stop Exposed Secrets Before
They Cause a Breach
Every day your repositories go unscanned, credentials from years of commits remain available to attackers. Start finding them in minutes with Checkmarx Secrets Detection.