
AI Supply Chain Security
for Complete AI Risk Control
Secure the AI you build on before it becomes an attack surface. Get complete visibility and governance
over every AI component in the ADLC, before threats reach production.
From Shadow AI to Secure AI
Shadow AI ends here. Checkmarx gives AppSec full visibility and governance across the ADLC, exposing AI assets such as LLMs, MCPs, Agents, AI SDKs and Libraries, to block risk before code ships.
You can’t secure what you don’t see. Lack of visibility and siloed data hide AI assets across repos and pipelines.

Complete AI oversight
Reduce risk exposure. Automatically discover every LLM, agent framework, MCP server, dataset, and prompt across your application.
Even after you gain visibility, you still don’t know the security vulnerabilities introduced by your AI assets.

Know your risks
Understand the risks your AI introduces. Identify risks that others miss, including insecure deserialization, dangerous model loaders, shell execution, and suspicious patterns.
AI visibility and transparency gaps put trust and compliance posture at risk.

Enforce AI Governance Without Friction
Govern AI in the development workflow. Flag AI risks in PRs and pipelines, whitelist trusted components, block threats, generate AI-BOMs, and enforce policy directly in‑flow. Govern AI in the development workflow
Flag AI risks in PRs and pipelines, whitelist trusted components, block threats, generate AI-BOMs, and enforce policy directly in‑flow.
Turn AI Blind Spots into Actionable Insights
See how you can find and protect hidden AI, ensure compliance, and reduce AI supply chain risk.
Why choose Checkmarx AI Supply Chain Security
Complete visibility, assessment, control, and reporting over AI usage across your enterprise, from discovery to compliance.
Deterministic, Code-Based Detection
Discovery relies on real signals – analyzing source code, dependency files, configuration manifests, and import statements – not AI inference.

Deployed LLMs Visibility
Gain cross-portfolio visibility at scale with a centralized AI asset catalog that spans all repositories and applications.

Generate AI BoMs
Go beyond CVE scanning to detect AI supply chain threats such as model poisoning indicators, unverified model sources, dataset exposure risks, and configuration weaknesses.
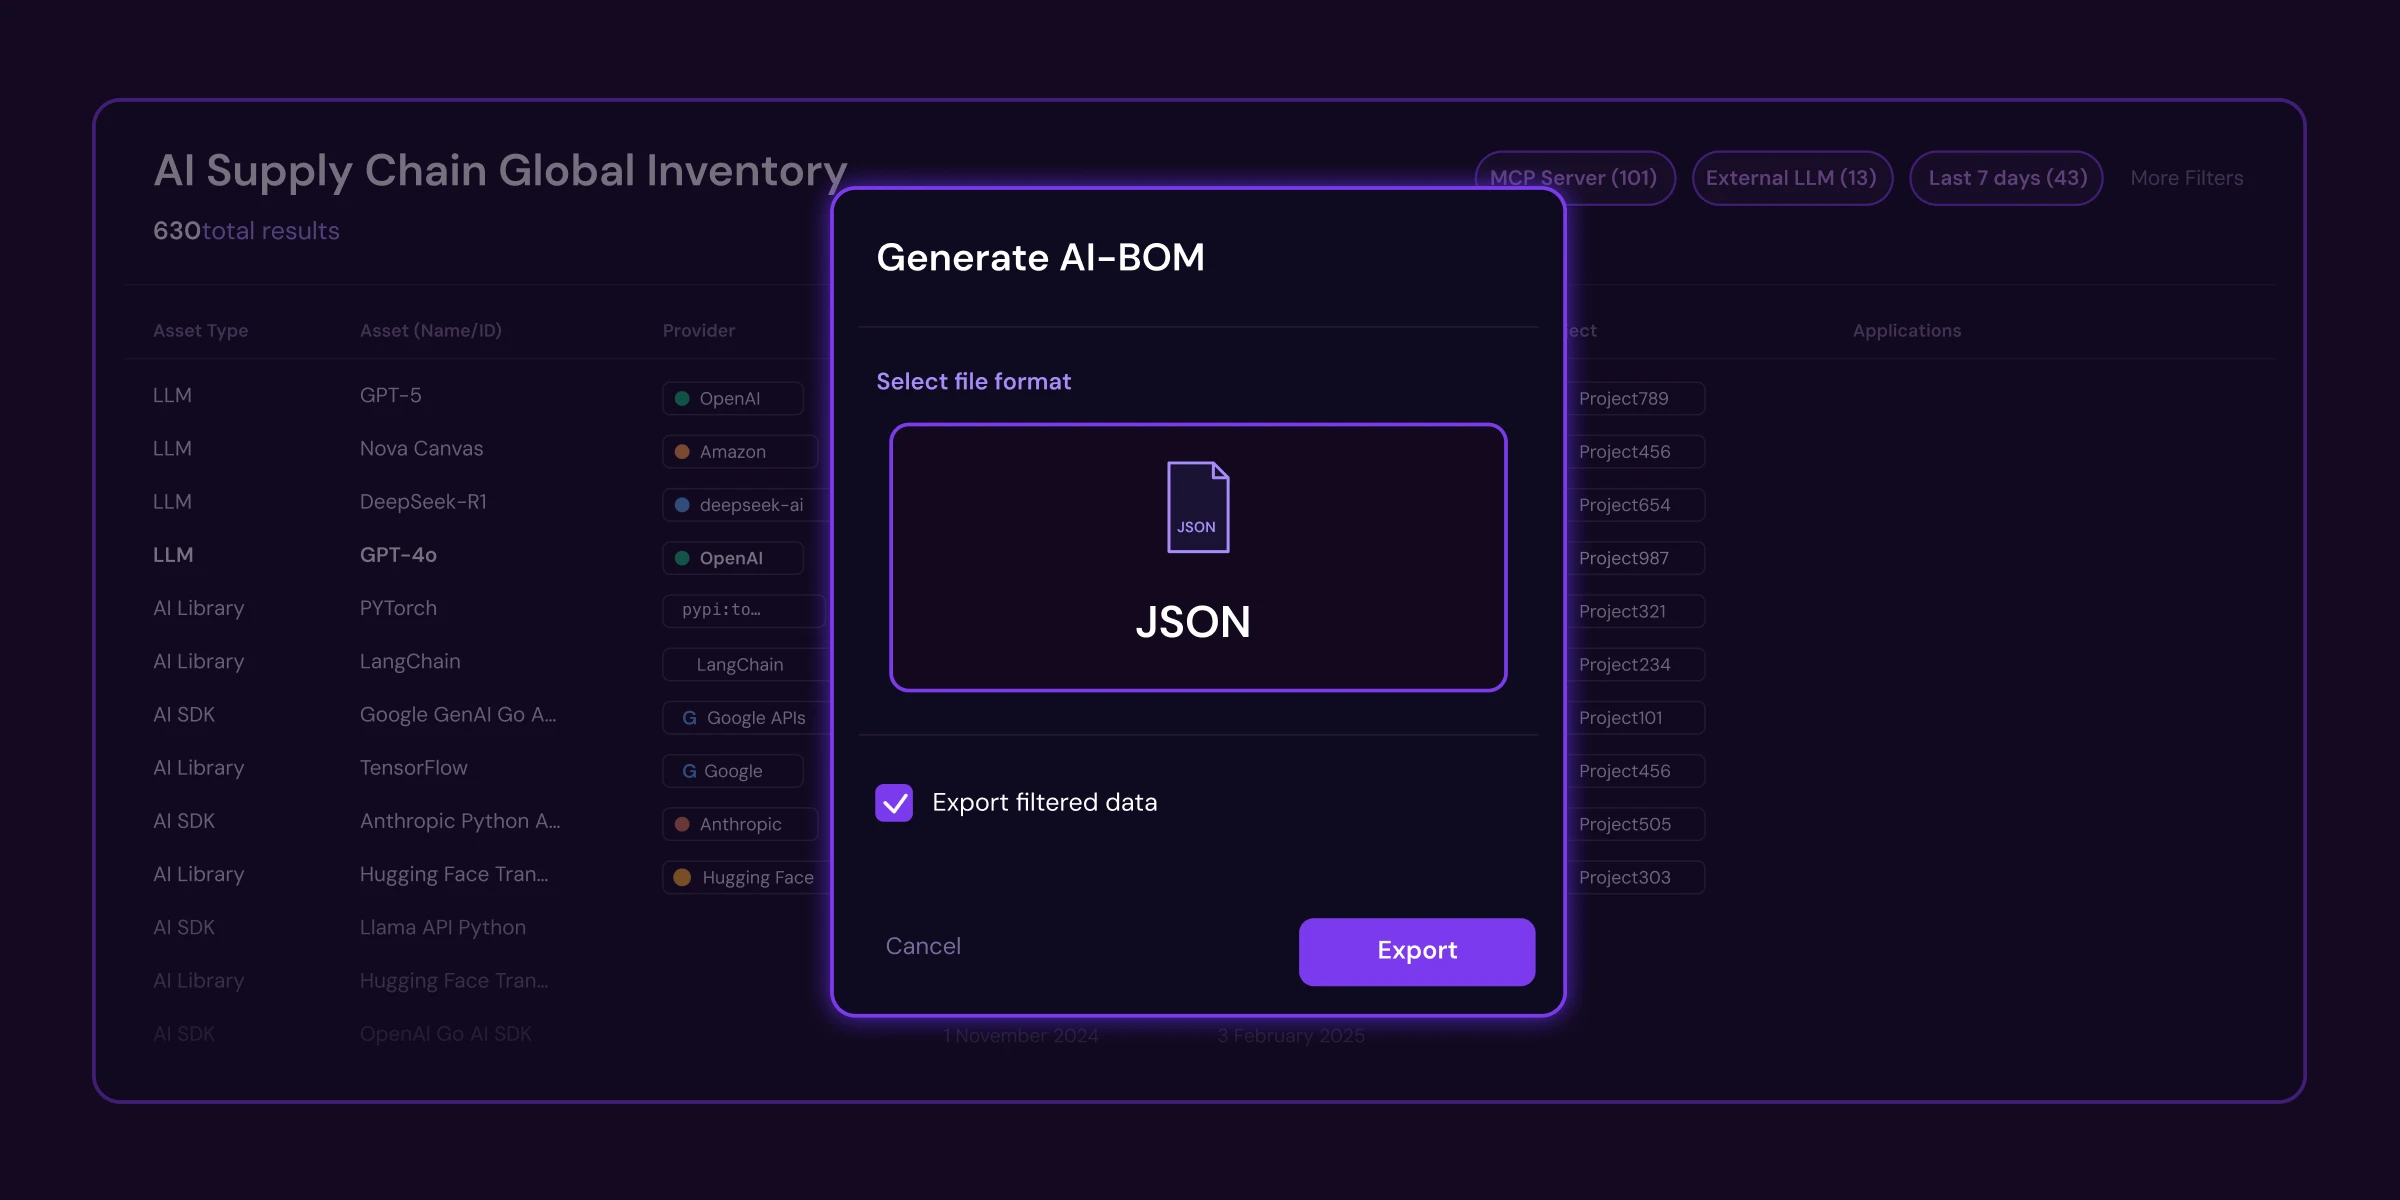
AI Governance and Compliance
Map discovered AI assets to compliance frameworks (NIST AI RMF, EU AI Act, ISO 42001, OWASP LLM Top 10) with audit trails and risk documentation aligned to regulatory requirements.

Unified AppSec Posture Control
AI security lives within your unified AppSec platform, not a separate tool. No new platform to adopt, no siloed data, no fragmented visibility.

Building CRA-Aligned Security with Checkmarx
Sign-up for a Custom Demo and see how Checkmarx helps Your company become Cyber Resilience compliant.
Get practical implementation walkthrough of lifecycle‑long risk assessment, SBOM/AI‑BOM visibility, and securing your software supply chain.


Related Resources
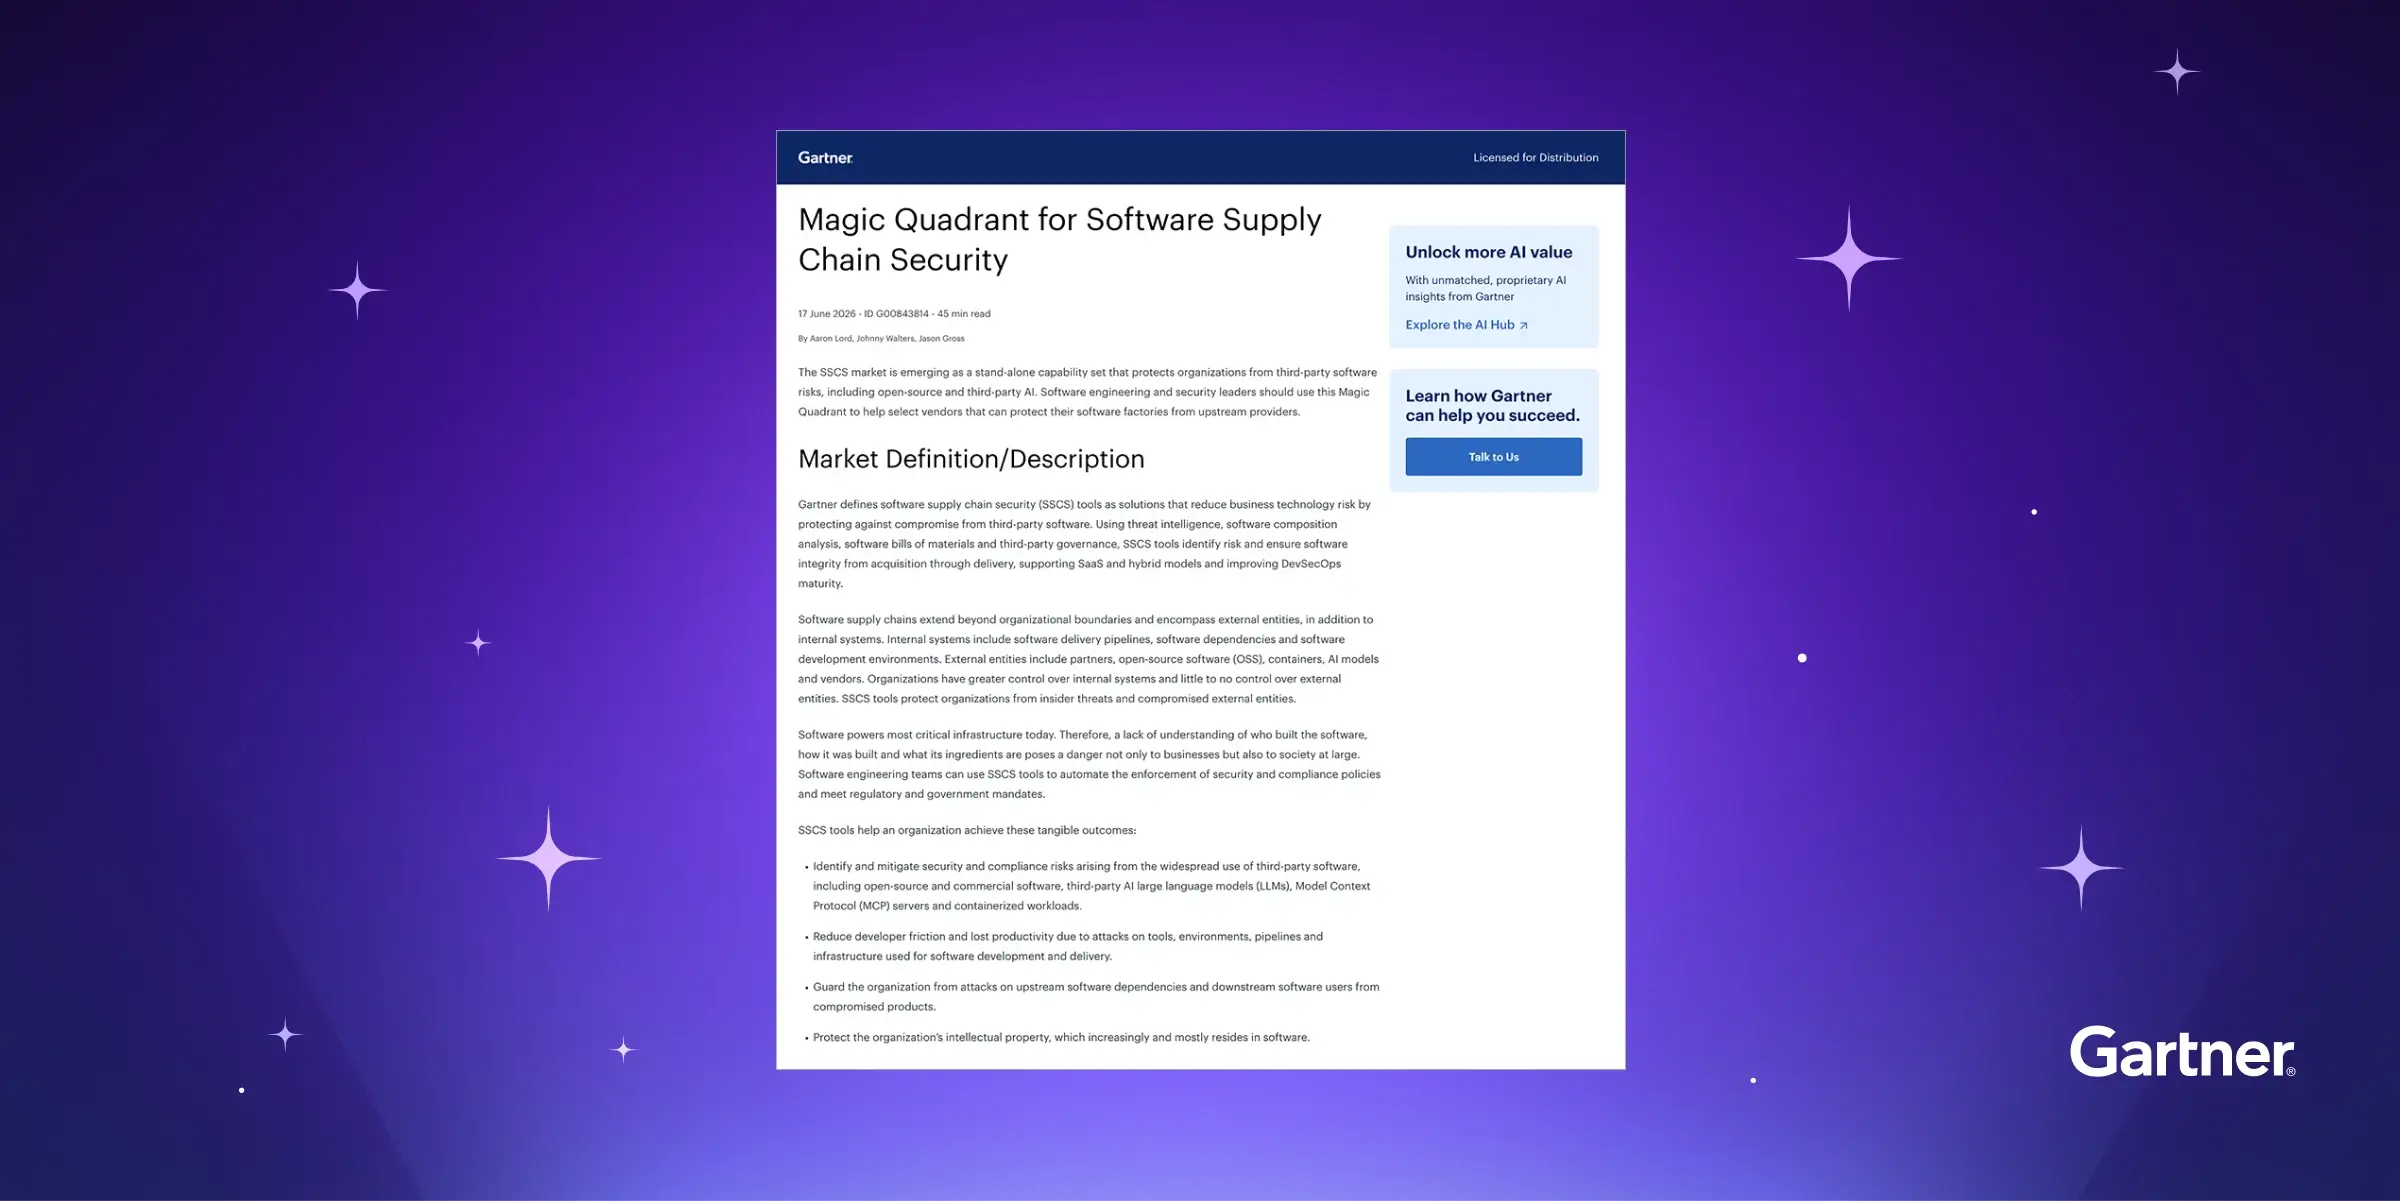 Analyst Report
Gartner® Magic Quadrant™ for Software Supply Chain Security 2026
Explore the Gartner® Magic Quadrant™ for Software Supply Chain Security to learn why Checkmarx was named A Leader for its unified AppSec and supply chain security platform
Learn More
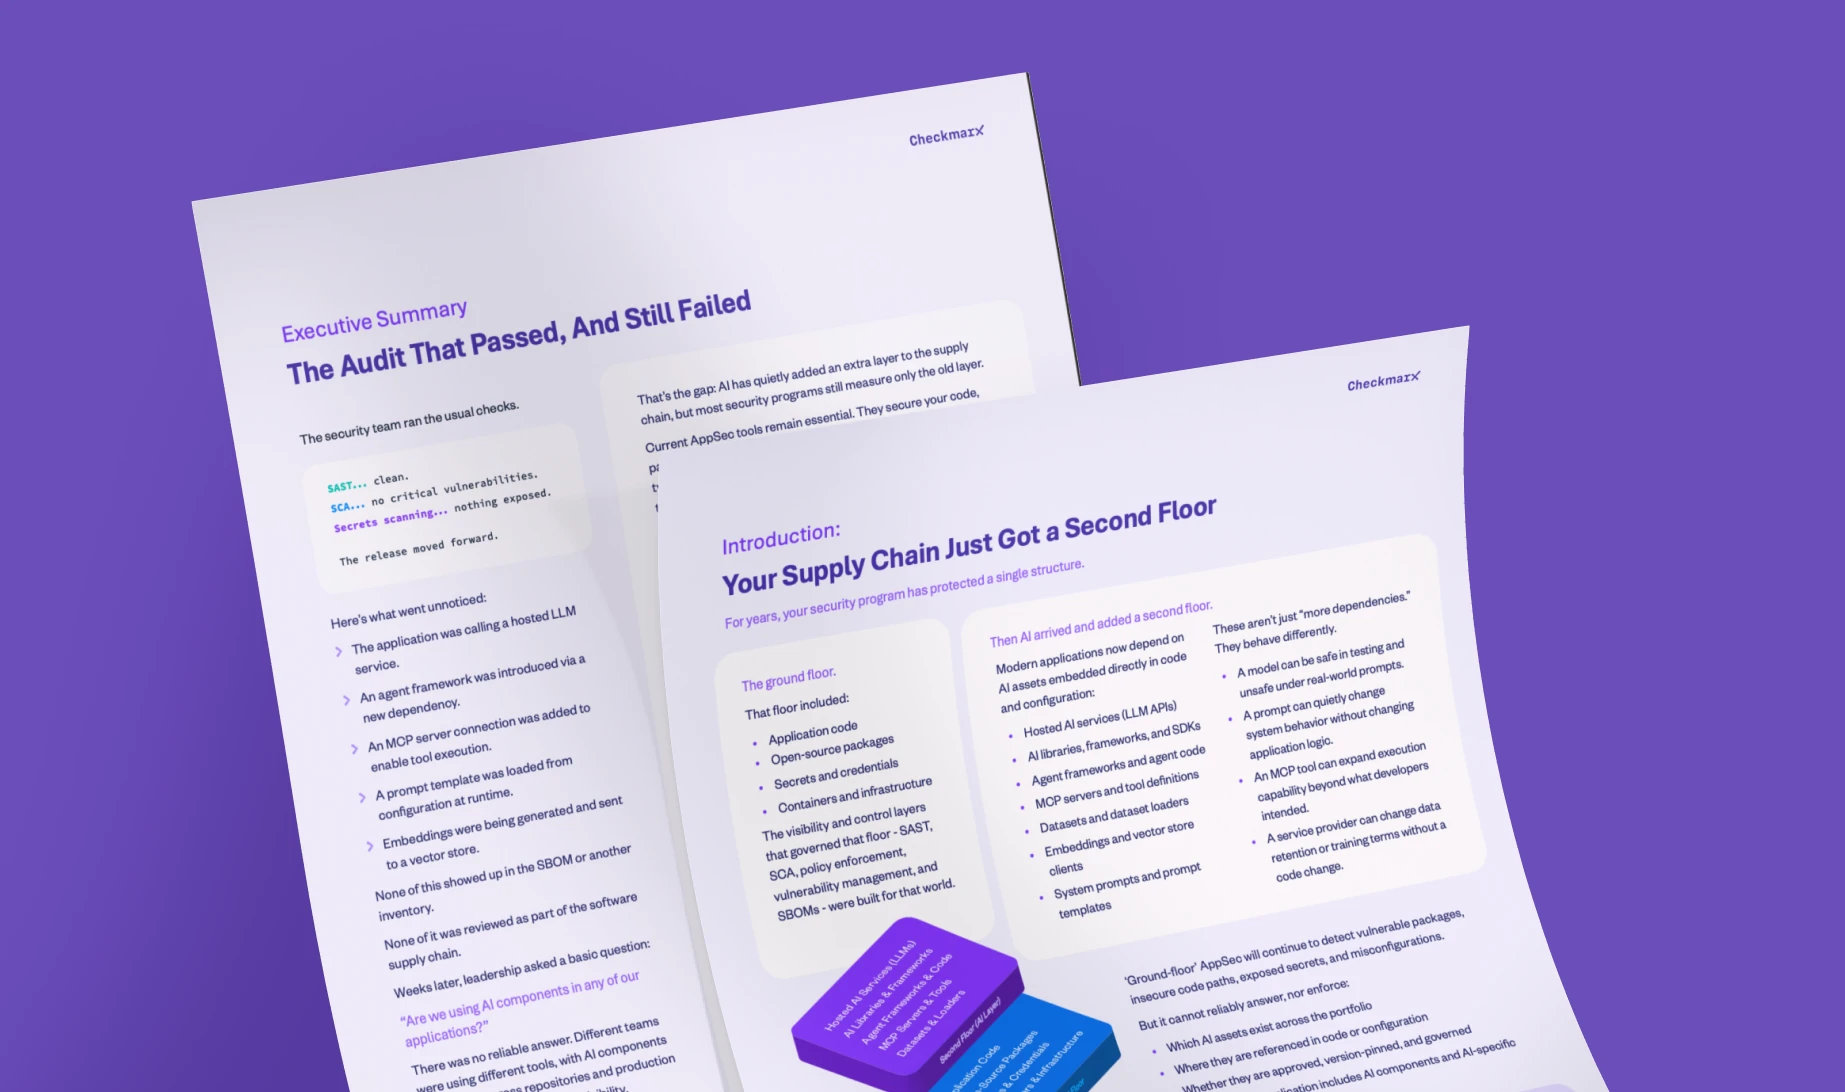 eBook
10 Al Supply Chain Risks Hiding in Your Codebase, and How to Get Ahead of Them
Learn More
 Solution Brief
AI SCS: See Every AI Component in Your Codebase
Learn More
 Webinar
The Software Supply Chain Just Got Harder to See
Learn More
 Whitepaper
Capability Without Security: Measuring the Functionality-Security Gap in AI-Generated Code
Learn More
Why the World’s Top Teams Choose Checkmarx

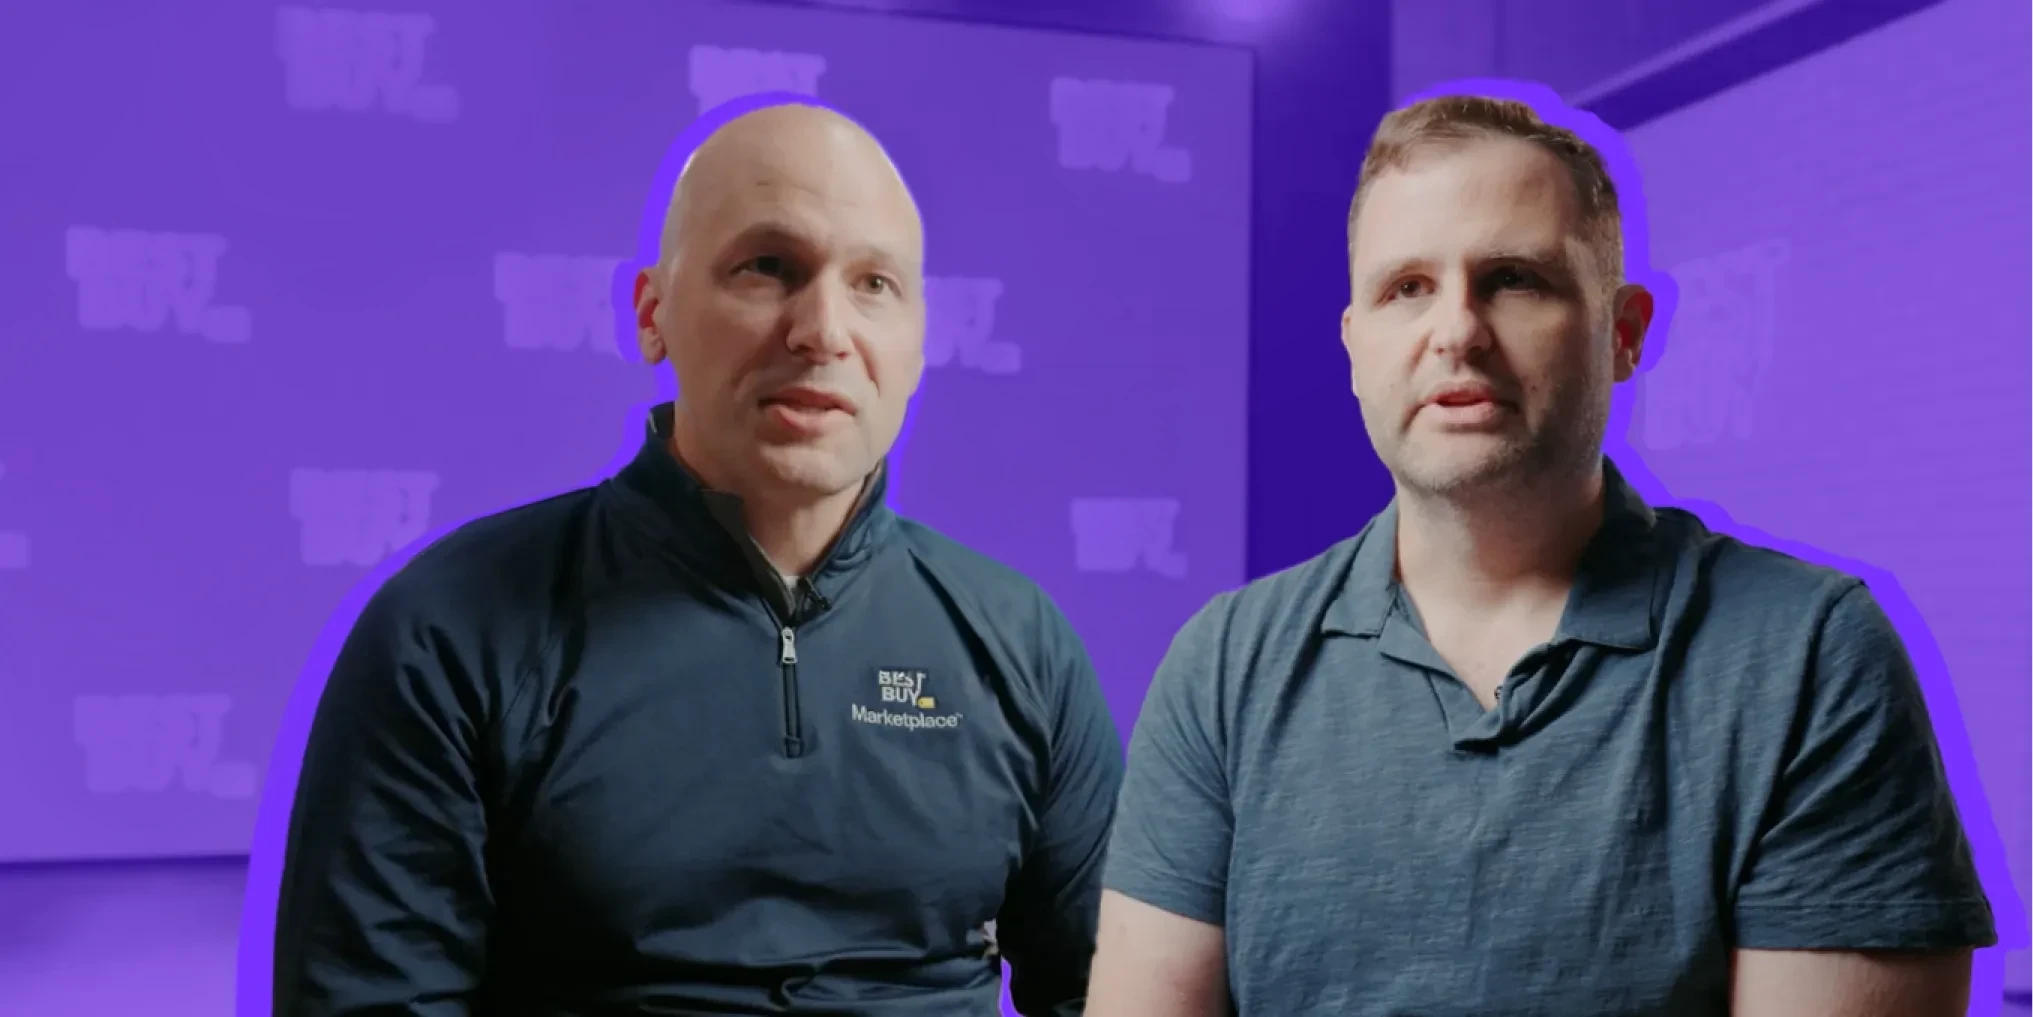
“We’ve seen an 80% noise reduction — our engineers now focus on the high-quality risks that matter.”Explore Best Buy Case Study
“By far the best AppSec tooling decision we have made”
“Checkmarx gave us a 90% reduction in vulnerabilities in just a few months.”
“Unifying our AppSec tools with Checkmarx gave us a single source of truth.”
“With 2.1B lines of code scanned monthly, Checkmarx gives us the scale and speed we need.”
“Checkmarx fits seamlessly into our DevOps pipelines—it’s a truly scalable solution.”

“From a buyer perspective, Checkmarx’s approach offers a structured and role-aware entry point into agentic security. ”
“Incorporating Checkmarx’s technology has revolutionized our development culture ”
“Checkmarx One made our security team and developers life easier.”
“The success of our AppSec program can be directly attributed to the tooling, processes and support provided by the Checkmarx managed services.”

“Bringing ASPM context directly into the IDE reflects a forward-looking approach to prioritizing security efforts based on risk earlier in the development process.”
Frequently Asked Questions
Checkmarx One AI Supply Chain Security discovers LLMs, AI SDKs, AI Libraries, MCP Servers. MCP Clients, AI Agents within your application.
You can explore all Checkmarx’s documentation here
No, our discovery engine is deterministic and relies on real signals, analyzing source code, dependency files, configuration manifests, and import statements, not AI inference.
Every organization has unique needs and sizes. For a price quote, please get in touch. See our packaging here.
If you are a current Checkmarx customer, please reach out to your account manager or contact us here
Checkmarx provides dedicated security assessment scanners for LLMs and MCPs. For LLMs, we detect security risks like insecure deserialization, dangerous model loaders, shell execution, and suspicious pickle/torch gadget patterns.
AI supply chain security is the practice of identifying and mitigating risks introduced by AI components including open-source LLMs, ML frameworks, pre-trained models, and AI-generated code, across the software development lifecycle. Unlike traditional supply chain risks, AI components can introduce hidden vulnerabilities through poisoned training data, compromised model weights, or insecure integrations that are difficult to detect with conventional security tooling.
s AI Software Supply Chain Security identifies AI components across your applications -models, LLMs, MCP servers – providing visibility for compliance frameworks. It helps determine which AI systems fall under EU AI Act risk classifications, NIST AI RMF governance, and ISO 42001 standards .
AI agents introduce security risks including excessive privilege, insecure tool invocation, indirect prompt injection via external data sources, and unintended data exfiltration. These risks are amplified in multi-agent or autonomous workflow environments, where a single compromised agent can propagate malicious instructions across an entire pipeline with little human oversight.
Start by taking an inventory of all AI usage to uncover Shadow AI. Assess your maturity with Checkmarx APMA. Align to frameworks like NIST AI RMF or ISO 42001. Define roles: AI risk owners, validators, compliance reviewers. Use AI SCS for continuous discovery and policy enforcement.
Securing open-source AI models and ML frameworks requires continuous inventory of all AI components in use, integrity verification of model weights and dependencies, and runtime monitoring for anomalous behavior. Organizations should treat every open-source model as an untrusted third-party dependency, scanning for known vulnerabilities, verifying provenance, and enforcing least-privilege access before deployment.
Get Your Personal Demo
See AI Supply Chain in Action
See how Checkmarx can enhance your AI security at the speed of development
Thank You!
Your Custom Demo Request is successfully sent.
A member of Checkmarx Team would contact you shortly to set up your custom demo.
Take Control of your AI Supply Chain
Unified AI Risk Management
Gain full visibility into AI assets with centralized monitoring and control
Native Integration into Checkmarx One
AI security lives within your unified AppSec platform
Meet AI Regulatory Requirements
Automate compliance with audit-ready oversight and reporting
Developer‑friendly Workflows
Integrate seamlessly with existing tools, so security doesn’t slow delivery.
Deterministic, Code‑Based Detection
Consistent, auditable results by analyzing real code and configs, no AI inference, no guesswork.
Enterprise‑ready
Trusted by 1,800+ customers including 40% of the Fortune 100
Get Started With
Checkmarx AI Software Supply Chain Security Today
Join the leading enterprises that include Checkmarx AI SSSCS in their application security toolkit for holistic application security.