Software Composition
Analysis (SCA)
Identify, prioritize, and remediate open-source risk in your applications, including vulnerabilities, malicious code, and license risks.
Everything You Need to Mitigate Open-Source Risk
Ship open source faster, not riskier. Know which open-source risks in your applications can be exploited, and fix those first, without slowing your developers down.
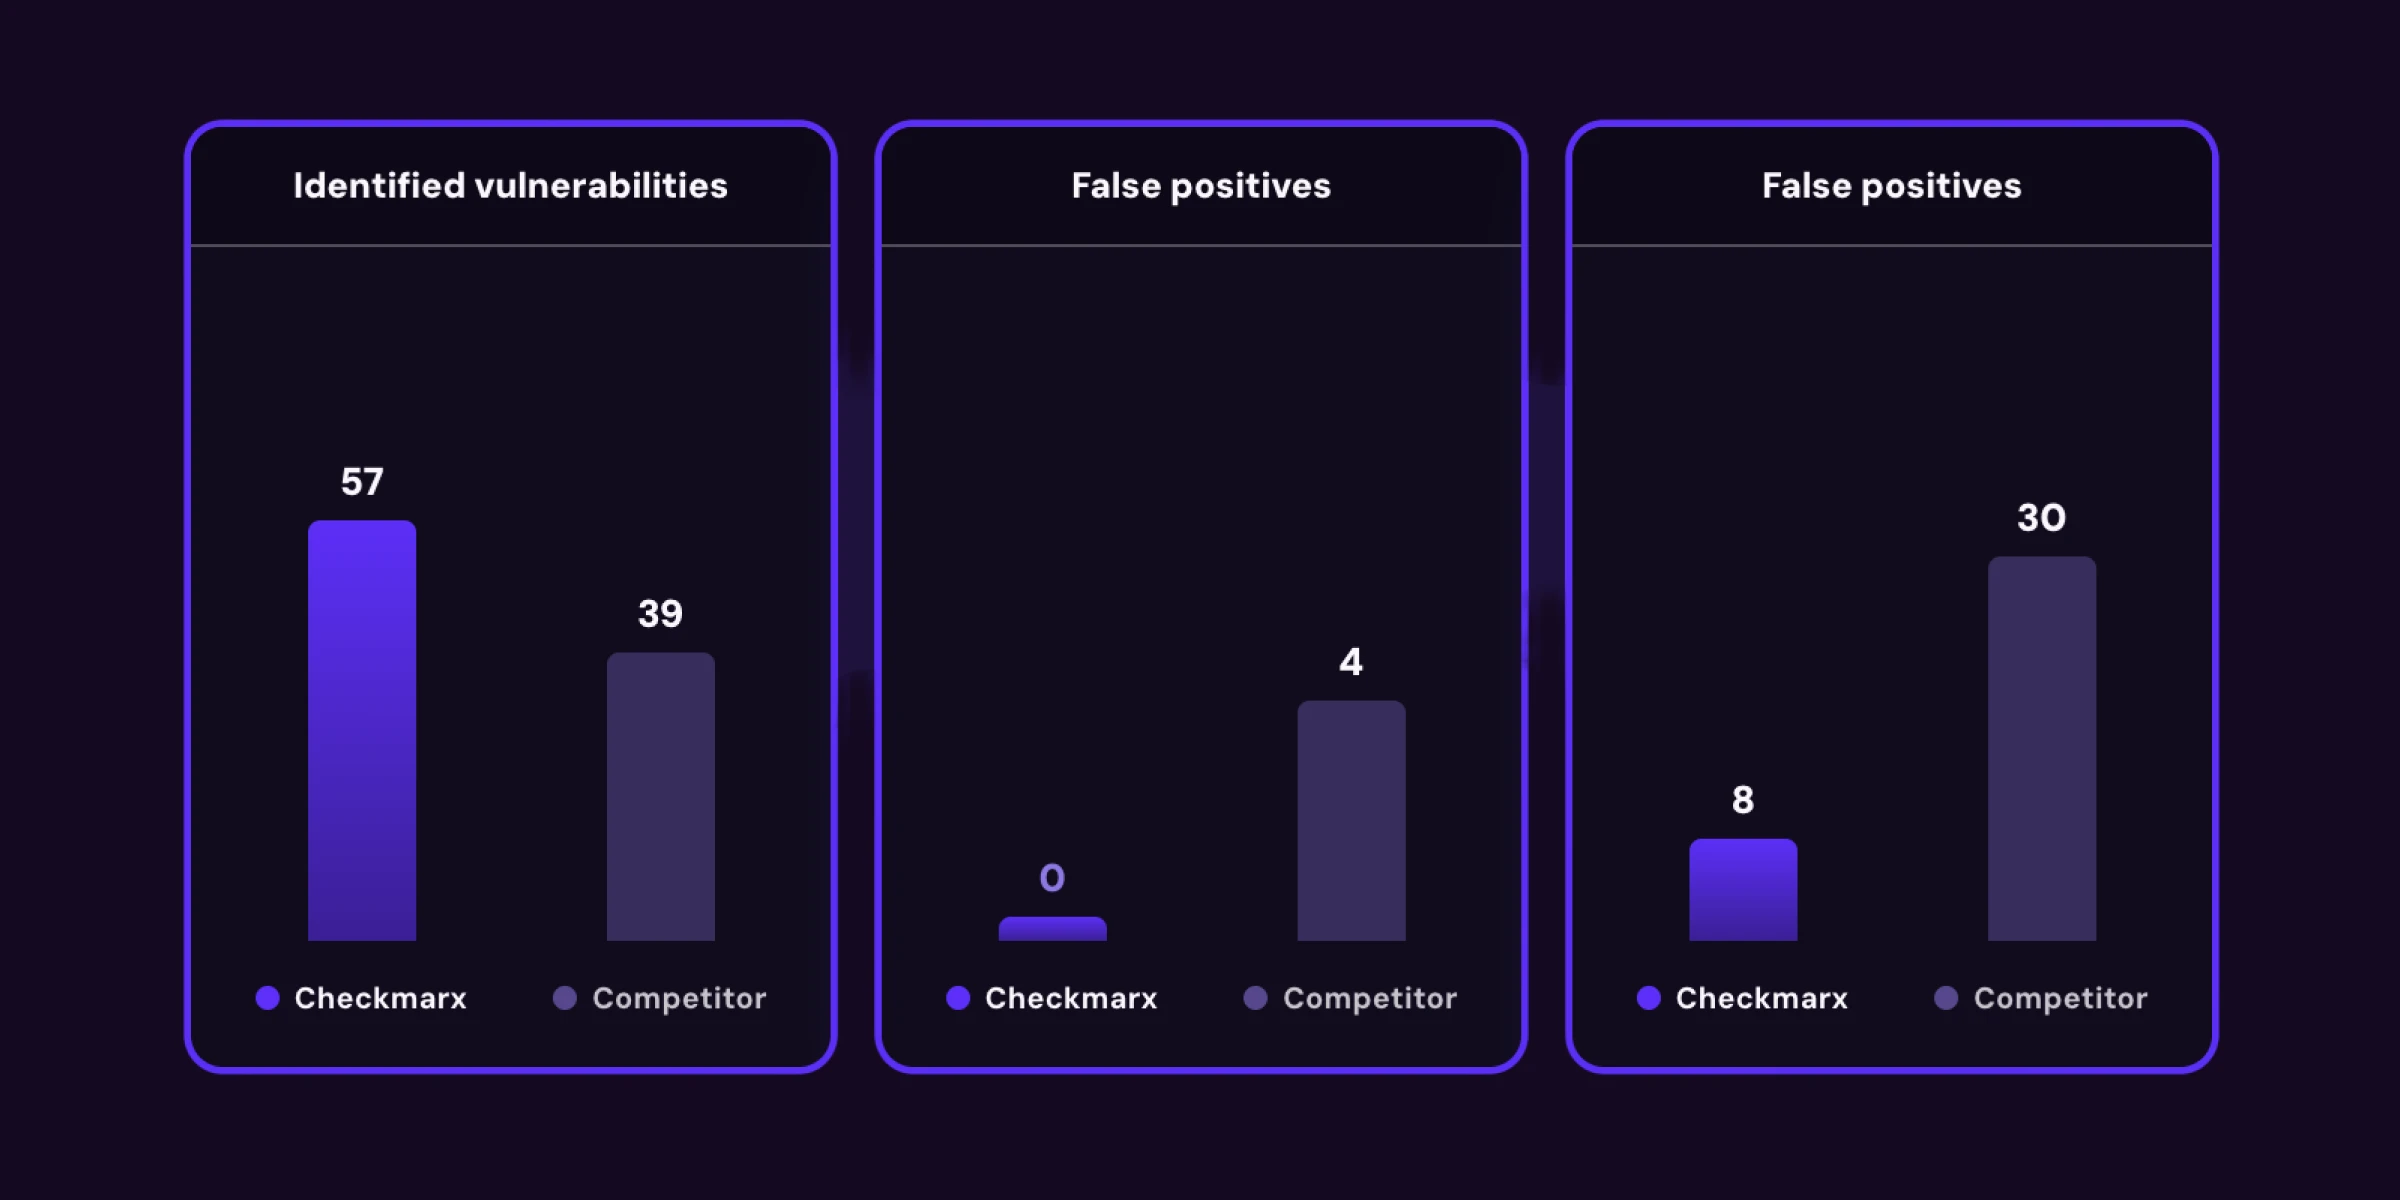
Unmatched Scan Accuracy
Checkmarx SCA tool verifies every match against known vulnerability data before it becomes a finding, with a zero false positive rate in independent testing, against 10% for the next-best competitor.
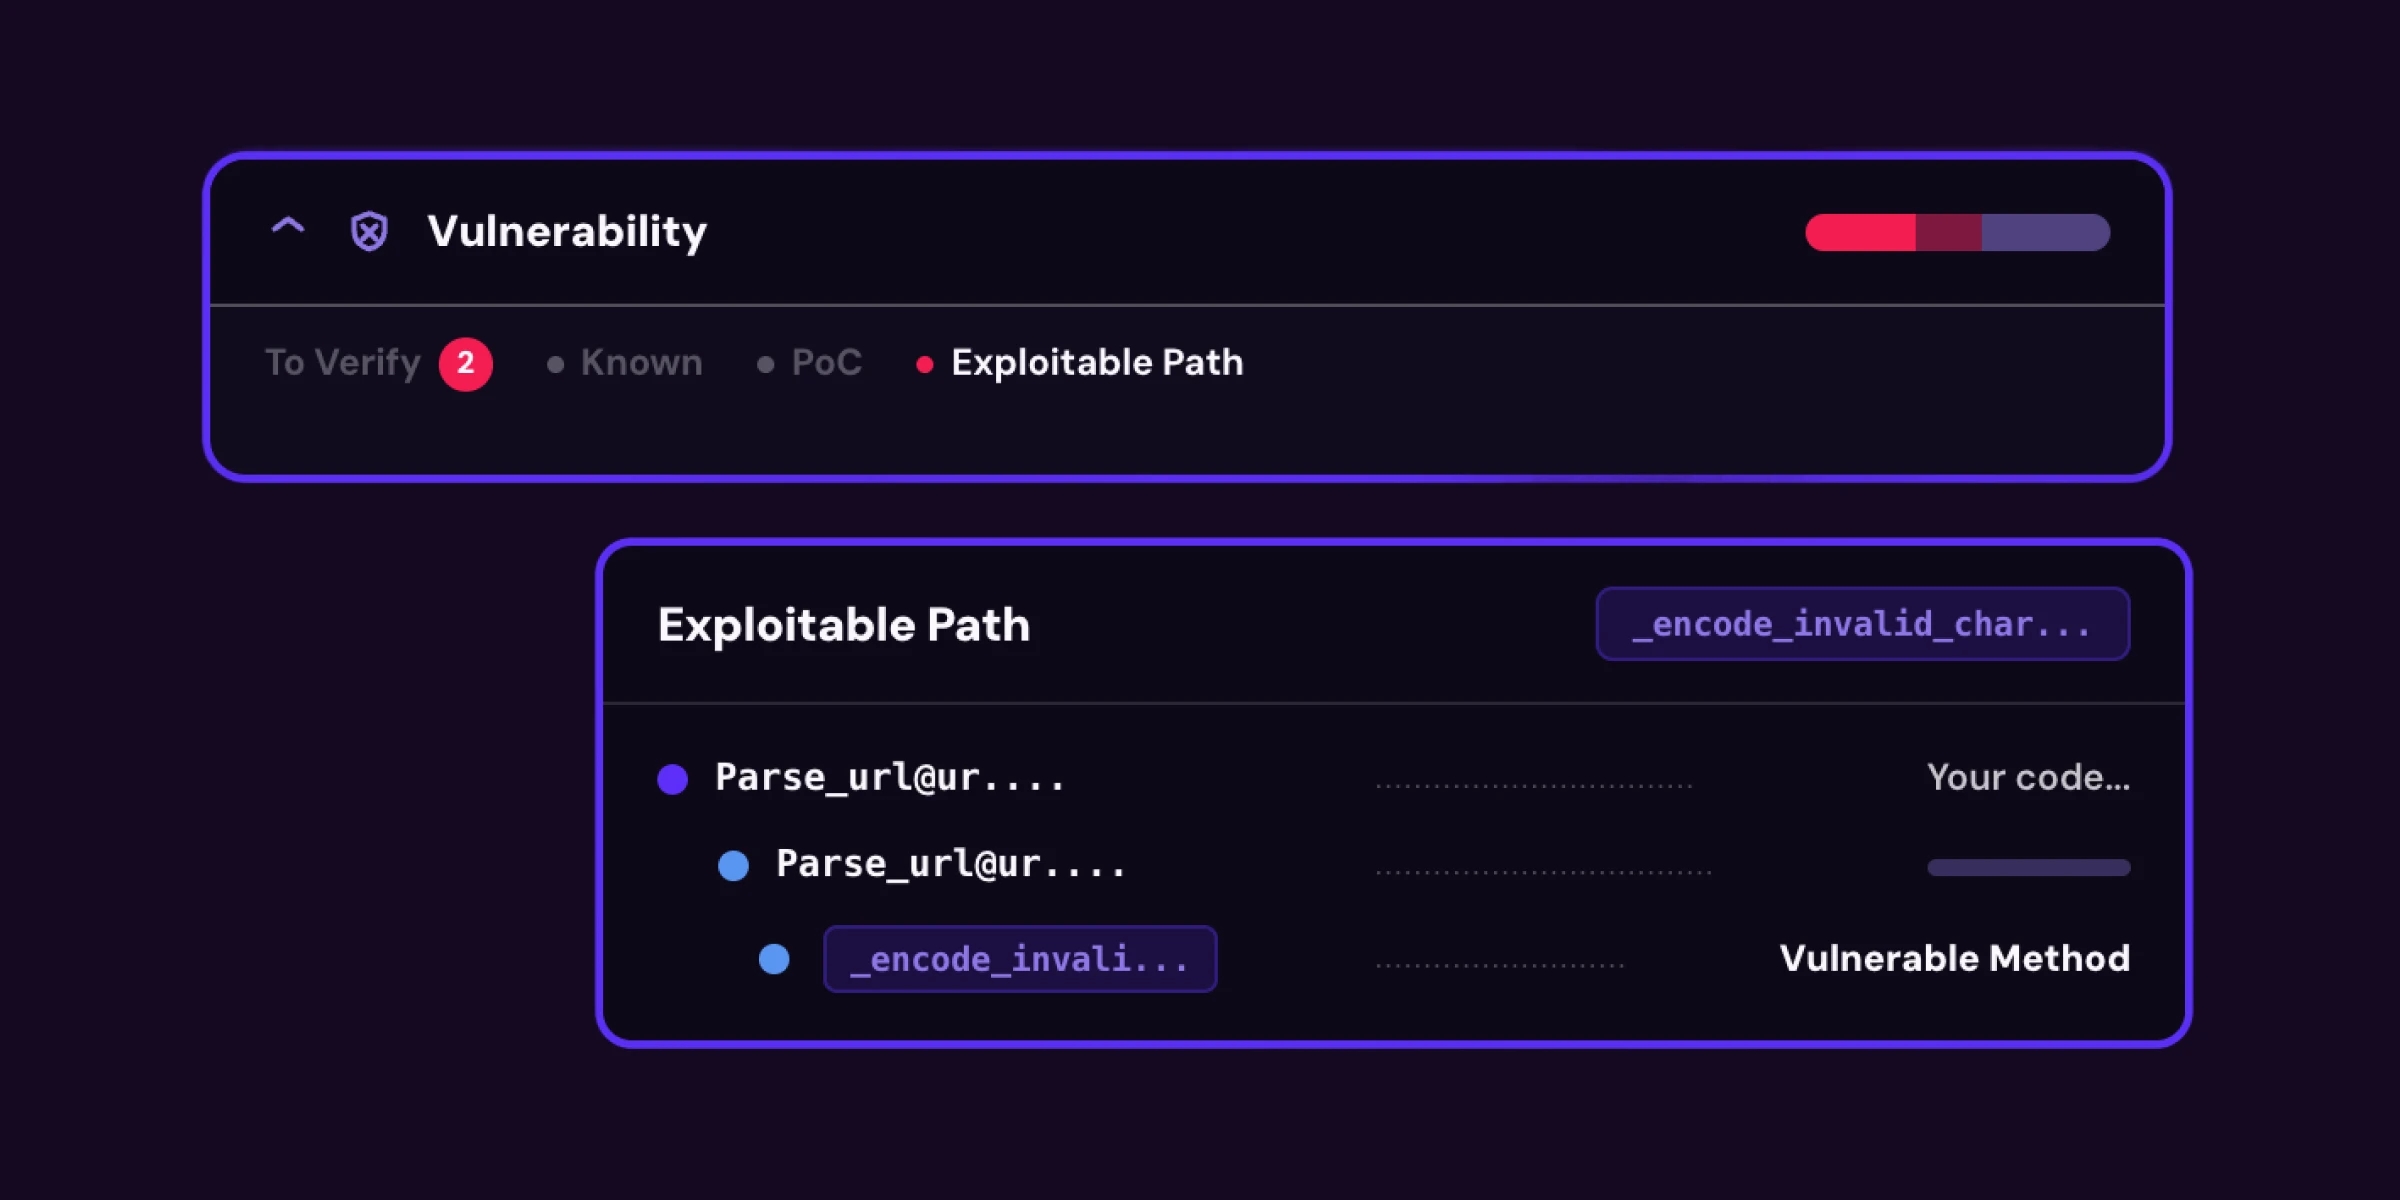
Trace the exact path to each vulnerability
Not every CVE is real risk. Reduce noise and prioritize remediation efforts by focusing on vulnerable OSS code that may potentially execute, based on an analysis of all potential call paths to unsafe functions. Supports a variety of coding languages, including Python, Java, JavaScript, and C#.
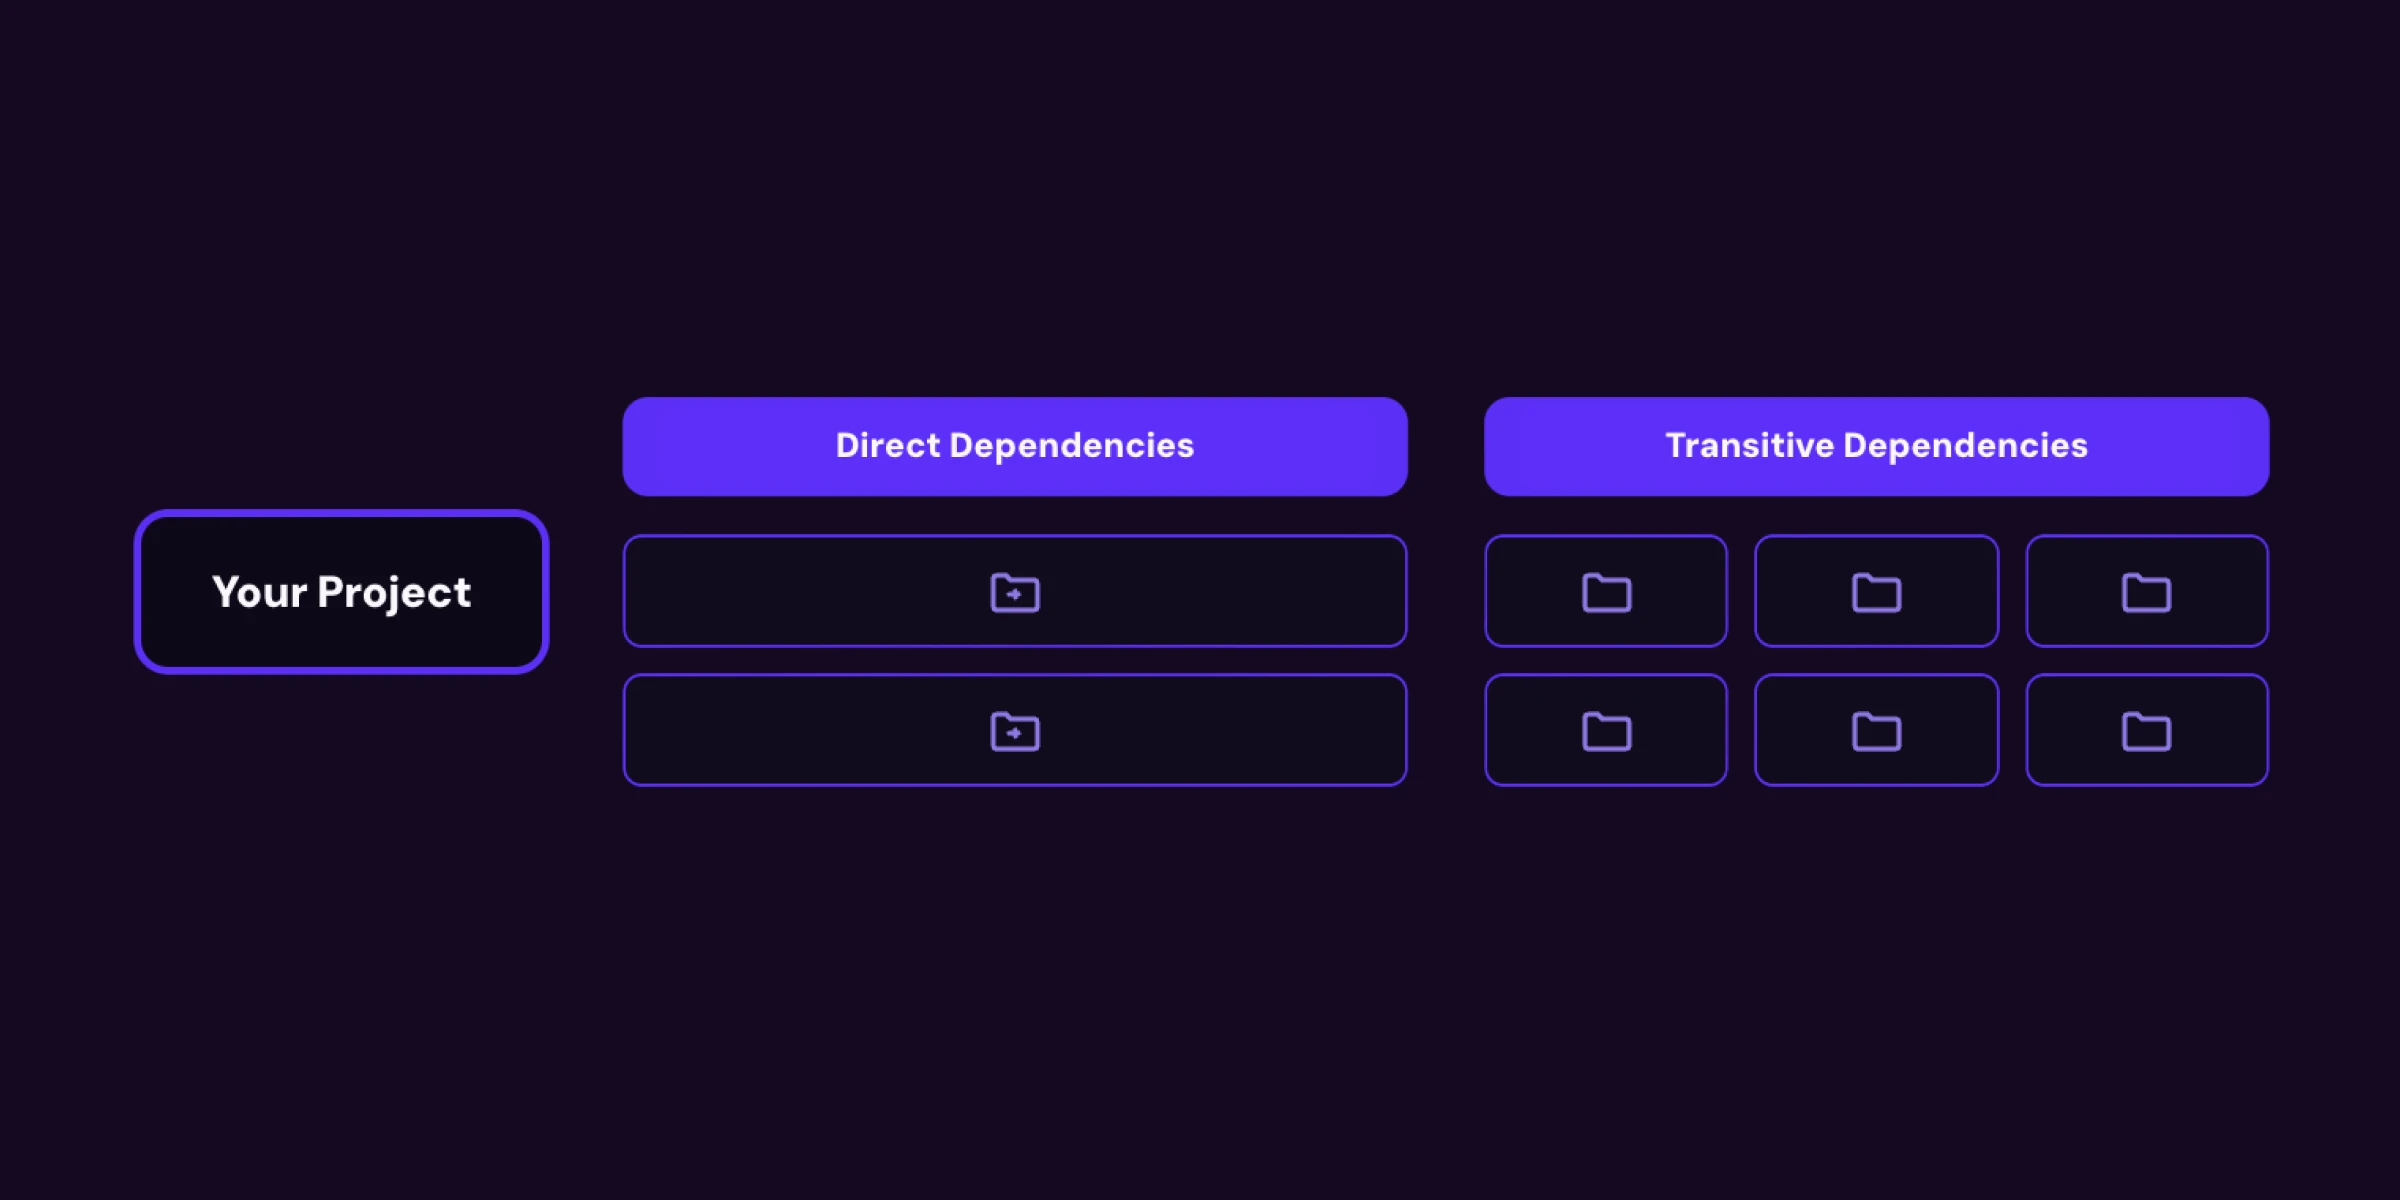
Transitive Dependency Scanning
See everything, not just what’s declared. Every dependency, direct or transitive, scanned to unlimited depth, including private packages in on-prem and private JFrog Artifactory registries. Checkmarx SCA tracks more than 3 million open-source packages across 13+ package managers, so nothing your applications depend on goes uncounted.
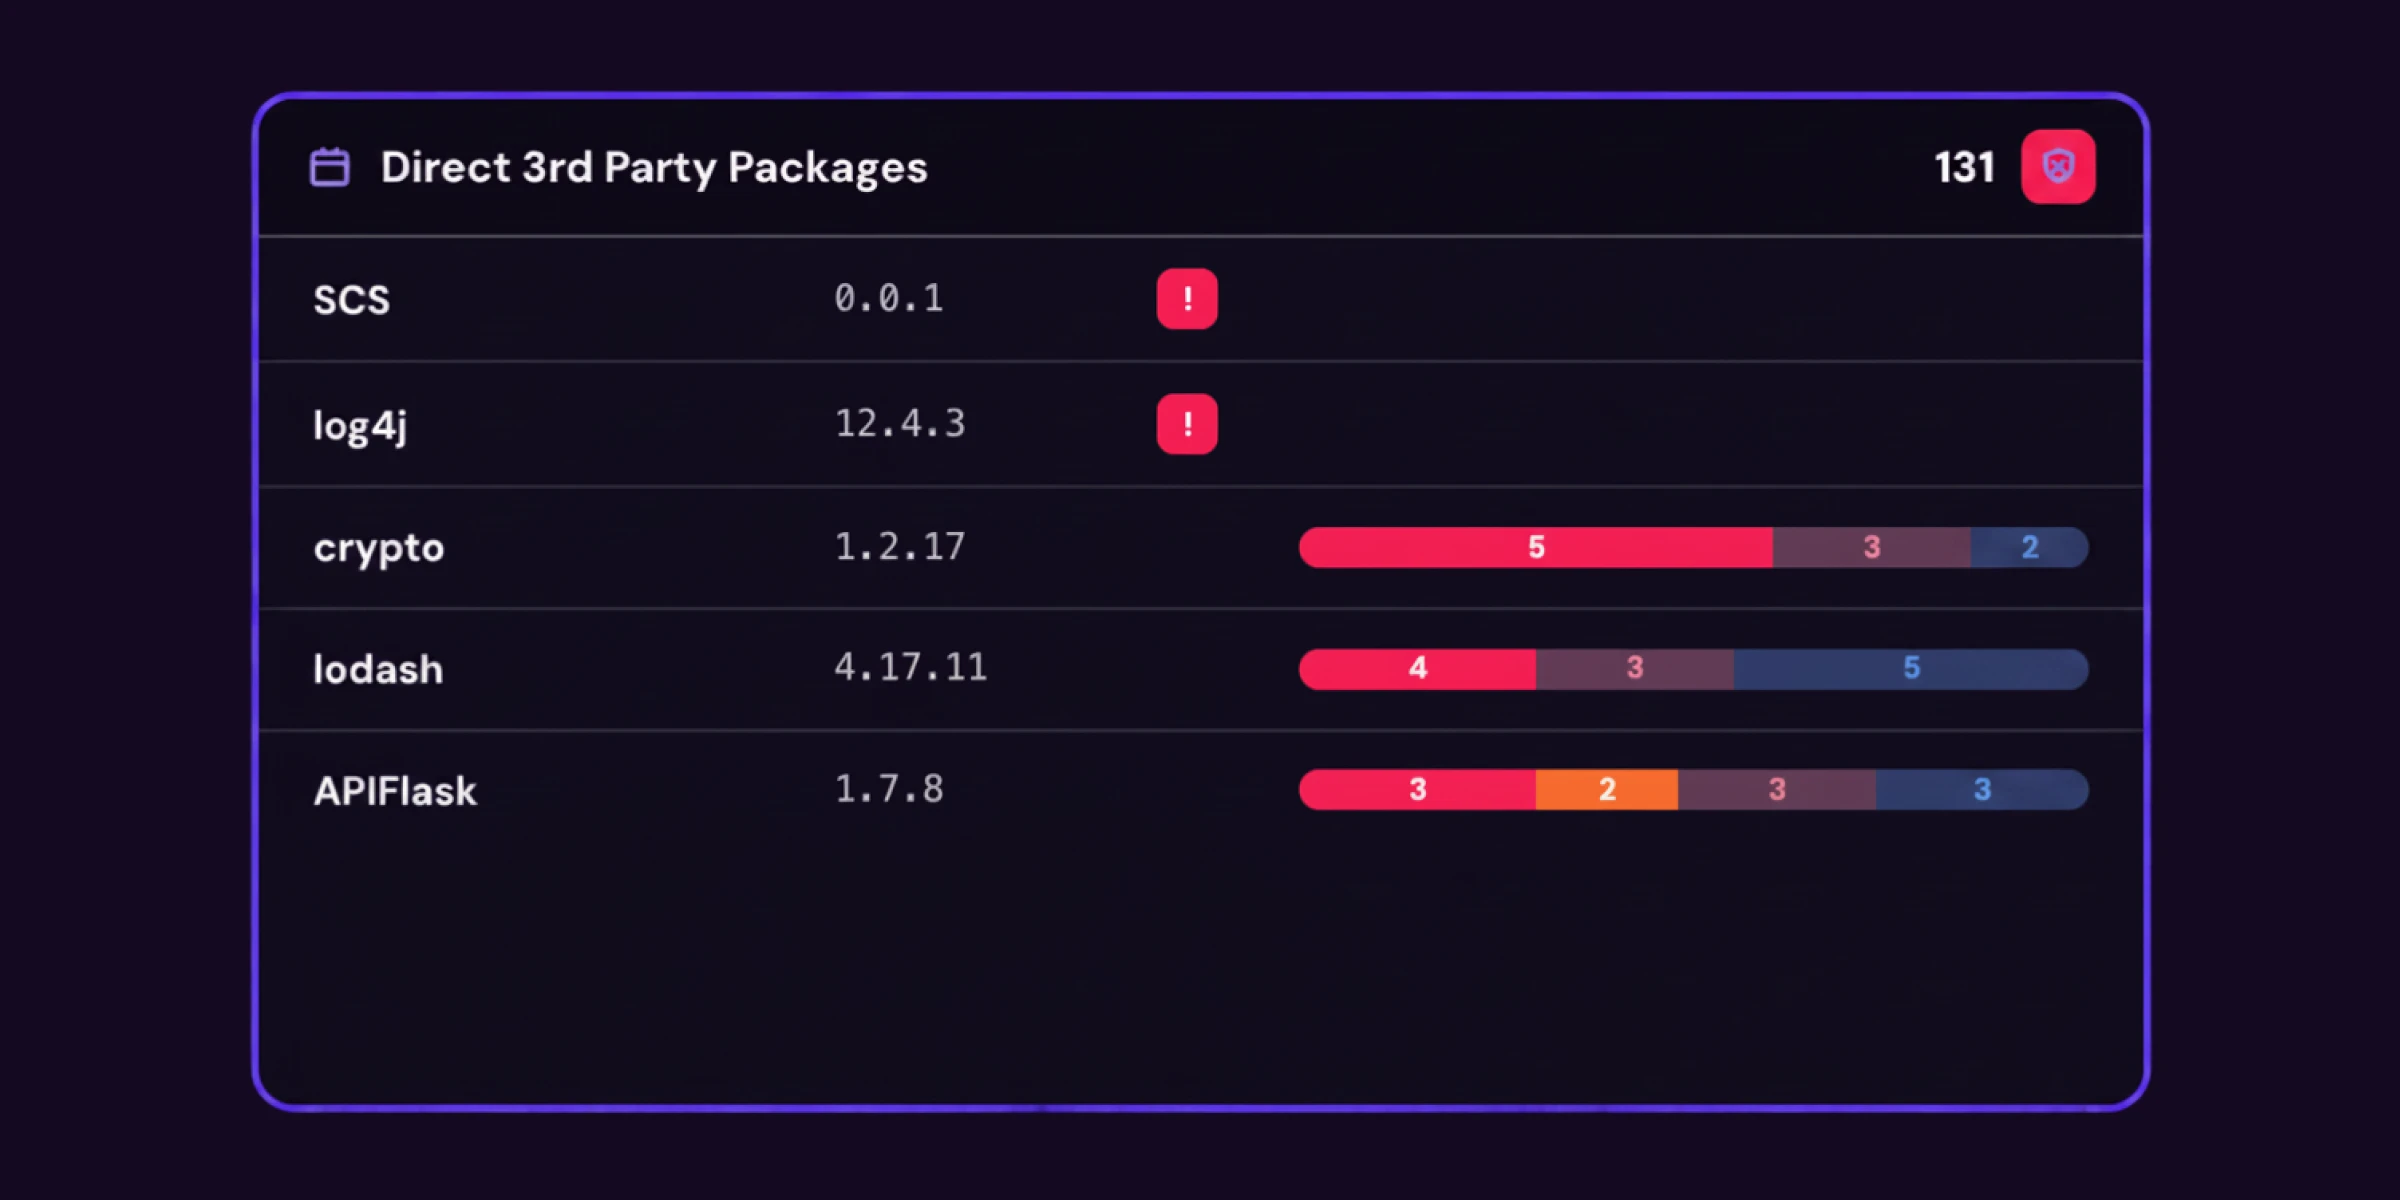
Stop malicious code before it ships
Checkmarx’ industry-leading proprietary database of more than 550,000 malicious packages enables you to identify and remediate any open-source libraries in your applications known to contain malicious code, intercepted before they ever reach your build
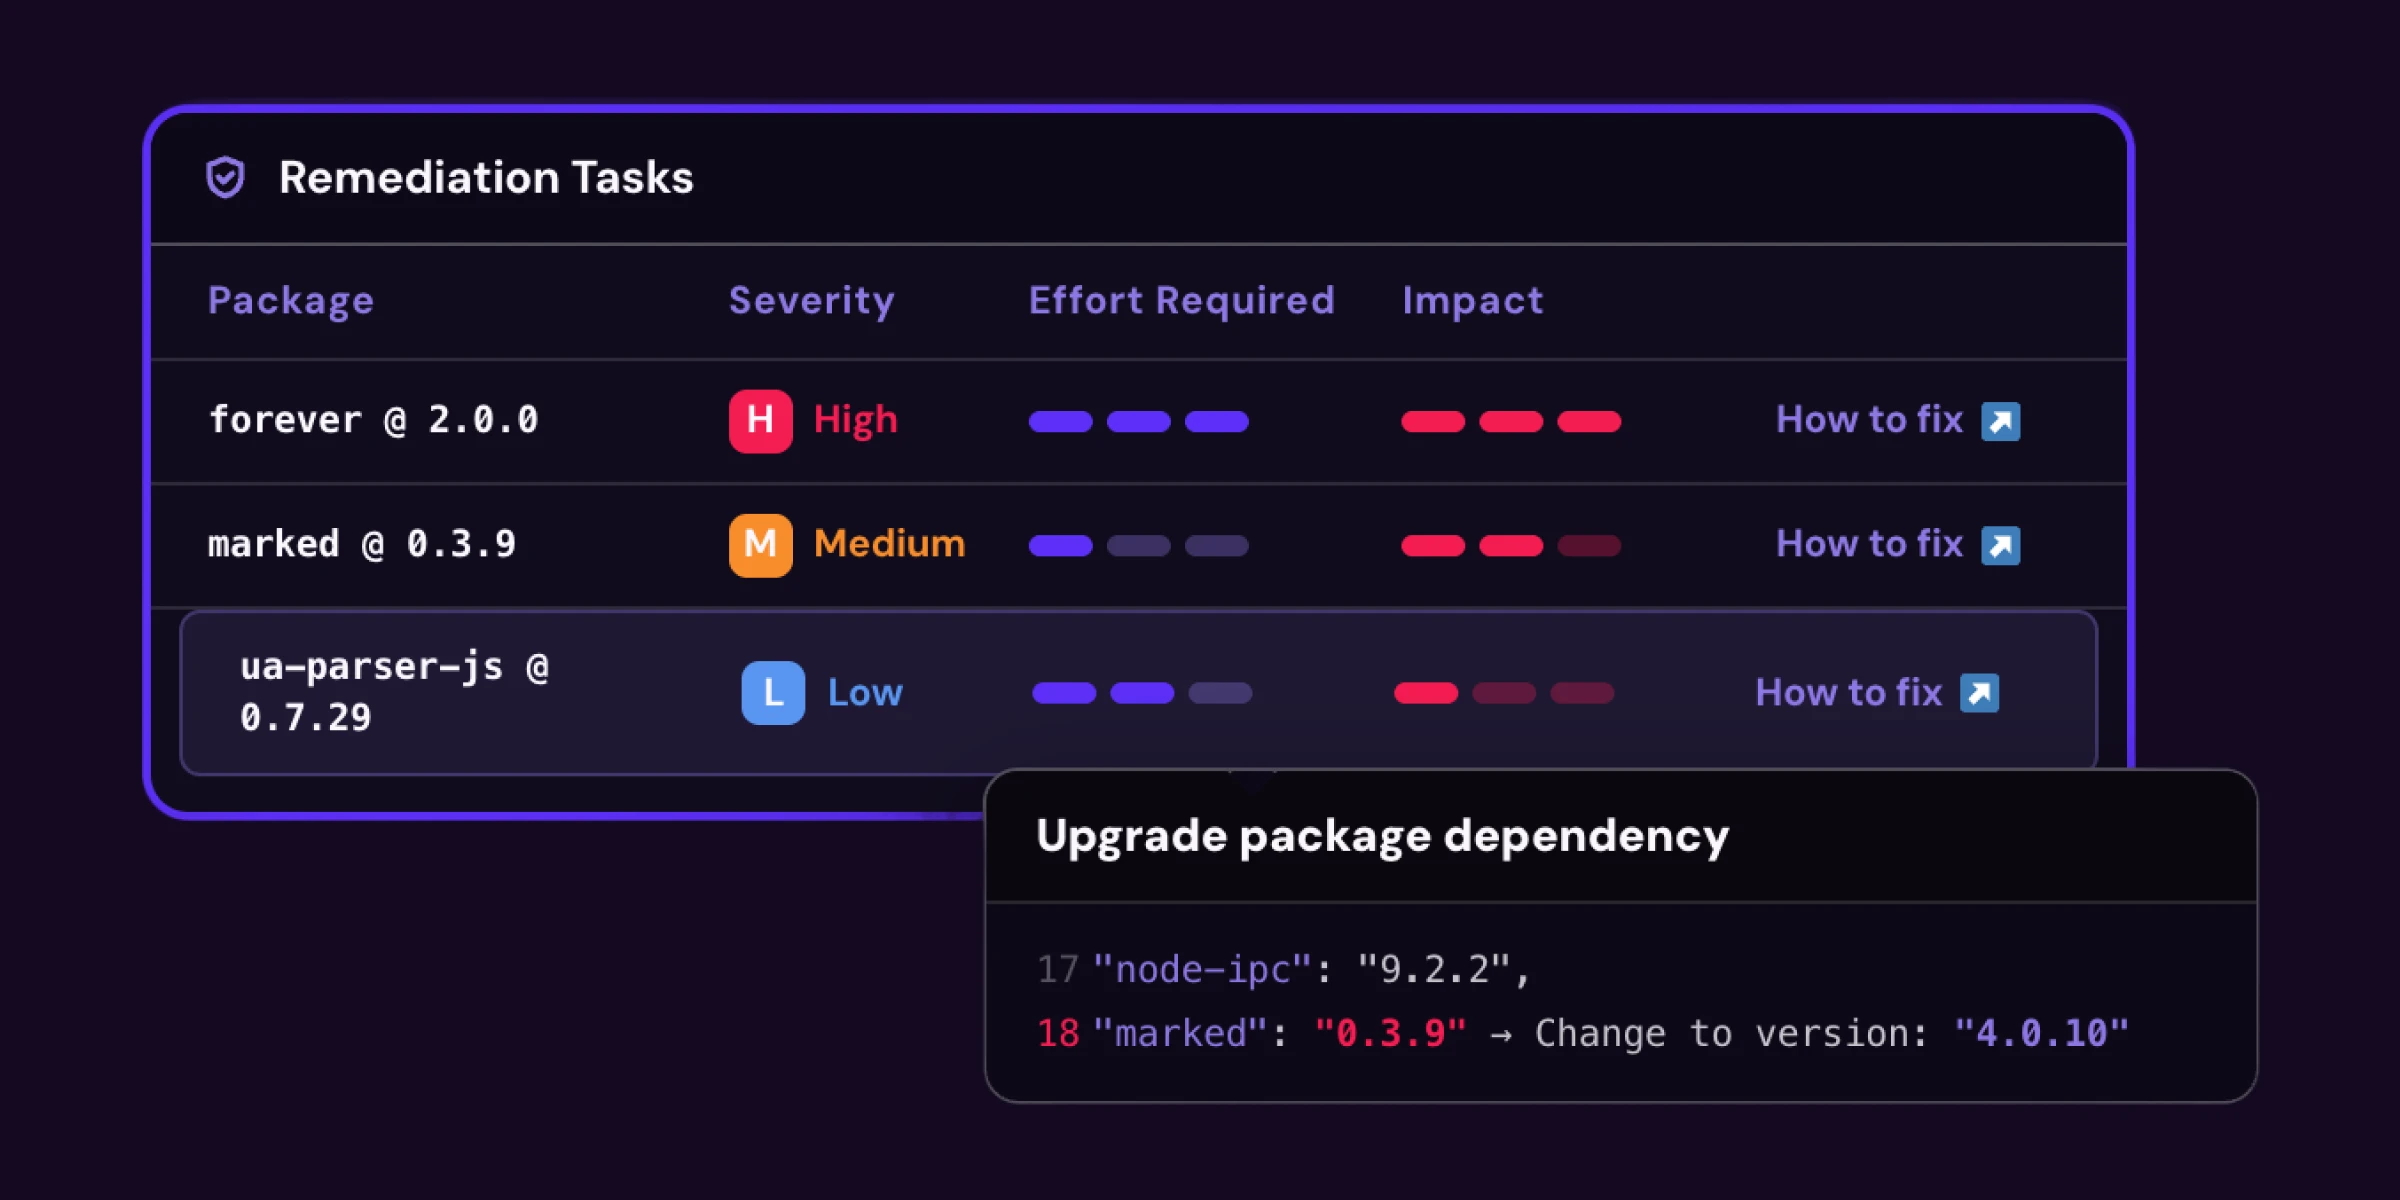
Guide Developers to fix with the least disruption
Dramatically ease and expedite mitigation efforts with actionable remediation guidance, including the expected effort and impact of each fix. Get AI recommendations for more secure alternative packages so your team spends less time deciding what to fix, and more time fixing it.
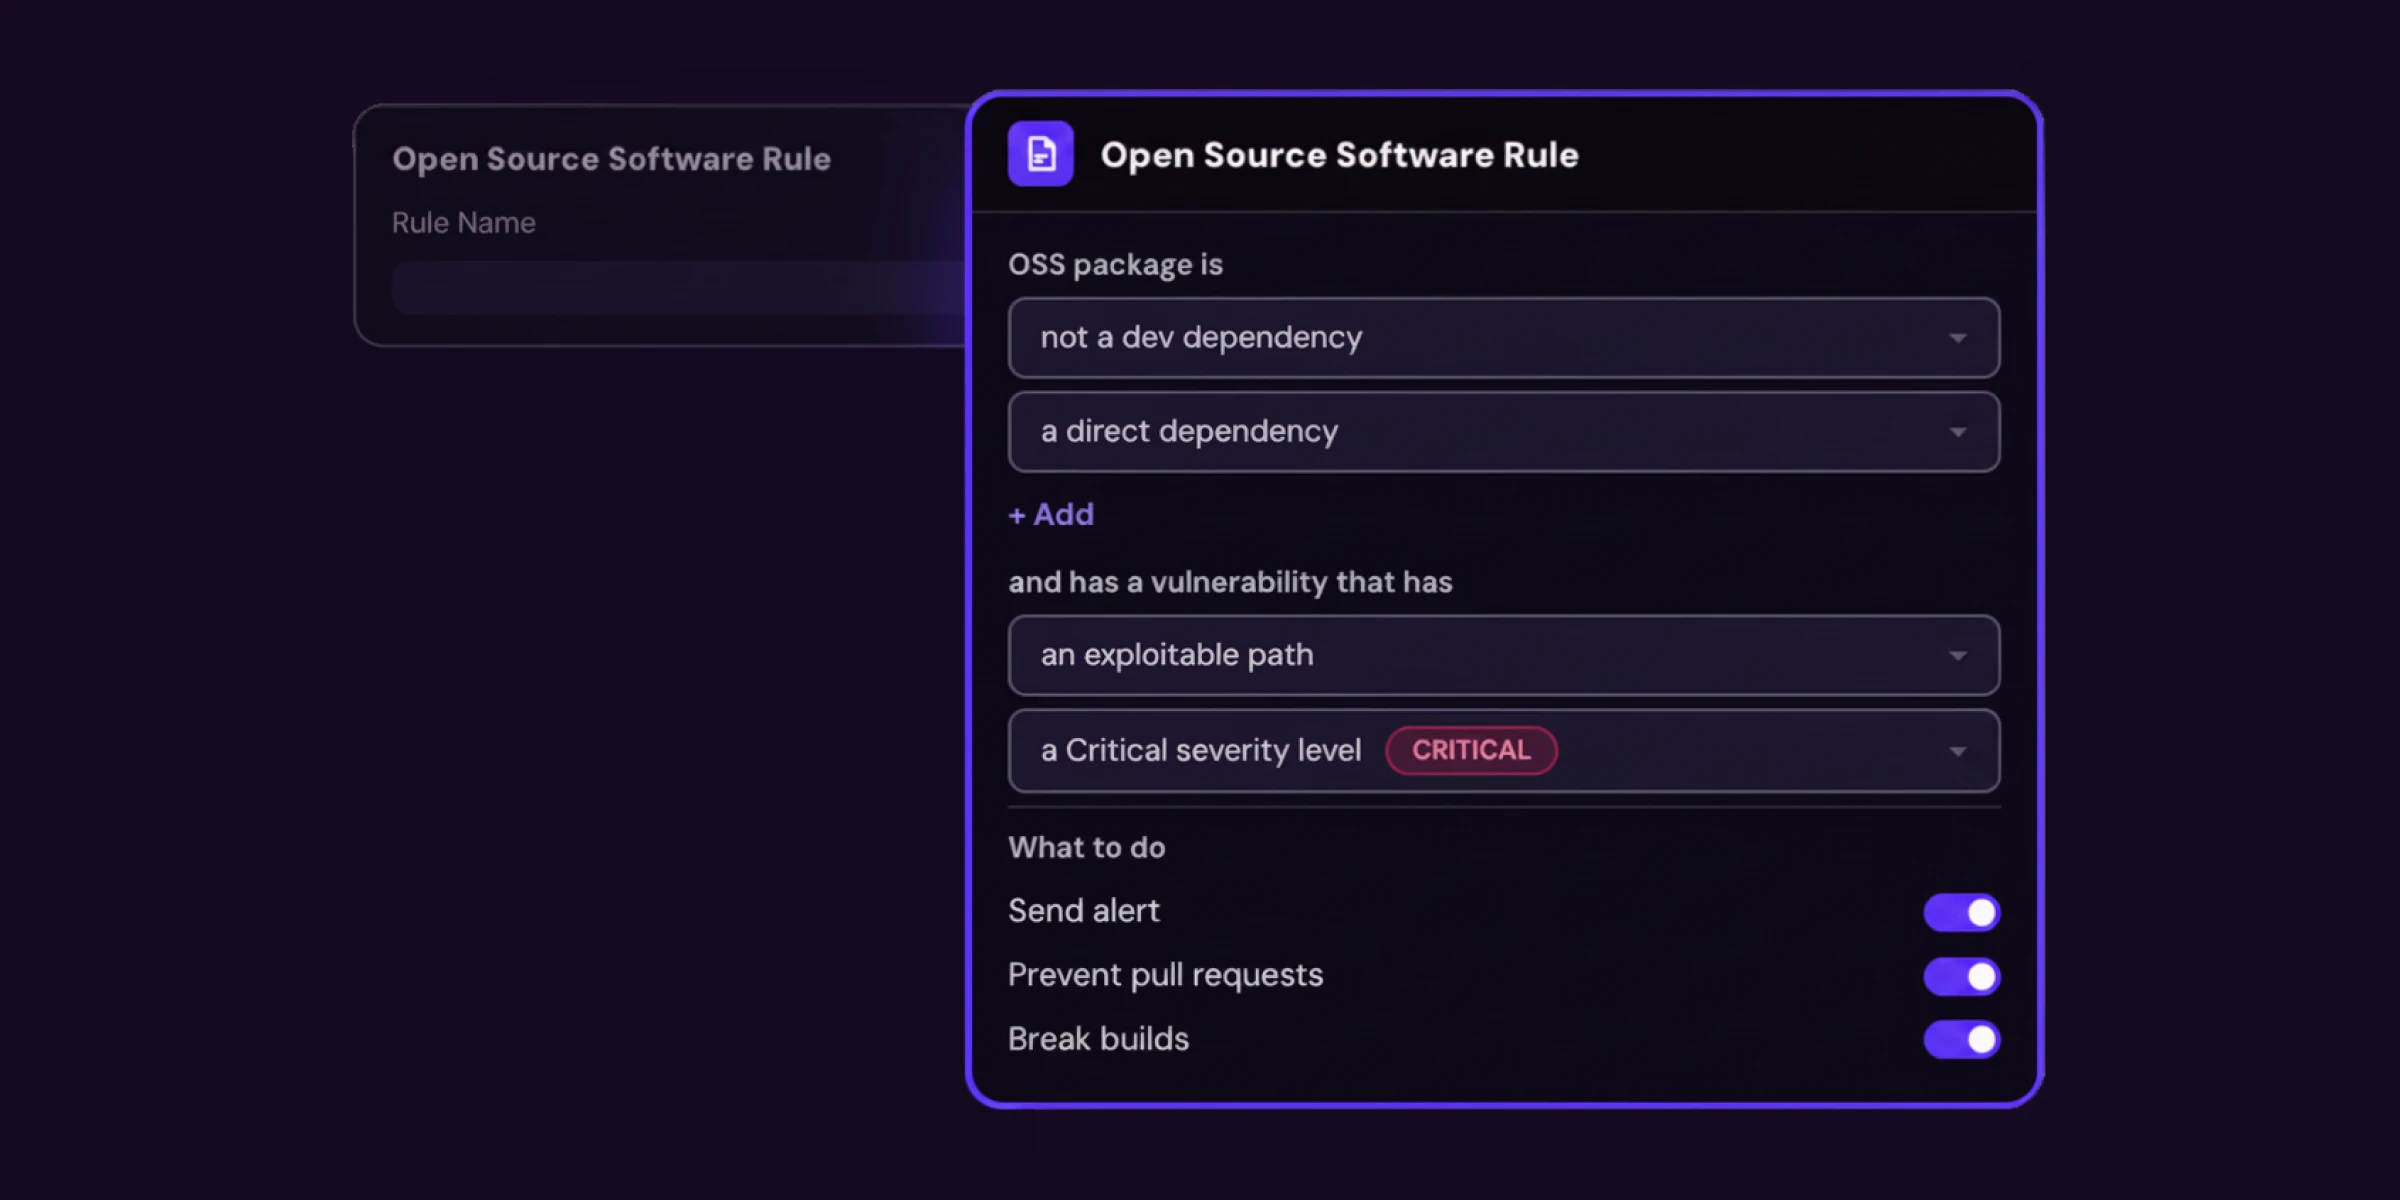
Enforce Policy Rules with Automated Actions
Enforce policy, not just publish it. Configure policies on package characteristics, CVSS severity (up to 4.0), reachability, malicious packages, and licensing to automatically alert, block pull requests, or break the build.
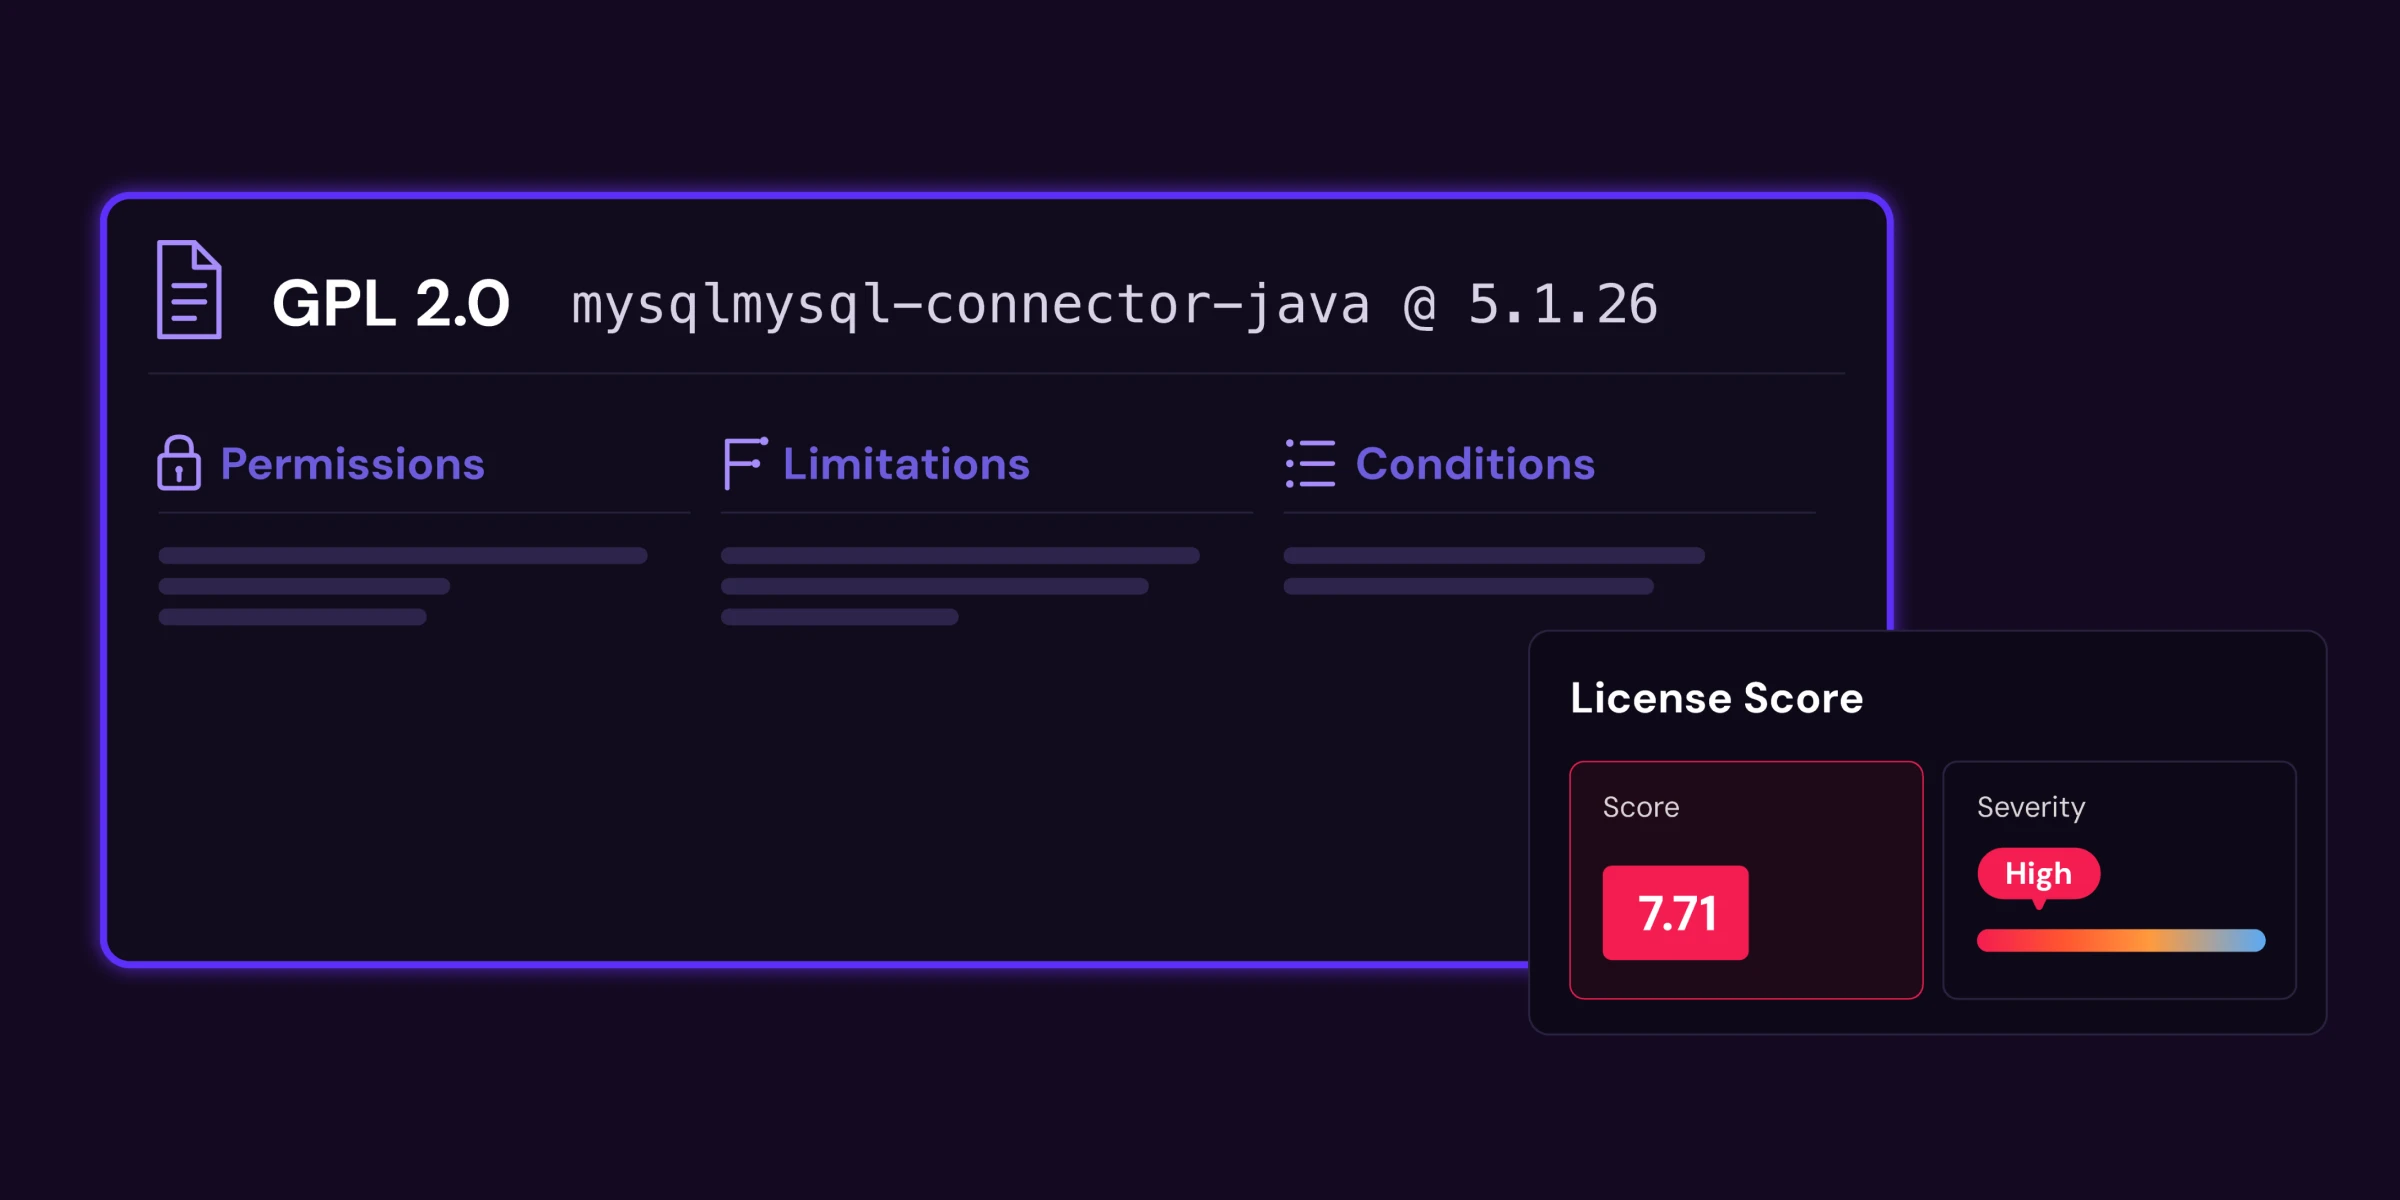
Catch license conflicts before they merge
Ensure awareness and tracking of all relevant third-party code license requirements and restrictions, to avoid potential compliance issues and other legal complications.
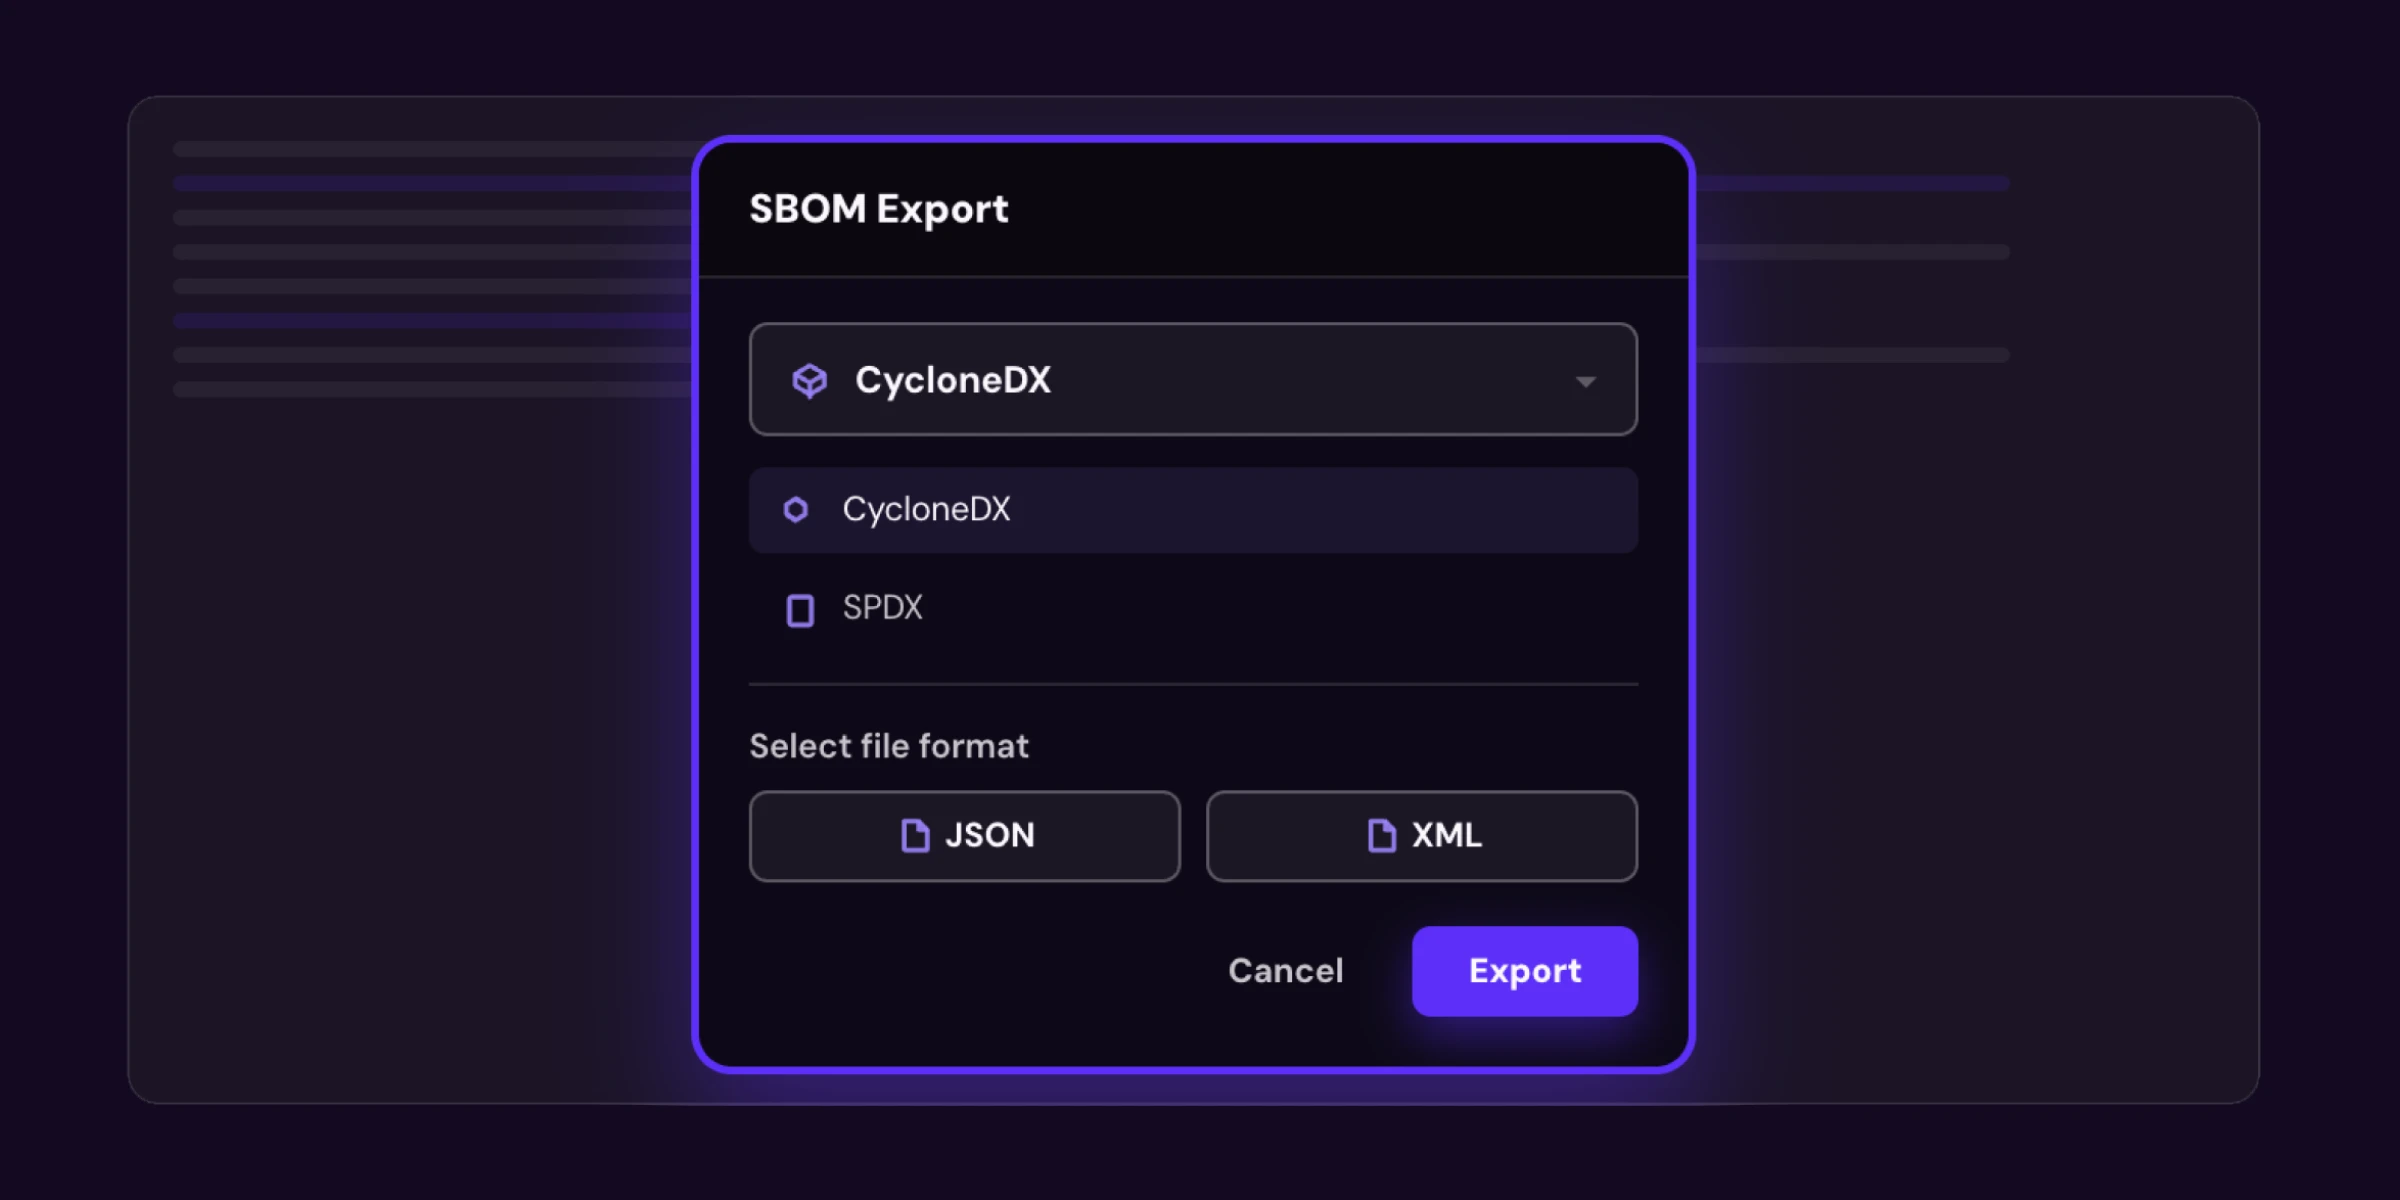
A Complete, Exportable Inventory
Generate and export SBOMs in industry-standard formats such as CycloneDX and SPDX, to inventory the components of your applications and more easily comply with relevant regulatory, policy, and licensing requirements.
The Most Accurate and Automated SCA
Better identify, manage, and remediate open-source risk as an integrated part of your SDLC.


How Organizations Benefit From Checkmarx SCA
Checkmarx SCA cuts false alarms, speeds up fixes, and keeps releases from waiting on a separate security review.

Open source doesn't slow down releases
SCA scans run automatically on every pull request and only block the merge when a real policy is violated so you can confidently utilize open-source software to launch new features and applications faster without interrupting your developers’ workflows

Every open-source risk, prioritized by exploitability
Checkmarx SCA tool deliver one correlated view across vulnerabilities, malicious packages, and license issues in your open-source dependencies, so the next item pulled from the backlog is exploitable vulnerabilities to prioritize and remediate first.

Dependency fixes, not a new dashboard
Developers can create secure applications faster with integrated application security in their existing tools and workflows.
Related Resources
 Revolutionizing SCA With Agentic AI
Discover how to use agentic AI to deliver real-time SCA inside the IDE—catching malicious packages instantly and automating safe fixes
Learn More
 Whitepaper
Capability Without Security: Measuring the Functionality-Security Gap in AI-Generated Code
Learn More
 Report
Tolly Competitive Evaluation
Learn More
 Solution Brief
Software Composition Analysis
Learn More
Why the World’s Top Teams Choose Checkmarx
“We’ve seen an 80% noise reduction — our engineers now focus on the high-quality risks that matter.”Explore Best Buy Case Study
“By far the best AppSec tooling decision we have made”
“Checkmarx gave us a 90% reduction in vulnerabilities in just a few months.”
“Unifying our AppSec tools with Checkmarx gave us a single source of truth.”
“With 2.1B lines of code scanned monthly, Checkmarx gives us the scale and speed we need.”
“Checkmarx fits seamlessly into our DevOps pipelines—it’s a truly scalable solution.”
“From a buyer perspective, Checkmarx’s approach offers a structured and role-aware entry point into agentic security. ”
“Incorporating Checkmarx’s technology has revolutionized our development culture ”
“Checkmarx One made our security team and developers life easier.”
“The success of our AppSec program can be directly attributed to the tooling, processes and support provided by the Checkmarx managed services.”
“Bringing ASPM context directly into the IDE reflects a forward-looking approach to prioritizing security efforts based on risk earlier in the development process.”
Frequently Asked Questions
Checkmarx SCA provides comprehensive coverage and highly accurate results, with full visibility into vulnerabilities, malicious code, and license risks in open-source libraries. Checkmarx analyzes one million packages each month; the company has identified more than 550,000 open-source libraries containing malicious code. Tight IDE, CLI tool, and CI/CD integration make it easy to integrate security workflows, including automatic SCA scan triggering, within existing development and deployment platforms.
Users are provided with prioritized remediation guidance to ensure that the most critical risks are addressed first. Also included are SBOM generation and ingestion, exploitable path analysis, transitive dependency scanning, binary dependency scanning, private package scanning, a risk management dashboard, policy rules with automated actions, and comprehensive reporting.
Static application security testing (SAST) scans proprietary code written by your developers, while software composition analysis (SCA) scans open-source libraries and third-party components.
Checkmarx’ unique exploitable path analysis is an advanced form of reachability analysis that accurately determines which vulnerable classes or functions within third-party libraries may be called by an application at runtime. By prioritizing code that is potentially exploitable when the application is published (versus other vulnerabilities that are not currently being called by the application and are thus not readily exploitable), developers can remediate the most dangerous libraries first.
An SBOM is a file that helps organizations see an application’s makeup to assess and address the security risk across all its underlying components.
Software Composition Analysis is a proactive approach to securing third-party code which is in line with modern security principles of continuous monitoring and early detection of potential threats. By preemptively addressing security risks and compliance issues, developers can focus on coding and continue to confidently leverage open-source libraries and components, while ensuring applications are secure.
Checkmarx SCA easily integrates into your CI/CD pipeline, works seamlessly with a wide variety of CI/CD tools, including Jenkins, Azure DevOps, GitHub Actions, and TeamCity.
Software Composition Analysis (SCA) differs from traditional security testing by focusing on identifying vulnerabilities and malicious code in open-source and other third-party components within an application. Rather than testing for flaws in proprietary code, SCA examines dependencies for known security risks, licensing issues, and outdated versions, enabling faster remediation of vulnerabilities in widely used external libraries.
Checkmarx SCA is available on the Checkmarx One platform. Developers can get it free within JetBrains’ IntelliJ IDEA Ultimate and Visual Studio Code plugins.
Open-source components are widely used in modern software development, yet they can introduce vulnerabilities or malicious code into applications. Software Composition Analysis (SCA) tools identify these risks early, enabling quick remediation and empowering developers to continue leveraging open-source components confidently. This approach supports developer productivity while ensuring the security and stability of the codebase.
Get Checkmarx SCA Today
Learn why enterprises across the globe rely on Checkmarx SCA to manage the risks associated with open source and other third-party dependencies.
Thank You!
Your Custom Checkmarx Demo Request was Successfully Sent!
Get a Custom Demo
Easily Manage Open Source Risks
Go hands-on with our SCA by booking a personalized demo with one of our AppSec experts.
The Highest Scan Accuracy:
Feel trust in a detection that beats the rest on all key metrics, including zero false positives
Let Your Devs Work:
Make the most of open source code by automating SCA scans for friction free security.
Enhance DevEx:
Experience tools that work in the IDE so devs can secure applications without interrupting workflow.
Focus On What Matters:
Save time with an SCA that tells you what to fix first by correlating insights.
Industry Leading Protection:
Trust our database of more than 420,000 malicious packages to identify and remediate potentially dangerous source libraries.
Get Started With
Checkmarx SCA Today
Keep open-source risks in check with industry-leading SCA tools