
The Ultimate Semgrep Alternative:
Built for Scale. Trusted by Devs.
Semgrep’s lightweight, open-source static analysis can leave critical security gaps. Checkmarx delivers deep, end-to-end coverage for application security that matches your dev velocity.
Here’s why teams that started on Semgrep land on Checkmarx.
Application Security That Matches Your Devs Velocity
Rules only catch what you write them to catch. Checkmarx proves what’s exploitable, across the entire AI-DLC, from the first line of AI-generated code to production, and fixes it automatically, so security never becomes the bottleneck in your pipeline.

Integrated AppSec. No Silos. No Gaps.
Semgrep misses half your risk surface, while Checkmarx secures human and AI-generated code across every stage of the SDLC -including SAST, SCA, IaC, API, DAST, secrets, containers, and ASPM – all in one platform.

Security Built into How Developers Already Work
Developer Assist catches and fixes issues before they’re ever committed, natively in the IDE, SCMs, and CI/CD, with real-time AI remediation and secure code training built in. Security that moves at developer speed, not friction bolted onto a scanner.

Fewer False Alarms. Faster Fixes.
Semgrep’s noise slows teams down. Checkmarx runs every finding through an independent validation layer, cutting false positives by up to 60%, then prioritizes what’s left by real exploitability and opens a fix PR automatically. Less noise in, faster fixes out.
Checkmarx vs. Semgrep: full breakdown
| Capability | Checkmarx One | Semgrep |
|---|---|---|
| AppSec Coverage | ✓ WIN SAST, SCA, IaC, API, Container, Supply Chain, ASPM – unified and correlated on a single AppSec platform | SAST + Supply Chain (SCA) + Secrets; No native IaC, API, container, or DAST coverage — gaps remain outside the code layer |
| SAST Accuracy, Fidelity & Depth |
✓ WIN
Mature engine, customizable queries, exploitable path. Concurrent deterministic + LLM-based engines, across all core languages plus AI-generated-code languages. Highest-fidelity in industry of F1 0.74 with Checkmarx Fusion vs. ~0.20 industry average. |
Rule-based pattern matching (YAML), extended with Multimodal's LLM reasoning layer. Fast, but pattern-matching finds what you write rules for — it doesn't trace data flow the way deterministic SAST does |
| SCA | ✓ WIN Reachability, exploitable path, malicious package detection, license risk, full SBOM generation | Supply Chain product available; less mature on malicious package detection and SBOM depth than a dedicated SCA platform |
| Rule quality | ✓ WIN Curated and maintained by dedicated rule engineering team, backed by decades of Checkmarx Zero research | Community + vendor-authored YAML rules; quality varies and typically requires internal vetting at enterprise scale |
| AI-Powered Triage & Remediation | ✓ WIN Triage & Remediation Assist auto-prioritizes reachable findings and opens fix PRs. Developer Assist fixes issues pre-commit in the IDE. All included as part of the Checkmarx Assist agent family. | Semgrep Guardian scans AI-written code in the IDE in real time; Multimodal adds LLM-based triage/reasoning on top of rules. Newer capabilities, still narrower in scope than a full remediation loop across the SDLC |
| Application Security Posture Management | ✓ WIN Native ASPM with policy engine, third-party scan ingestion, prioritization, IDE integration | No native ASPM; posture and cross-tool correlation would require a separate platform |
| DAST & Runtime Security | ✓ WIN Native DAST and runtime correlation | Not offered |
| Supply Chain Security | ✓ WIN 500k+ malicious packages, repo health, ChainJacking protection, repo health, SBOM | Dependency scanning; less depth on malicious packages and repo health |
| Container & API Security | ✓ WIN Native support for container scanning and API security | Not offered |
| AI Supply Chain Security | ✓ WIN Inventories and governs every AI asset (models, MCP servers, agents, LLM usage) mapped to EU AI Act, ISO 42001, and NIST AI RMF. AI-BOM generation. | Guardian scans the AI-generated code, but doesn't inventory or govern the models, MCP servers, or agents producing it |
| Support + Services | ✓ WIN Premium support, AppSec maturity assessment, dedicated TAM | Self-serve and community-led; enterprise support available with paid tiers |
| Reporting & Dashboards | ✓ WIN Application Risk Management with executive-level posture views | Reporting focused on findings; limited executive views |
| Enterprise Readiness | ✓ WIN Multi-tenant cloud, on-prem, hybrid; deployed at Fortune 100 scale | Cloud and self-hosted options; enterprise governance and compliance tooling still maturing |
Truly Secure Code at the Speed of AI Development
See how Checkmarx One stacks up in an objective custom comparison for your use case.
From comprehensive hybrid scanning to AI-powered remediation, Checkmarx One keeps security in step with how modern teams build.


Why Checkmarx Is Better Than Semgrep
Semgrep was built for developers, not enterprises – Checkmarx is built for both, embedding AppSec directly into the workflow so developers fix faster and stay in flow.
Semgrep Can’t Scale. Checkmarx Can.
Lightweight open-source static analysis tools weren’t built for enterprise risk. When governance, visibility, and compliance matter, Semgrep’s static scans and shallow insights fall short. Checkmarx delivers 100% codebase coverage, 70% faster compliance reporting, analytics, and dashboards built for real enterprise visibility to deliver application security that grows with you instead of slowing you down.

High-Fidelity Detection Across Every Layer
Gaps in rule quality leave your code exposed. Semgrep’s open-source rules lack consistency and enterprise validation, leading to false positives and missed vulnerabilities. Checkmarx Fusion pairs deterministic, rules-based precision with a multi-model AI engine that reasons over code the way no single model or rule set can, backed by Checkmarx Zero intelligence and validated before every result reaches you, leading to an F1 score nearly four times the industry average, with 60–70% fewer false positives than standalone AI scanning.
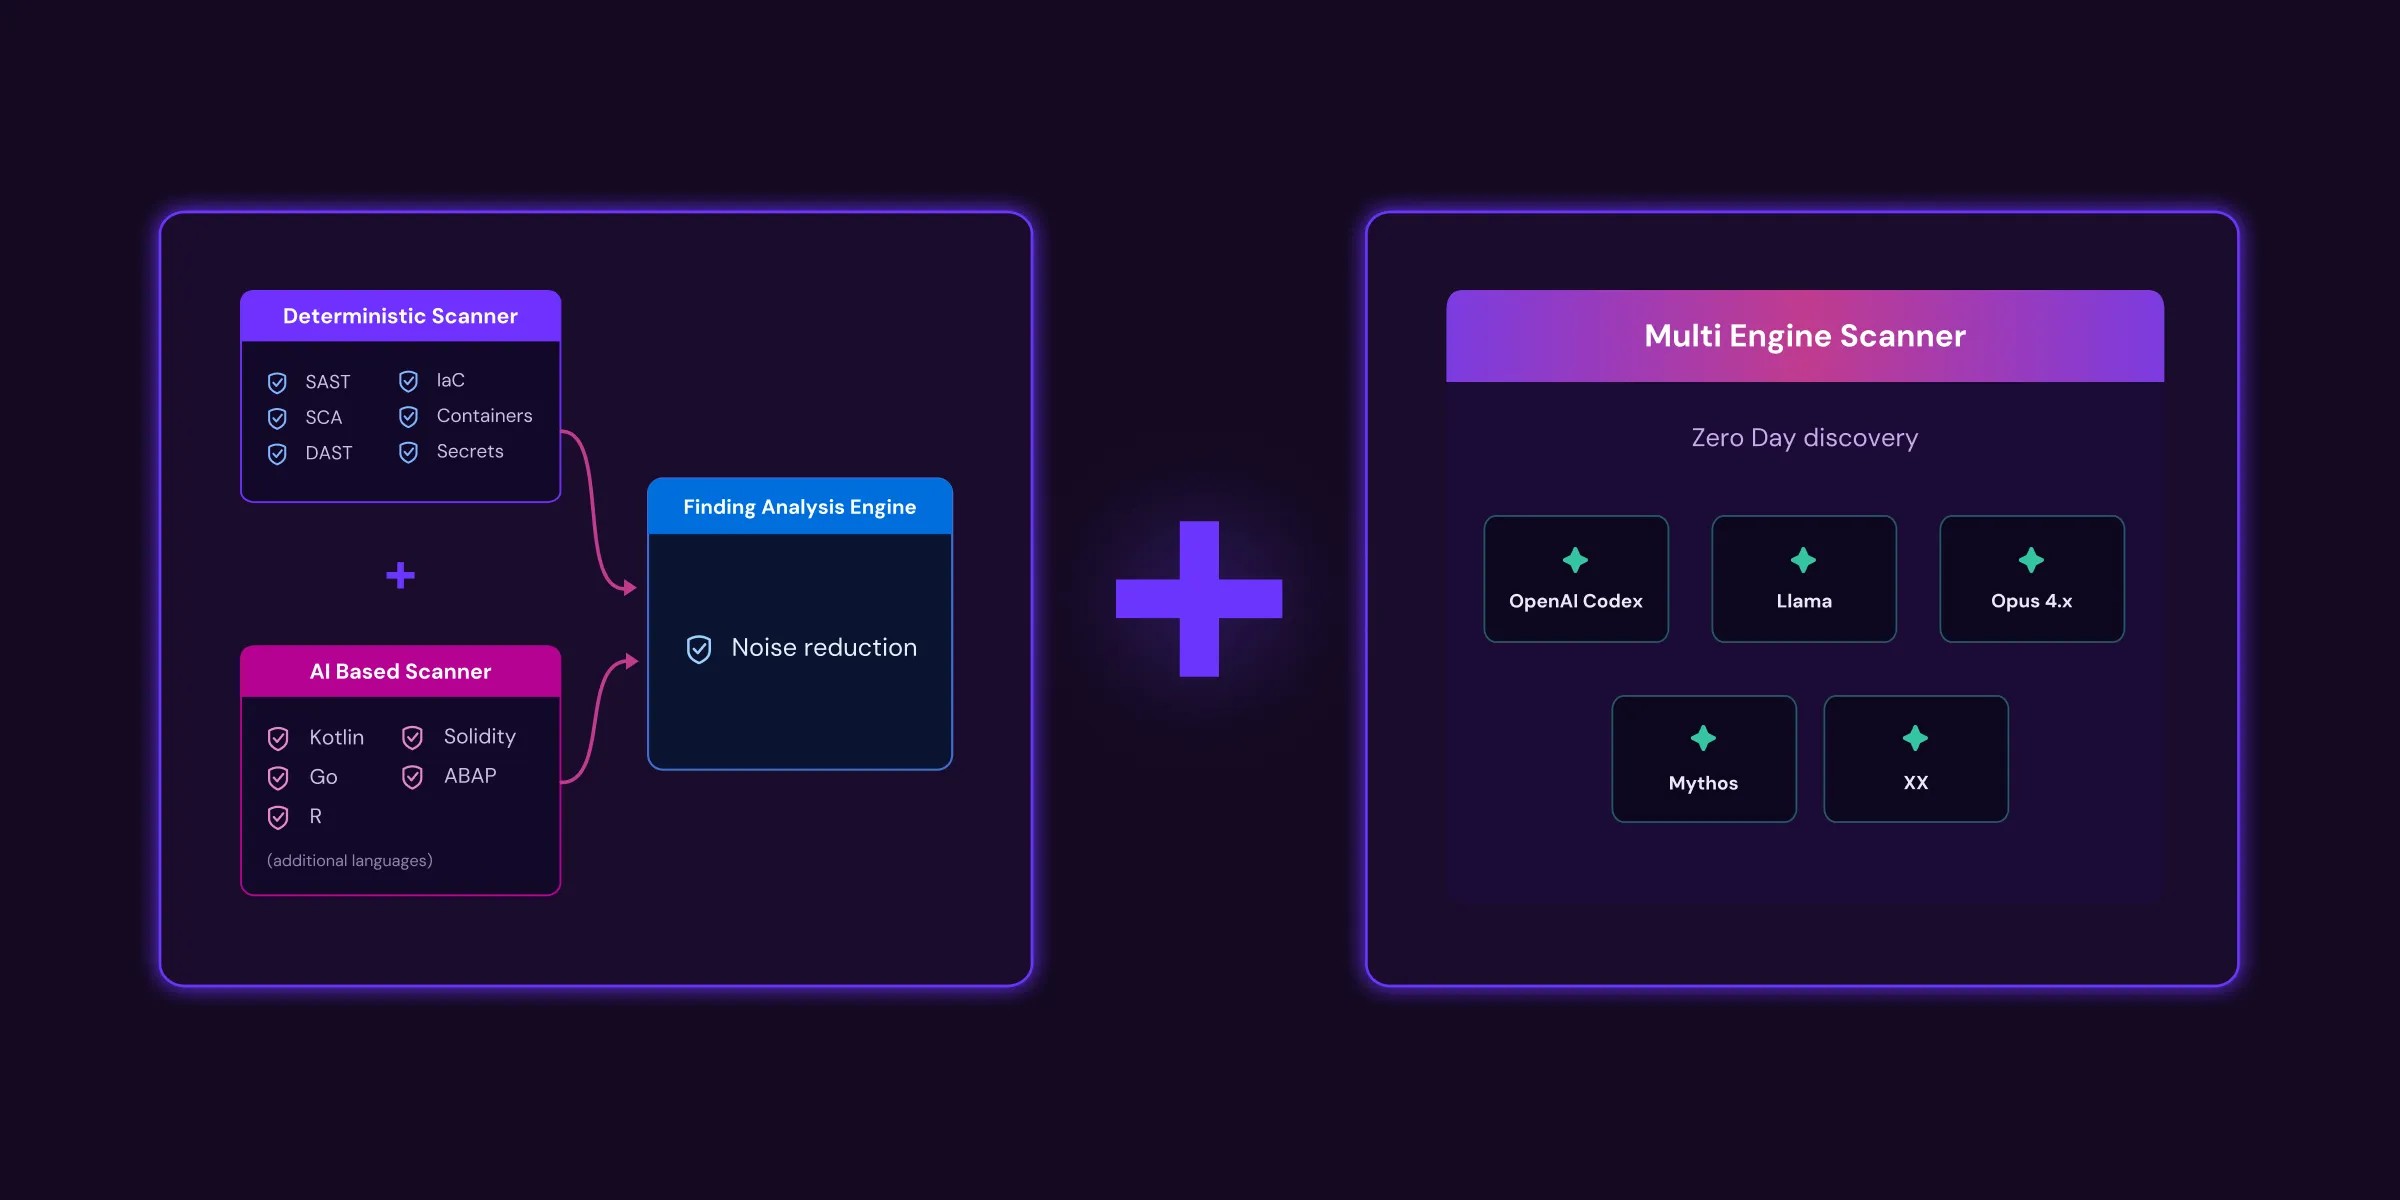
Resolve issues 5–7x faster in the IDE
Fix once, fix right, with automated remediation across the full code path. Checkmarx One Assist delivers real-time remediation in the IDE, automatically scanning, validating, and fixing insecure AI or developer-written code, reducing rework and keeping delivery moving without breaking developer flow.

Why the World’s Top Teams Choose Checkmarx

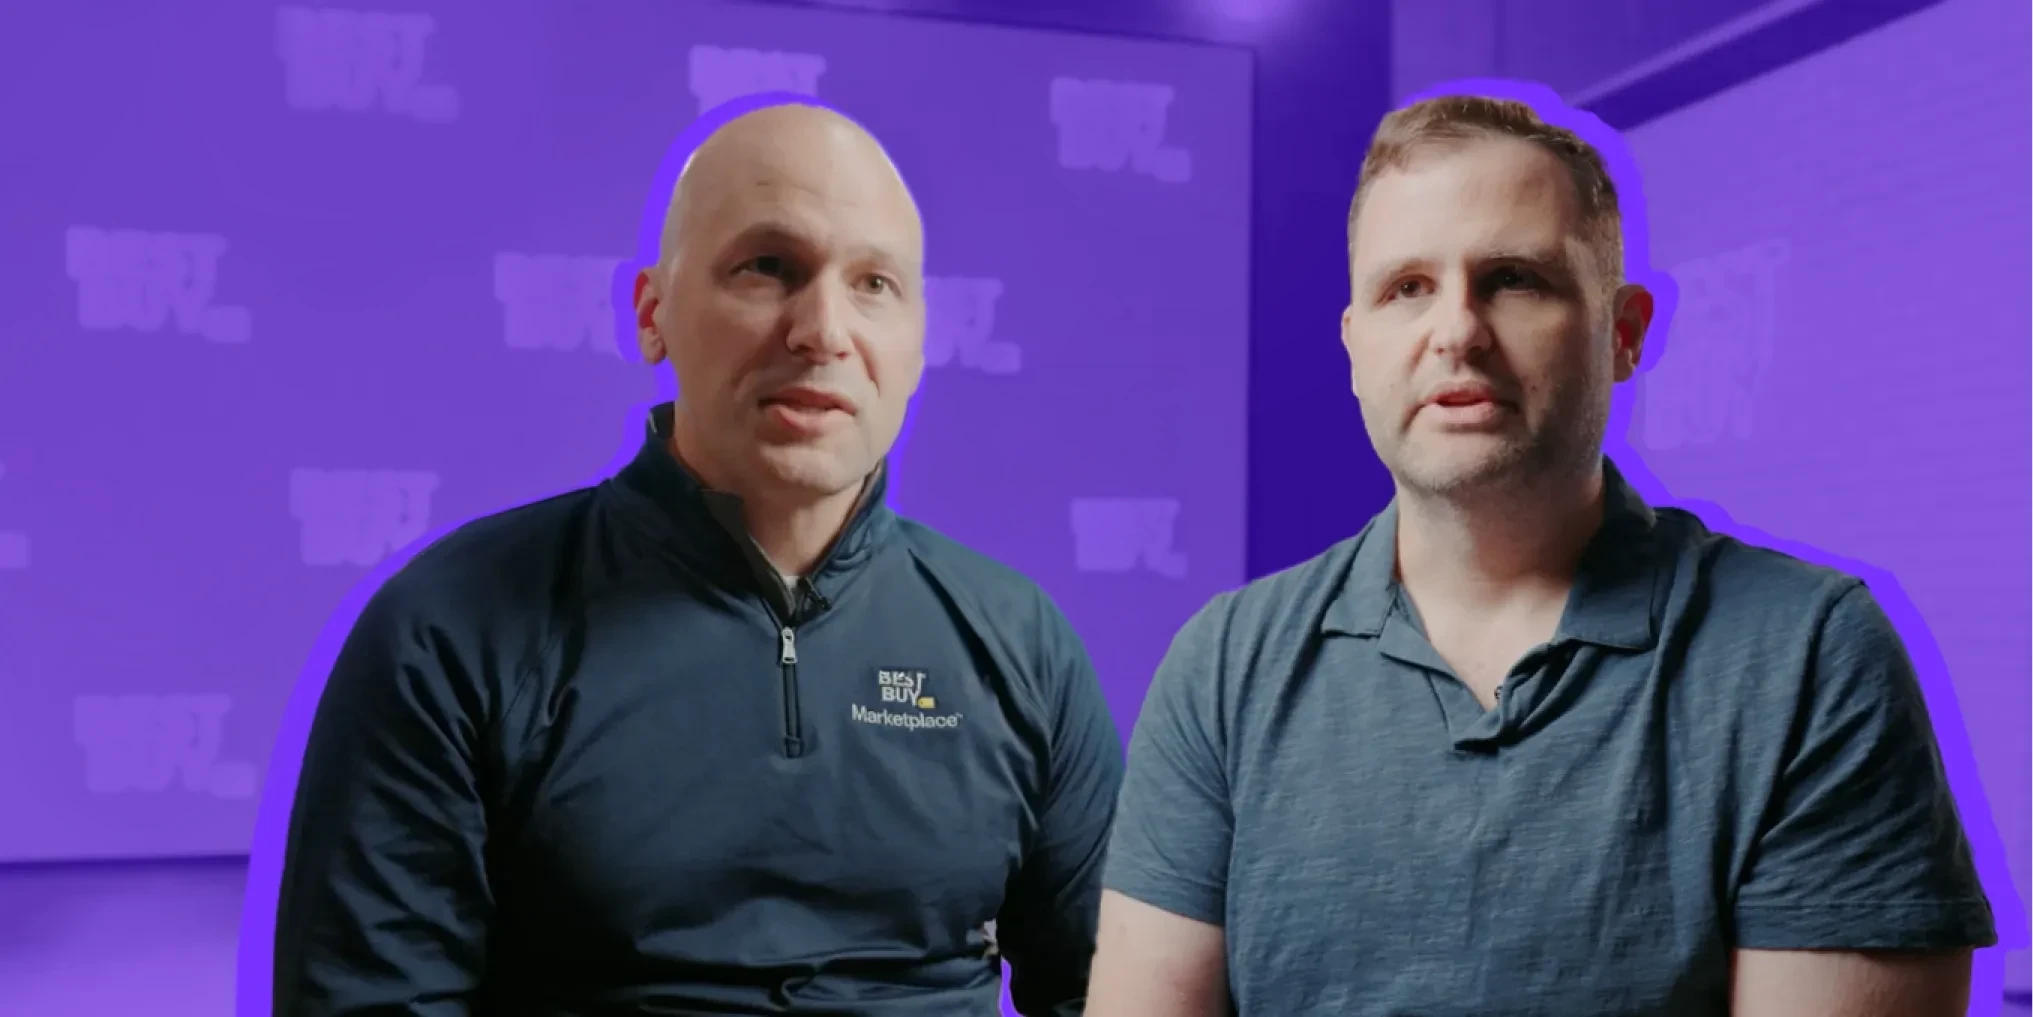
“We’ve seen an 80% noise reduction — our engineers now focus on the high-quality risks that matter.”Explore Best Buy Case Study
“By far the best AppSec tooling decision we have made”
“Checkmarx gave us a 90% reduction in vulnerabilities in just a few months.”
“Unifying our AppSec tools with Checkmarx gave us a single source of truth.”
“With 2.1B lines of code scanned monthly, Checkmarx gives us the scale and speed we need.”
“Checkmarx fits seamlessly into our DevOps pipelines—it’s a truly scalable solution.”

“From a buyer perspective, Checkmarx’s approach offers a structured and role-aware entry point into agentic security. ”
“Incorporating Checkmarx’s technology has revolutionized our development culture ”
“Checkmarx One made our security team and developers life easier.”
“The success of our AppSec program can be directly attributed to the tooling, processes and support provided by the Checkmarx managed services.”

“Bringing ASPM context directly into the IDE reflects a forward-looking approach to prioritizing security efforts based on risk earlier in the development process.”
See it in action
See why Checkmarx is Better
Speak to an expert to explore how Checkmarx meets your critical application security needs.
Thank You!
Your Custom Demo Request is successfully sent.
A member of Checkmarx Team would contact you shortly to set up your custom demo.
Personalized Demo
See Where Checkmarx Wins
Integrated AppSec
SAST, SCA, IaC, API, Container in one platform, no silos
Curated rules at scale
Mature, tuned, vetted – not crowdsourced
Resolve issues 5–7x faster
With AI-guided remediation, not just findings
Enterprise governance
ASPM, AI-BOM, SBOM, Compliance-ready
See Why Checkmarx Is Better Than Semgrep
Checkmarx embeds AppSec directly into the developer workflow, so developers fix faster and security teams stay in control. See what broader coverage, faster fixes, and enterprise-grade governance look like in practice.