Full AppSec Coverage,
Zero Developer Disruption
SCA-only security isn’t enough. Get 360° AppSec coverage with Checkmarx that scales as fast as your code.
Full AppSec Coverage with Reachability that Doesn’t Stop at Open Source
Endor Labs is fine for open-source security and risk management, but that’s where it ends. Checkmarx delivers complete application security across the AI-DLC, with the highest fidelity in the industry, so you scale security as fast as your code.

One Platform. Zero Blind Spots.
Endor Labs stops at SCA and AI code governance. Checkmarx secures every layer of your application across your software supply chain, with native SAST, SCA, IaC, API security, container scanning, DAST, secrets detection, and ASPM, all in one platform. No gaps. No tool sprawl.

Proprietary Exploitable Path Analysis
Reachability isn’t enough. It creates noise, blind spots, and missed coverage that Endor Labs can’t solve. Checkmarx combines exploitability prioritization and advanced analysis to deliver clarity, fewer false positives, and actionable results, so you focus on real risk.

Built for Developers. Trusted by Enterprises.
Security shouldn’t slow you down. Checkmarx delivers AI-powered protection and continuous find-fix-verify loops, securing human-written and AI-generated code with native IDE, SCM, and CI/CD integrations for real-time remediation and code security at speed.
Checkmarx vs Endor Labs: Key Differences
| Capability | Checkmarx One | Endor Labs |
|---|---|---|
| AppSec Coverage | ✓ WIN Secures the entire AI SDLC covering SAST, SCA, IaC, API, Containers, DAST, Secrets, and AI Code and AI Supply Chain. | Strong on OSS dependency risk and AI code governance; no native DAST, ASPM, IaC, container, or API security. Requires stitching in other tools. |
| SAST Accuracy & Depth |
✓ WIN
Highest fidelity with an F1 score of 0.64 vs industry average of ~ 0.20. This reflects highest accuracy and recall. <br /> <br /> Deep analysis across all languages and 80+ frameworks. Advanced AI and correlation reduce noise and false positives by up to 90%. Strong accuracy on complex flows, multi-file analysis, and compliance coverage. |
Basic flow analysis, limited rules management. Higher noise and limited language support. SAST not core focus. |
| SCA | ✓ WIN Reachability analysis, license risk, integrated risk insights, and actionable remediation guidance, full SBOM support and generation. Zero false positive rate in independent testing, against 10% for the next-best competitor. | No reachability for C/C++, Rust, Ruby, Swift/Objective-C, PHP. |
| Rule quality | ✓ WIN AI-enhanced and curated by insights of security research team, to stay on top of evolving risks. | Heavily reliant on Opengrep with “curated” rules. |
| Application Security Posture Management | ✓ WIN Native ASPM. Cross-Scanner correlation. Embedded in IDE, unified policy enforcement, risk-based prioritization, engineering and executive dashboards. | No native ASPM. Posture management and cross-scanner correlation require a separate tool. |
| DAST & Runtime Security | ✓ WIN Native DAST capabilities, cloud insights and CNAPP integrations | Not offered |
| Supply Chain Security | ✓ WIN Advanced OSS risk, Malicious Package, license analysis and exploitable path. | Advanced reachability engine, but with added noise. |
| Container & API Security | ✓ WIN Native support for container scanning and API security without need for external tools. | Limited support. Lacks Docker file support and registry integration. |
| Artificial Intelligence Capabilities | AI-powered Developer Assist for real-time remediation in IDEs and deep vulnerability coverage. Capabilities cover multiple security domains including malicious packages and IaC, in a single platform, ensuring consistency and scale. | AppSec agents with few in beta only. |
| IaC Security | ✓ WIN Full native scanning capabilities. | No dedicated IaC solution. |
| Reporting & Dashboards | ✓ WIN Unified results, detailed reporting, engineering overview dashboard, | Limited capabilities. |
| Pricing | Predictable ROI with tiers and levels that scale with your business. | Licensed per contributing developer. |
| Industry recognition | ✓ WIN Recognized Leader in Gartner, Forrester, IDC, and GigaOm for innovation in AI-driven, code-to-cloud security. | Lack industry recognition for AppSec. |
| Enterprise Readiness | ✓ WIN Built for scale with ASPM, policy management, and multi-team orchestration. | Best suited for teams focused on SCA only. |
Truly Secure Code at the Speed of AI Development
See how Checkmarx One stacks up in an obejctive custom comparison for Your use-case!
From comprehensive enterprise scanning to AI-powered remediation in the IDE, Checkmarx One keeps security in step with how modern teams build.


Why Checkmarx Is the Top Alternative to Endor Labs
Checkmarx delivers accuracy, breadth, and AI-native security at every layer, protecting human and AI-generated code with enterprise-grade integrations and a full AppSec suite that scales with evolving threats.
Enterprise Agentic Appsec Platform
Endor Labs focuses on SCA and AI governance, leaving gaps in broader AppSec coverage like limited language support and missing integrations. Checkmarx One fills those gaps with a complete AppSec suite that adapts to evolving cyber threats, provides real-time visibility into posture and remediation progress, and enables teams to scan, prioritize, and fix critical vulnerabilities from repo to runtime, all within one unified software supply chain security platform built to scale without slowing you down.
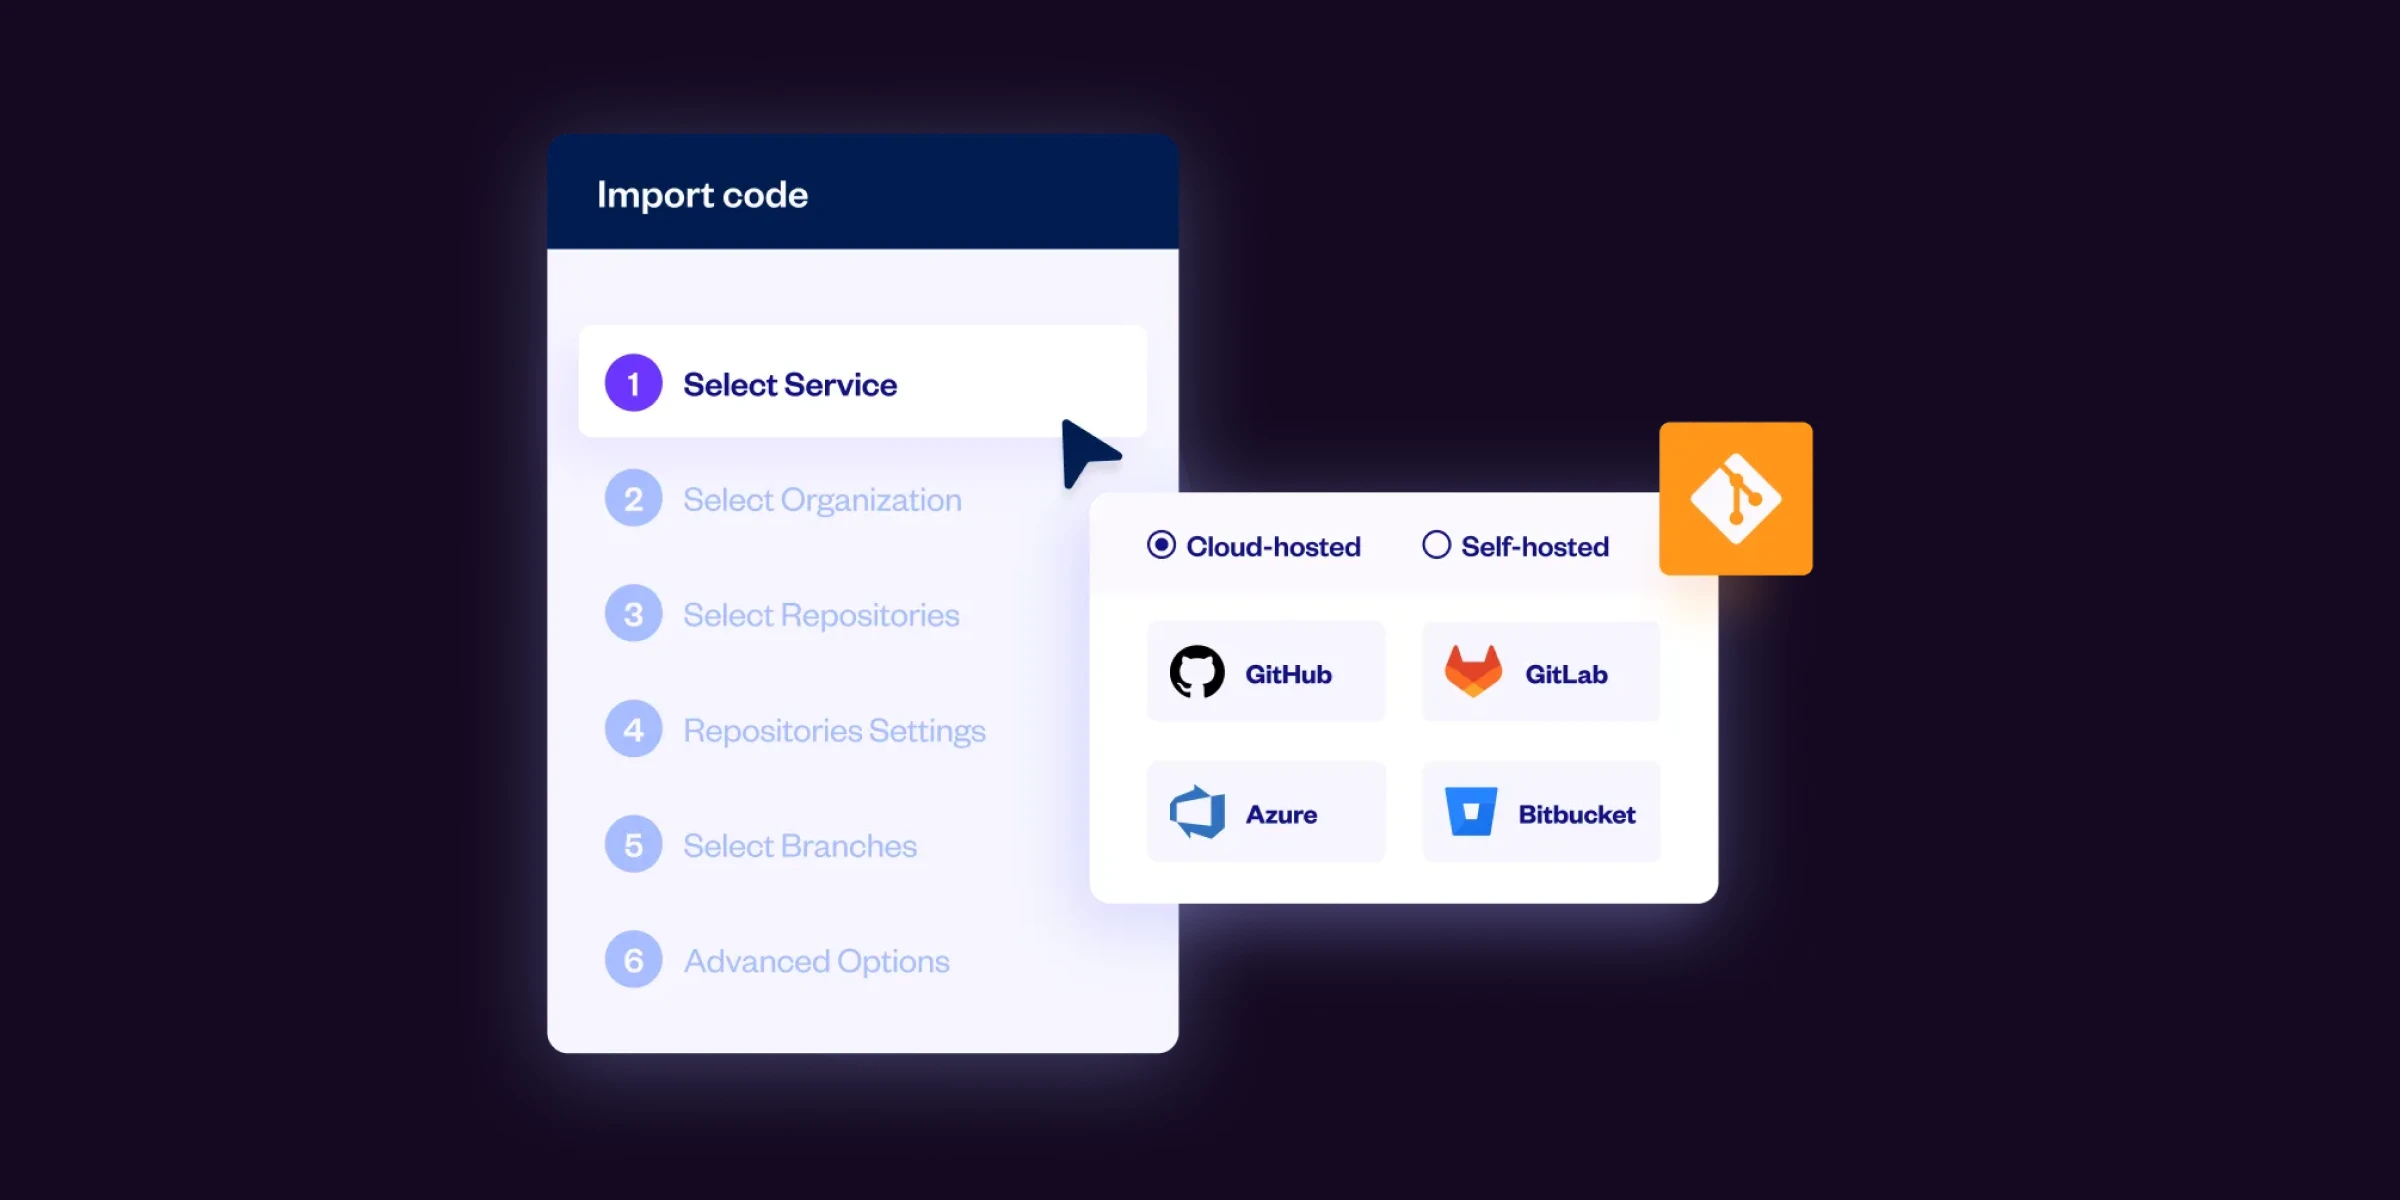
Widest Native Framework Coverage & Integrations
Endor Labs limits CI/CD dependency checks to GitHub Actions, creating blind spots across other pipelines. Checkmarx eliminates those gaps in software supply chain security with native integrations for GitHub, Azure DevOps, Jenkins, Bitbucket, and more. Multi-cloud orchestration ensures flexibility and scale for even the most complex enterprise environments.
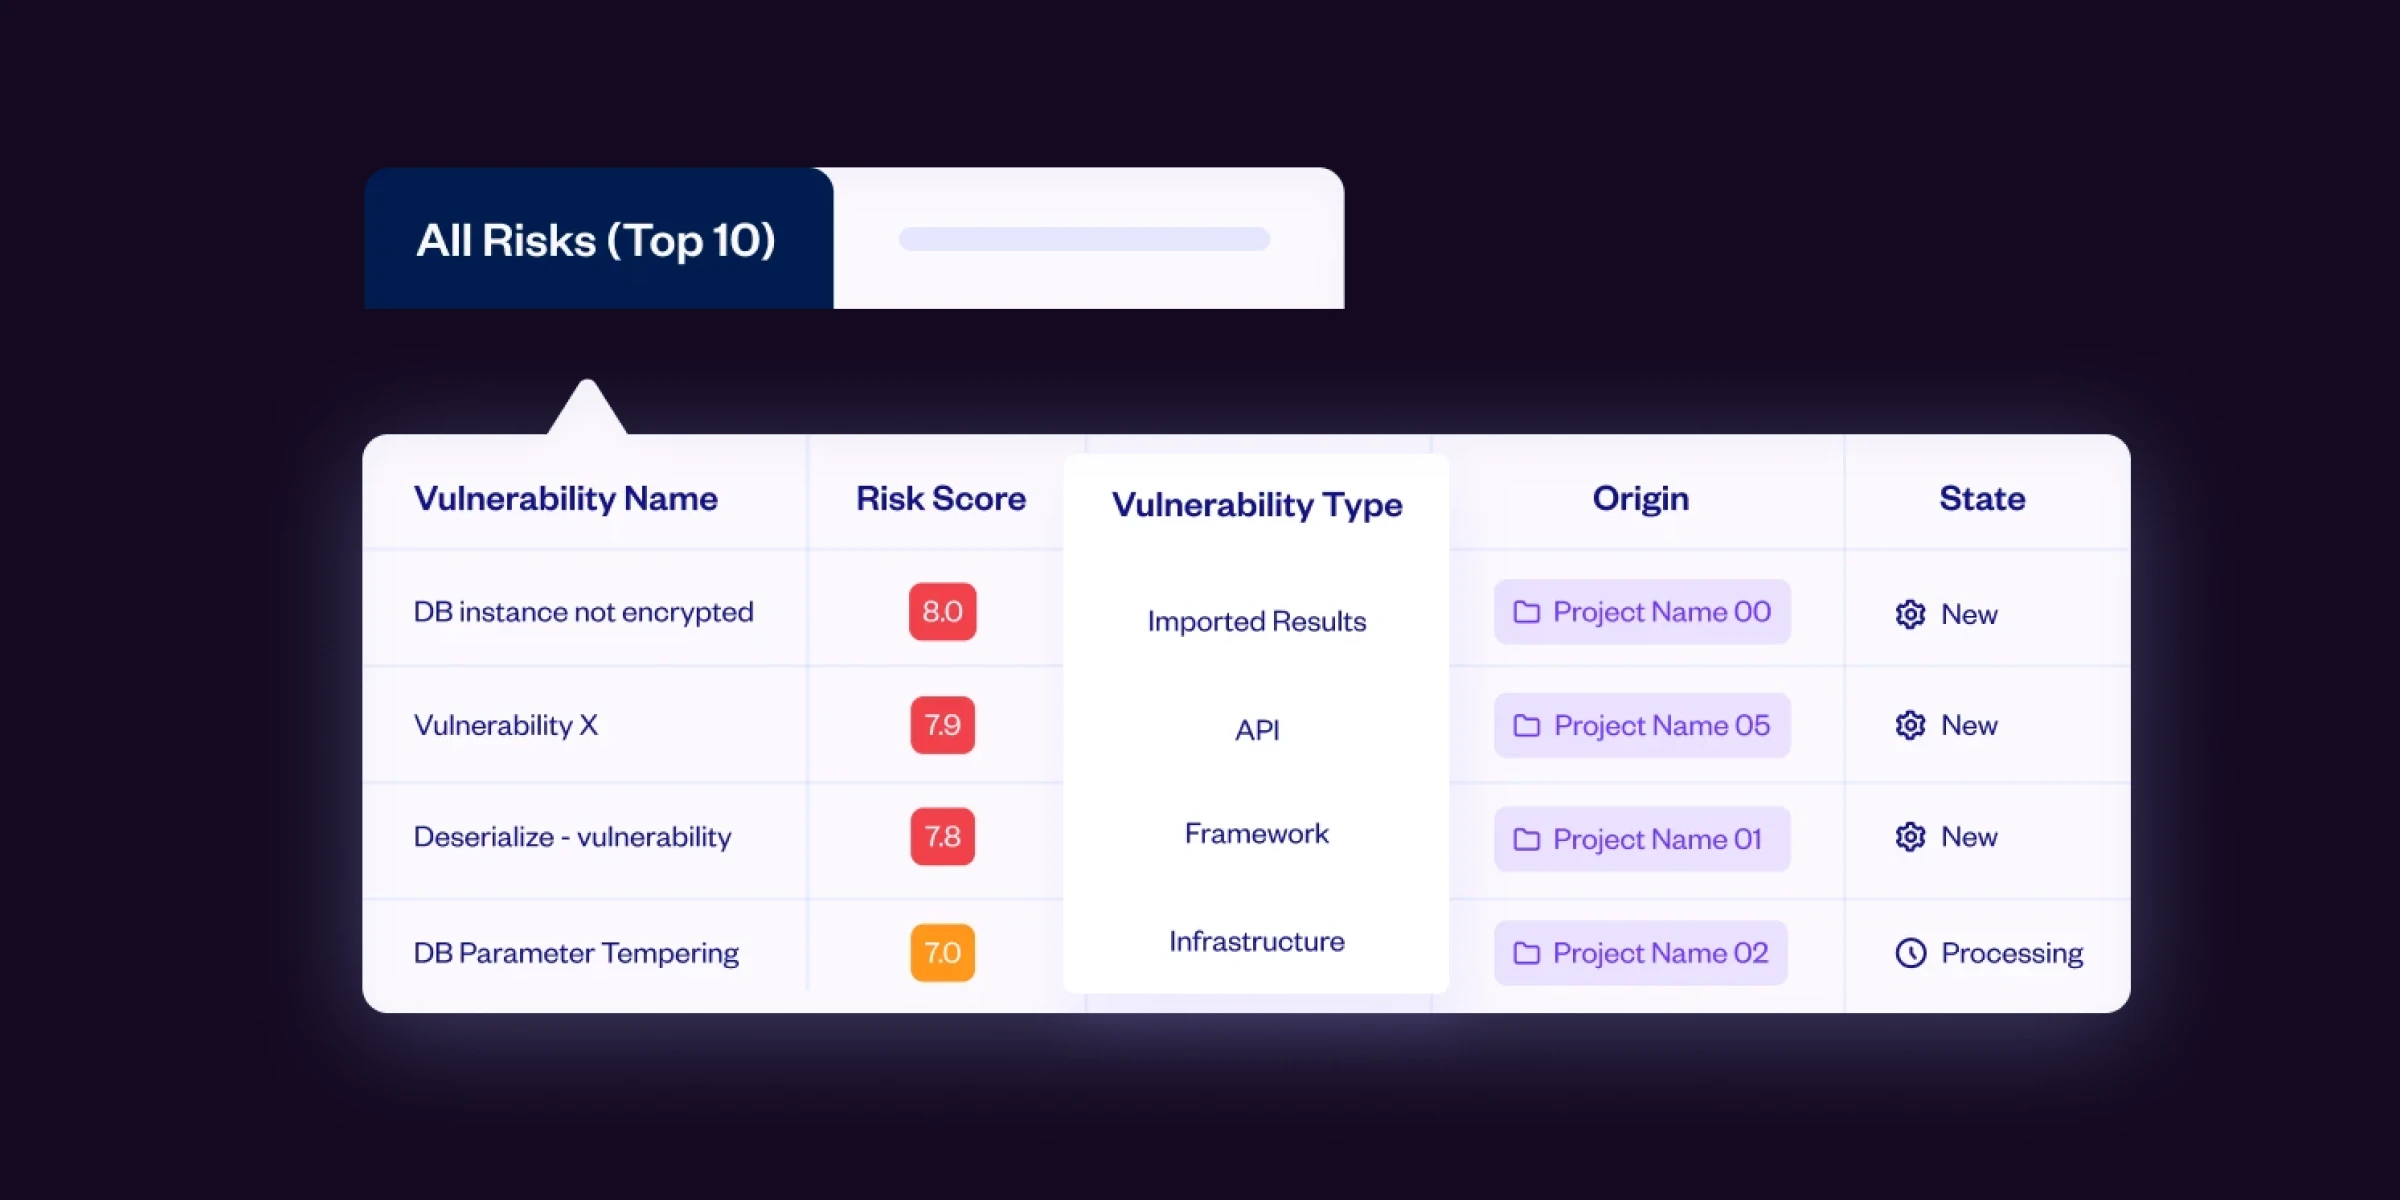
Endor Labs lacks visibility into application security posture. Checkmarx delivers native ASPM, reporting, and analytics, prioritizing real security vulnerabilities with context-aware scanning that considers business impact, runtime exposure, and asset criticality. By eliminating up to 90% of unnecessary threat detection alerts, your security team stays focused, responds faster, and avoids burnout, all with a single, centralized view of AppSec risk.
Why the World’s Top Teams Choose Checkmarx
“We’ve seen an 80% noise reduction — our engineers now focus on the high-quality risks that matter.”Explore Best Buy Case Study
“By far the best AppSec tooling decision we have made”
“Checkmarx gave us a 90% reduction in vulnerabilities in just a few months.”
“Unifying our AppSec tools with Checkmarx gave us a single source of truth.”
“With 2.1B lines of code scanned monthly, Checkmarx gives us the scale and speed we need.”
“Checkmarx fits seamlessly into our DevOps pipelines—it’s a truly scalable solution.”
“From a buyer perspective, Checkmarx’s approach offers a structured and role-aware entry point into agentic security. ”
“Incorporating Checkmarx’s technology has revolutionized our development culture ”
“Checkmarx One made our security team and developers life easier.”
“The success of our AppSec program can be directly attributed to the tooling, processes and support provided by the Checkmarx managed services.”
“Bringing ASPM context directly into the IDE reflects a forward-looking approach to prioritizing security efforts based on risk earlier in the development process.”
See it in action
See why Checkmarx is Better
Speak to an expert to explore how Checkmarx meets your critical application security needs.
Thank You!
Your Custom Demo Request is successfully sent.
A member of Checkmarx Team would contact you shortly to set up your custom demo.
Personalized Demo
See Where Checkmarx Wins
One platform, zero blind spots
AST, SCA, IaC, API, Container, Supply Chain unified
Accuracy beyond reachability
Exploitable path across the full app, not just OSS
Every pipeline, not just GitHub
Works across all major SCMs and CI/CDs
Enterprise-ready ASPM
Policy, governance, audit trail, third-party scan ingestion
Move beyond a bundle of acquired products
See how Checkmarx delivers faster feedback, broader coverage, and a developer experience that actually drives adoption – without the two-pipeline overhead.