
Why Devs Switch to Snyk
Alternatives and Competitors
Snyk built a strong developer tool. Checkmarx built the platform enterprises run on, correlating every scanner, governing every AI agent, and closing the loop from the first line of code to production, at a scale Snyk’s developer-first architecture wasn’t built to reach.
Enterprise-Grade Application Security,
Without the Trade-Offs
From false positives to a missing AI governance layer, Snyk’s approach leaves real gaps for enterprise teams. Checkmarx closes them with agentic prevention, unified AI Supply Chain Security, and hybrid AI scanning built for the way code gets written today.

Real-Time Prevention, Not Post-Commit Scanning
Snyk scans mostly after a commit, producing high false positives and reports that can take hours to build. Developer Assist secures code the moment it’s written — instant inline detection, explainability, and confidence scoring, natively inside the IDE.

The AI Governance Layer Snyk Doesn't Have
Snyk governs coding agents from the outside looking in. Checkmarx AI Supply Chain Security unifies deterministic discovery of every AI asset touching your codebase, not AI self-reporting, and lets you export it into an AI-BOM for regulatory needs.

7x More Exploitable Path Vulnerabilities
Checkmarx SAST + SCA identify approximately 7x more exploitable path vulnerabilities than Snyk, and surface them an estimated 73% earlier than Snyk’s post-build pipeline, enabling teams to find vulnerabilities that Snyk misses.

Triage & Remediation, Built Into the PR
Snyk’s Agent Fix works inside the developer’s workflow only. Checkmarx adds a second layer: Triage Assist and Remediation Assist automatically triage findings for reachability and exploitability and generate merge-ready fix pull requests directly in GitHub.

Built for Enterprise Scale
Checkmarx was engineered for organizations that scale, with unified governance and intelligence, in one platform, without needing to rely on addition tools to gain full AppSec coverage

The Highest-Fidelity Scanning in the Market
Snyk Code, powered by DeepCode AI, runs a single AI model against your code. Checkmarx Fusion fuses deterministic and AI-based scanning into one adaptive engine, so you get AI’s reach without giving up the deterministic accuracy security teams have to trust.
The highest-fidelity scanning architecture available
Checkmarx Fusion delivers the highest fidelity and broadest coverage in enterprise AI scanning, combining deterministic rules-based engines with AI-augmented analysis to deliver the highest F1 score in the industry, three times the query-based baseline.
Why Checkmarx is Better than Snyk
Checkmarx One embeds AppSec directly into how engineering teams build today with a single correlated platform with explainable AI remediation, not a point tool bolted onto the pipeline. It extends coverage into the languages, runtime behavior, and AI-native tooling Snyk’s platform doesn’t reach.
The Broadest Language and Framework Coverage
Checkmarx leads coverage across all languages and 80+ frameworks, including legacy stacks like COBOL, RPG, and PL/SQL that Snyk’s engine doesn’t cover, plus every major IDE.

From Exploit to Exact Source Location
Native DAST maps runtime findings back to their source code location, turning “we found a vulnerability” into “here’s where to fix it.” Snyk has no native DAST engine, only delivered through a separate partner product.

Native MCP Server Built for Agentic Coding
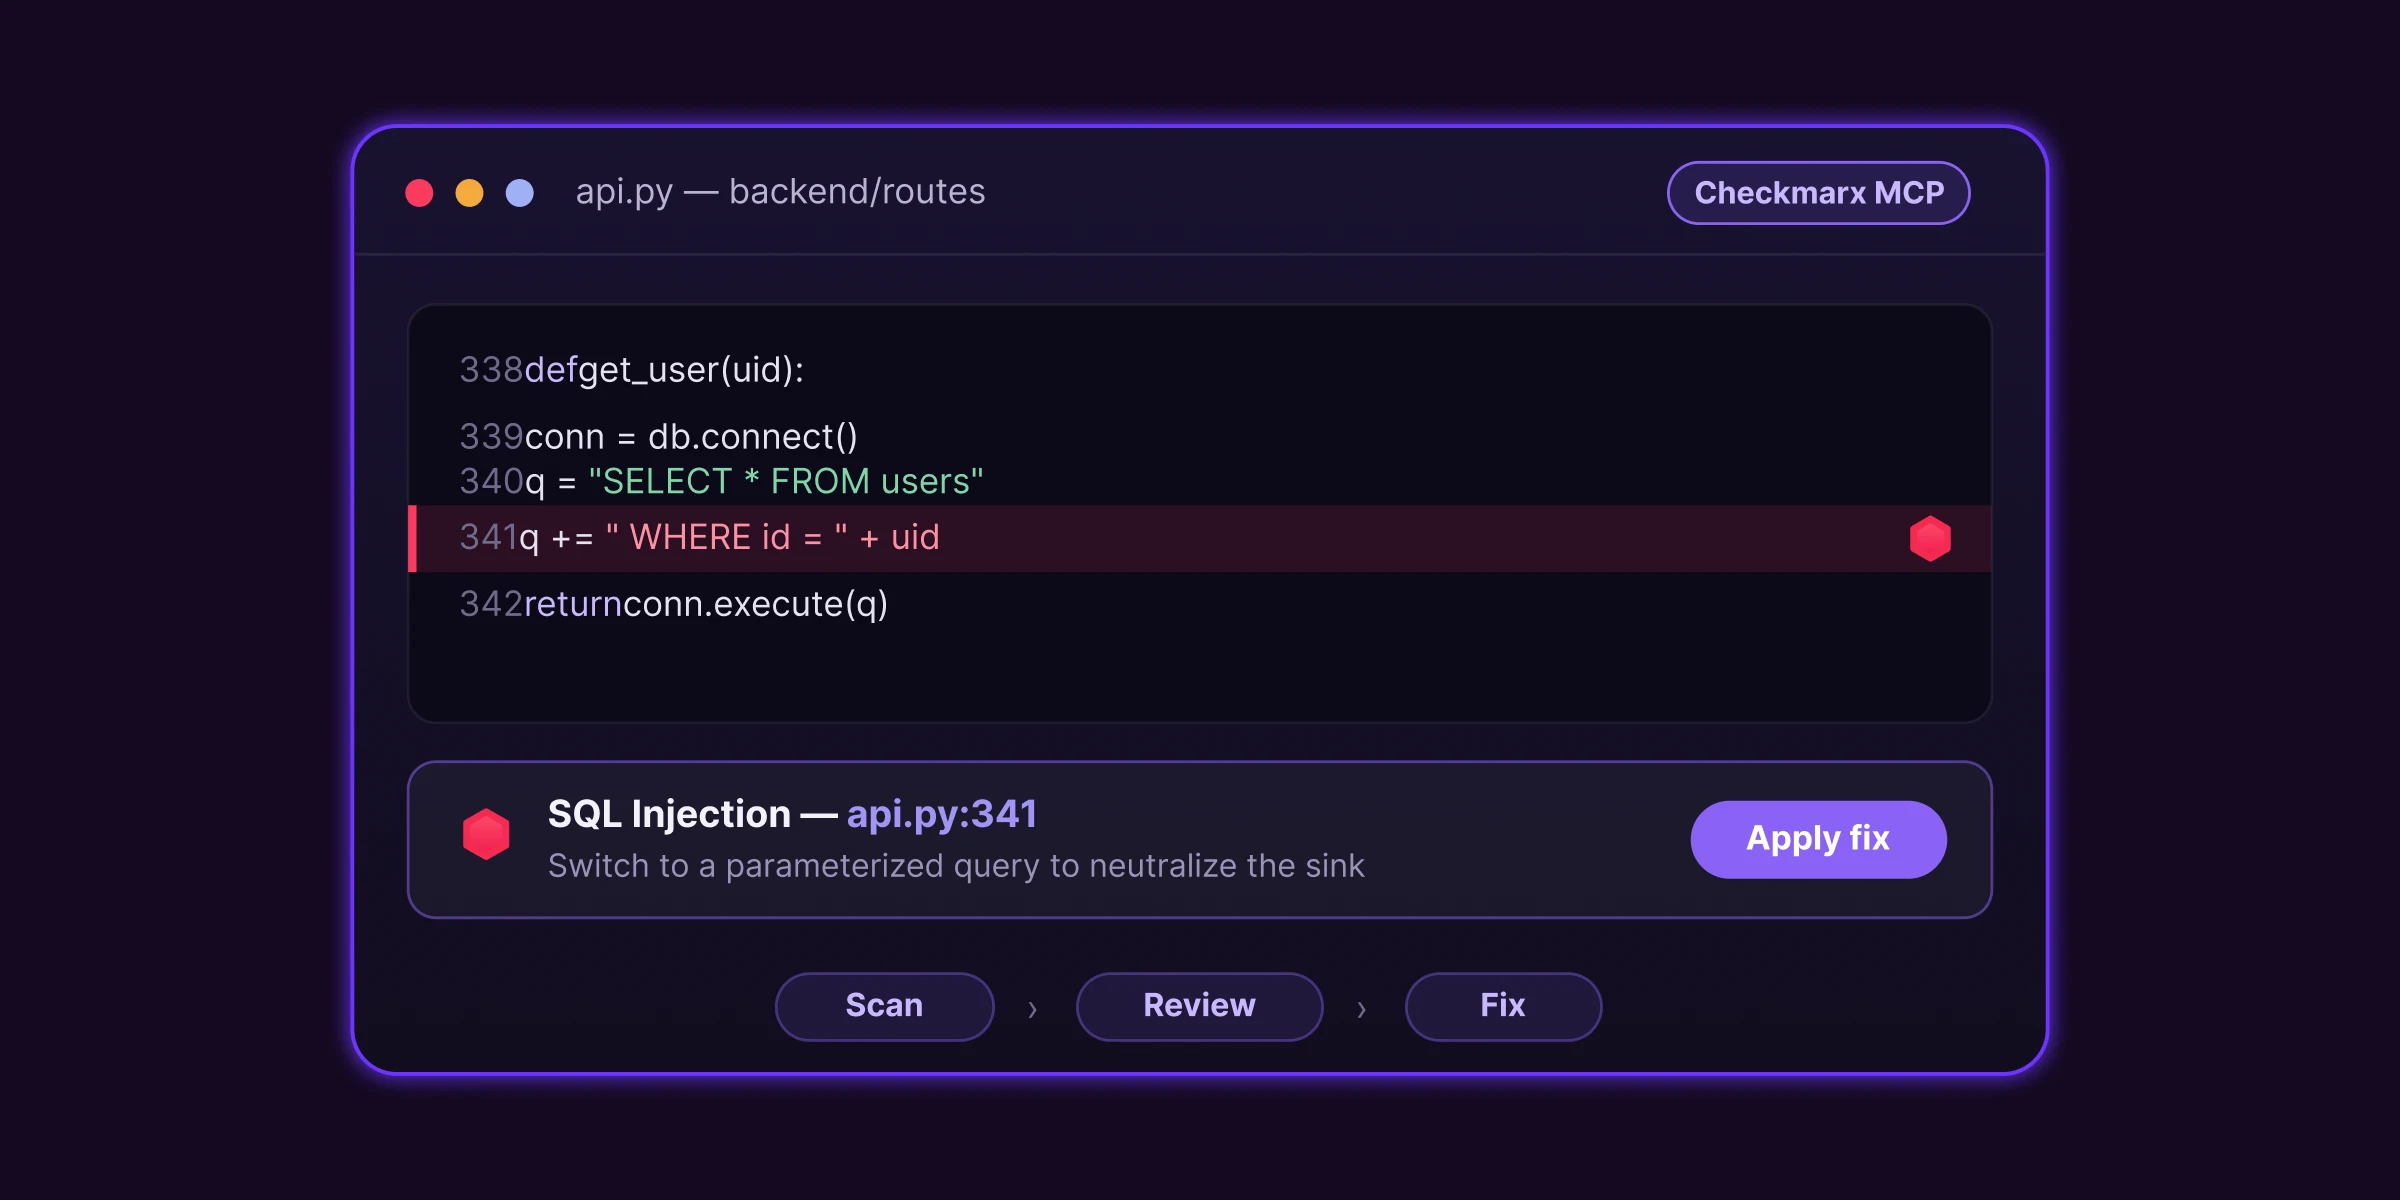
Checkmarx works natively inside Claude, ChatGPT, Cursor, Windsurf, and VS Code, and auto-selects the right scan engines for what’s in the repo, with enterprise SSO and RBAC. Snyk’s MCP server is scoped to SCA and developer-triggered SAST scans, without engine auto-selection.
Developer Adoption at Scale
Snyk relies on CLI and repo scans. Checkmarx integrates direct to IDE, working seamlessly with Cursor, Copilot, Windsurf and more. Snyk reports take hours to build and lack IDE context, while Checkmarx provides inline explainability, confidence scoring, and more.

Compare Snyk vs Checkmarx One
| Capability | CHECKMARX ONE | Snyk |
|---|---|---|
| Platform | Unified multi-engine platform — SAST, SCA, SCS, DAST, API Security, IaC in a single UI with correlated results and ASPM | SCA and SAST (Snyk Code) at the core, expanding with Snyk Studio and AppRisk; DAST and ASPM depth still lean on partners or newer, less mature modules. |
| SAST | ✓ WIN Incremental scanning; tailored presets; supports all languages; 2x true positives in benchmarks. AI-powered SAST with Attackability scoring cuts noise and prioritizes real risk. | Handles standard use cases, but cannot perform incremental scanning; high false negative rates for Java, Apex & C#; limited custom query capability; only 1 scan per developer. |
| AI Remediation | ✓ WIN Triage Assist + Remediation Assist auto-triage PR findings for reachability and exploitability, generating merge-ready fix pull requests in GitHub with a full audit trail. | Agent Fix delivers AI-generated, merge-ready fixes in the developer's workflow, paired with reachability-based prioritization. |
| AI Governance | ✓ WIN Deterministic discovery of AI assets, not AI self-reporting. Native MCP Server auto-selects scan engines for what's in the repo, with full SSO and RBAC. AI-BOM generation. | Evo provides AI agent guardrails and component inventory. Snyk also offers an MCP server, focused on SCA and developer-triggered scans, without engine auto-selection or enterprise RBAC. |
| SCA | ✓ WIN Unified scanning with webhooks; aggregated dependency results; 7x more exploitable path vulnerabilities found | Exploitable Path analysis is limited to Java/JS with GitHub integration. |
| Supply Chain Security | ✓ WIN Checkmarx Zero proactively identifies and blocks malicious packages before public disclosure — over 550,000 malicious packages catalogued to date, using behavioral detonation-chamber analysis. | Snyk Advisor flags packages as unmaintained; it does not perform behavioral malicious-code detection. |
| DAST | ✓ WIN Native DAST engine with CI/CD automation and API testing | No organic DAST solution — only available through third-party partners |
| API Security | ✓ WIN Complete API inventory, risk detection | Not offered as a standalone native capability — positioned as a combination of existing tools. |
| IaC Security | ✓ WIN Native IaC engine (KICS) covering Terraform, CloudFormation, and Kubernetes, correlated with SAST findings in one results view. | Supports fewer frameworks, with findings siloed from application-code results. |
| Container Security | ✓ WIN Container image scanning through SCA, with CVSS scoring, attack-vector, and CIA-impact data. | Fast image scanning with runtime monitoring capabilities. |
| Developer Experience | In-IDE guidance and real-time, AI-validated fixes in VS Code, Cursor & Windsurf. | Good IDE experience — but developers still stop to evaluate, defer, or accept risk. |
| Language Coverage | ✓ WIN 35+ core languages, with NG SAST extending coverage to modern and AI-generated code (PowerShell, Solidity, GraphQL, and more) — including COBOL, RPG, Dart, Groovy, Lua, Perl, PL/SQL, Objective-C, VB6, and ASP. | Roughly 20 languages; no support for COBOL, RPG, Dart, Lua, Perl, or PL/SQL. |
| Deployment | ✓ WIN Enterprise-grade reporting, policy management, audit trails, and a multi-year Gartner Magic Quadrant Leader track record. | Enterprises report added effort scaling governance and policy consistency across large, complex environments. |
*Engagement scope, deliverables, and pricing are defined in your statement of work.
Access without the overhead: Through this engagement, your code is scanned with Checkmarx Fusion without your team having to procure, configure, or manage it. Our experts select the right frontier model for each scan, weighing complexity against cost, so you get the depth of advanced scanning within a defined scope.
Why the World’s Top Teams Choose Checkmarx

“We’ve seen an 80% noise reduction — our engineers now focus on the high-quality risks that matter.”Explore Best Buy Case Study
“By far the best AppSec tooling decision we have made”
“Checkmarx gave us a 90% reduction in vulnerabilities in just a few months.”
“Unifying our AppSec tools with Checkmarx gave us a single source of truth.”
“With 2.1B lines of code scanned monthly, Checkmarx gives us the scale and speed we need.”
“Checkmarx fits seamlessly into our DevOps pipelines—it’s a truly scalable solution.”

“From a buyer perspective, Checkmarx’s approach offers a structured and role-aware entry point into agentic security. ”
“Incorporating Checkmarx’s technology has revolutionized our development culture ”
“Checkmarx One made our security team and developers life easier.”
“The success of our AppSec program can be directly attributed to the tooling, processes and support provided by the Checkmarx managed services.”

“Bringing ASPM context directly into the IDE reflects a forward-looking approach to prioritizing security efforts based on risk earlier in the development process.”
Discover why Checkmarx One stands out from the rest
Speak to an expert to explore how Checkmarx meets your critical application security needs.
Thank You!
Your Custom Demo Request is successfully sent.
A member of Checkmarx Team would contact you shortly to set up your custom demo.
The Bottom Line
Where Checkmarx wins
7x more exploitable vulnerabilities
found by Checkmarx SAST + SCA vs. Snyk reachability
15+ more languages
including COBOL, RPG, Dart, Groovy, Perl, and PL/SQL
Industry-leading malicious package detection
Snyk only identifies if a package is unmaintained
Designed for complex enterprises
Snyk “probably works great for a small shop” (real customer quote)
See the difference for yourself
Let us show you how Checkmarx finds 7x more exploitable vulnerabilities in your actual codebase — with a live comparison using your own projects.


