
Choose Checkmarx Over Veracode
Checkmarx One is the unified, agentic AppSec platform, built for developers, AppSec leaders, and CISOs, with autonomous triage, remediation, and AI-validated scanning that Veracode doesn’t match. See why teams are making the switch.
Legacy Solutions Don’t Build DevSecTrust
Veracode has historically focused on the needs of security teams — not developers. Checkmarx One has a unified experience and doesn’t get in the way of developers’ workflows.

Faster Risk Mitigation
Veracode needs two separate builds, only scans compiled binaries, and often can’t point to the exact vulnerable line. Checkmarx scans source directly, no compile step, faster feedback, and one fix that remediates every instance of the pattern across your codebase.

Seamless Integrations
Veracode ships SAST and SCA as separate plugins, making integrating into your workflows a challenge. Checkmarx integrates natively across IDEs, SCMs, CI/CD, feedback tools, pipelines, and AI coding assistants, including Cursor, Windsurf, GitHub Copilot, and Claude Code.

A Truly, Unified Platform
Veracode still connects SAST and SCA through APIs to SCM tooling, leading to fragmented results. With Checkmarx, a single event can trigger multiple scans, delivering high-fidelity results teams can act on with confidence with a shared view of application risk.
The highest-fidelity scanning architecture available
Checkmarx Fusion delivers the highest fidelity and broadest coverage in enterprise AI scanning, combining deterministic rules-based engines with AI-augmented analysis to deliver the highest F1 score in the industry, three times the query-based baseline.
Why Checkmarx is better than Veracode
Checkmarx gets teams to their first scan fast, keeps false positives low, and gives developers a security experience they want to use. Here’s where that shows up against Veracode.
Find More Vulnerabilities
A large FinTech migrated from Veracode SAST and SCA to Checkmarx. In under six months, Checkmarx rescanned nearly half the applications in their portfolio and surfaced over 12,000 critical vulnerabilities Veracode had missed.

Unified AppSec Risk Coverage
Veracode scans compiled binaries only, has no native SCM integration, and its coverage thins out in IaC, supply chain, and DAST. Checkmarx One ASPM’s intelligent risk view unifies signals, cuts noise, and prioritizes what’s exploitable for smarter risk management across the full pipeline, from source to runtime.

Fewer false positives, proven
Veracode claims the lowest out-of-the-box false-positive rate but doesn’t publish how it’s measured. Checkmarx does. Our NG SAST runs a deterministic engine and an AI engine concurrently, then validates every finding through a Findings Analysis Engine before a developer sees it — 60% fewer false positives, 70% better fidelity than traditional SAST, with a published F1 score of 0.64 against an industry average near 0.20.

Built for developer trust
Security that fights developers loses. Checkmarx meets developers in their existing tools, prioritizes what matters, and gives AppSec teams what they need to build a program developers use.
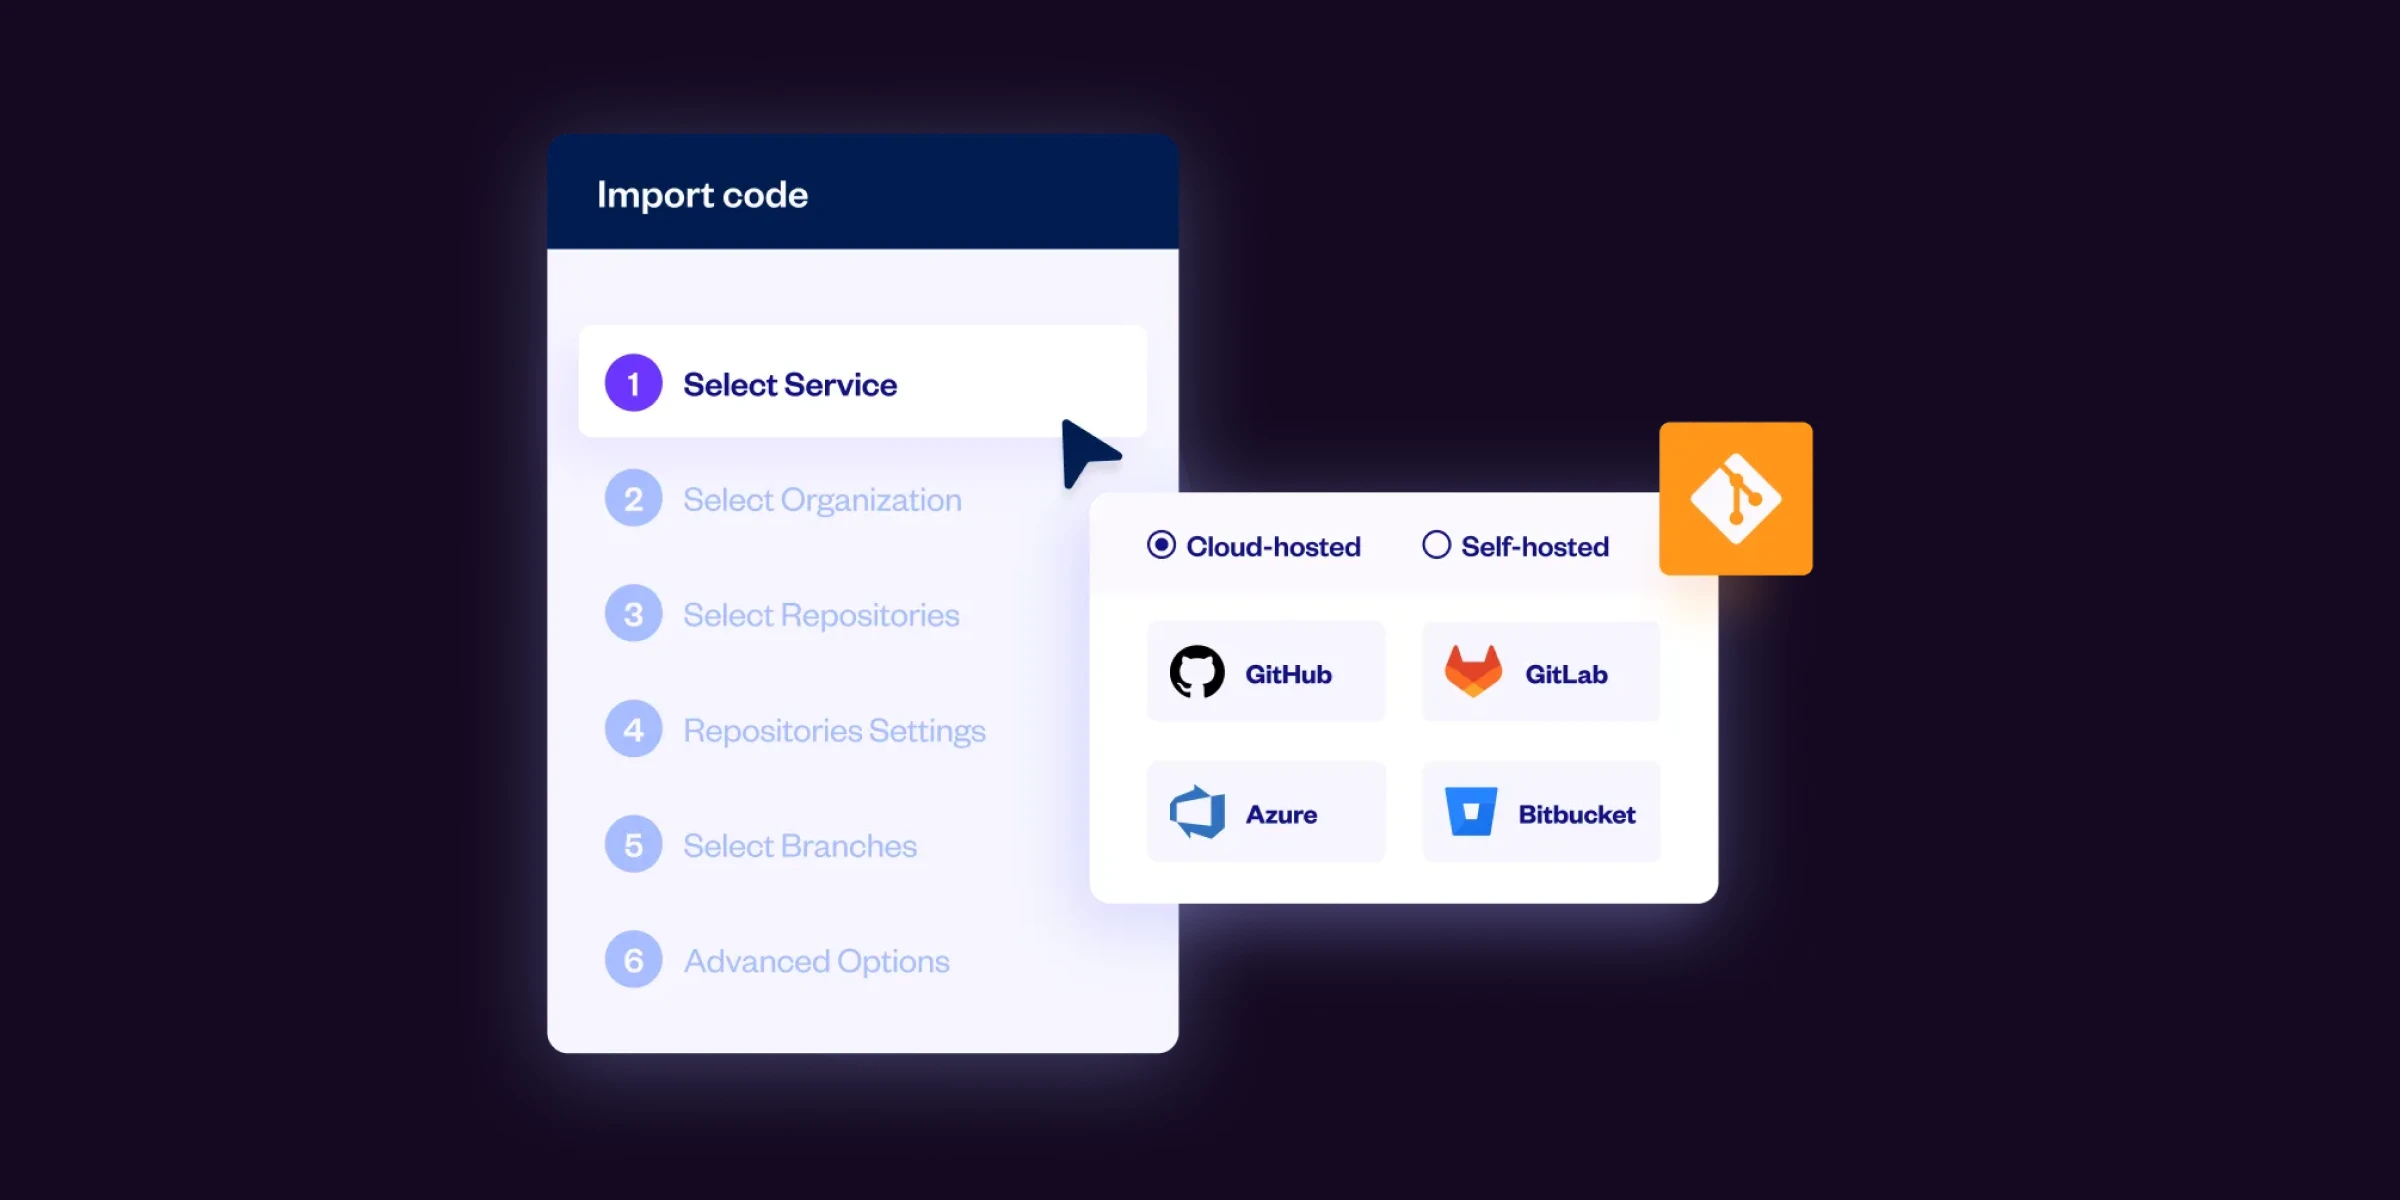
From finding to fix, faster
Veracode’s Fix suggests patches, but there’s no step in between to tell you which findings are worth fixing first. Checkmarx closes that gap: Triage Assist analyzes every pull request for real exploitability the moment it’s opened, and Remediation Assist turns confirmed findings into a merge-ready fix PR, all in one continuous loop, without a developer ever leaving their workflow.

See how Veracode compares to Checkmarx
| Capability | Checkmarx One | Veracode |
|---|---|---|
| Platform | ✓ WIN One unified platform with real-time scanning direct from source; a single event can trigger multiple engines, results in one view. | Customers say UI is “clunky” and UX feels disjointed; Veracode has separate plugins for SCA and SAST, making integration a challenge; No real-time scanning. |
| SAST | ✓ WIN Hybrid scanning approach with highest-fidelity in industry, covering all languages. 60% fewer false positives, 70% improved fidelity vs. traditional SAST. | Static Analysis remains binary-based; AI is layered on through Veracode Fix rather than a concurrent multi-engine detection core. |
| AI Remediation | ✓ WIN Triage Assist auto-analyzes PR findings for real exploitability (Attackability) and tags Confirmed / Not Exploitable; Remediation Assist generates a merge-ready fix PR on request. | Veracode Fix generates AI-suggested patches, with no equivalent PR-level exploitability triage distinguishing real risk from noise before remediation. |
| AI Supply Chain Security | ✓ WIN AI-BOM generation. LLM Scanning capabilities. Mapped to regulatory requirements. | No equivalent — no MCP security, no AI-BOM, no agent inventory. |
| SCA | ✓ WIN Malicious package detection – 500K+ malicious packages identified to date; AI-generated-code scanning | Limited malicious package detection; No AI-generated code scanning. |
| Exploitable Path | ✓ WIN Exploitable Path analysis – reduces noise by 70% | No Exploitable Path |
| ASPM | ✓ WIN Native ASPM solution correlating Checkmarx and third-party signals. Named a Leader in the IDC MarketScape for ASPM. | Risk Manager offers limited unified visibility. No ASPM solution. |
| Query Customization | AI Query Builder for custom CxQL — write or modify detection queries with AI assistance. | No custom query capability. |
| Integrations | ✓ WIN Frictionless IDE, SCM, and CI/CD integrations — a single event can trigger multiple scans. | Separate plugins for SCA and SAST; API-based SCM connections. |
Why the World’s Top Teams Choose Checkmarx

“We’ve seen an 80% noise reduction — our engineers now focus on the high-quality risks that matter.”Explore Best Buy Case Study
“By far the best AppSec tooling decision we have made”
“Checkmarx gave us a 90% reduction in vulnerabilities in just a few months.”
“Unifying our AppSec tools with Checkmarx gave us a single source of truth.”
“With 2.1B lines of code scanned monthly, Checkmarx gives us the scale and speed we need.”
“Checkmarx fits seamlessly into our DevOps pipelines—it’s a truly scalable solution.”

“From a buyer perspective, Checkmarx’s approach offers a structured and role-aware entry point into agentic security. ”
“Incorporating Checkmarx’s technology has revolutionized our development culture ”
“Checkmarx One made our security team and developers life easier.”
“The success of our AppSec program can be directly attributed to the tooling, processes and support provided by the Checkmarx managed services.”

“Bringing ASPM context directly into the IDE reflects a forward-looking approach to prioritizing security efforts based on risk earlier in the development process.”
Discover why Checkmarx One stands out from the rest
Speak to an expert to explore how Checkmarx meets your critical application security needs.
Thank You!
Your Custom Checkmarx Demo Request was Successfully Sent!
The Bottom Line
Where Checkmarx wins
No binary compilation required
source code scanning eliminates the need for two build pipelines
Seamless IDE, SCM, and CI/CD integrations
vs. Veracode’s separate plugins and integration challenges
Native IaC, container, and supply chain security
areas Veracode doesn’t natively cover
Faster scanning feedback
source code scanning avoids cloud processing delays and compilation failures
Move beyond binary scanning
See how Checkmarx delivers faster feedback, broader coverage, and a developer experience that actually drives adoption — without the two-pipeline overhead.


