Checkmarx Fusion SAST:
Find More Real Vulnerabilities
AI-generated code ships in more languages than most SAST tools support. Checkmarx Fusion SAST pairs proven analysis with frontier-model reasoning to find what either misses alone, at predictable cost.
More Signal. Less Noise.
A SAST Tool Built to Find Everything That Matters.
Different methods catch different risks. Checkmarx brings complementary strengths together in one fused SAST experience.
From source code scanning to remediation, Checkmarx Fusion SAST gives enterprise teams the accuracy, coverage, and AI-powered intelligence to secure code without slowing down delivery.
High Fidelity SAST Tool
A deterministic engine for core languages, plus LLM-based scanning with Fusion SAST for emerging languages and frameworks that rules alone don’t cover. If LLMs can code it, we can scan it.
Try Scanning in a Demo
Several curated frontier models reason about your code, each approaching it differently, to surface vulnerabilities with no known rule and no prior CVE. Choose the depth and cost you need.
Try Checkmarx Fusion SAST in a Demo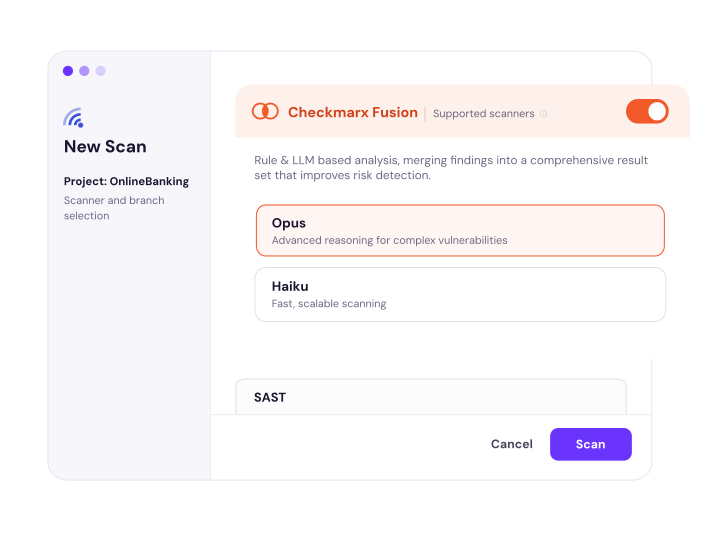
Fusion findings flow directly in Checkmarx One, where Risk Orchestration adds application, risk, policy, and ownership context. Triage Assist helps determine what needs action using reachability and exploitability, while Remediation Assist generates review-ready fixes for developers.
See AI-powered Triage & Remediation in Action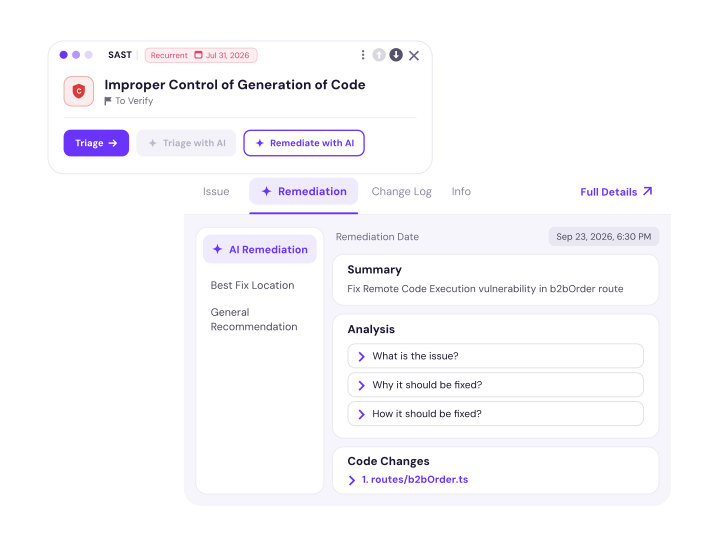
Full SAST scans for deep analysis, incremental scans for PR-level speed. Fusion is on by default in the Checkmarx SAST scanner. Run frontier-model reasoning when Credits are available, or turn it off and continue as before.
Try Code Scanning in a Demo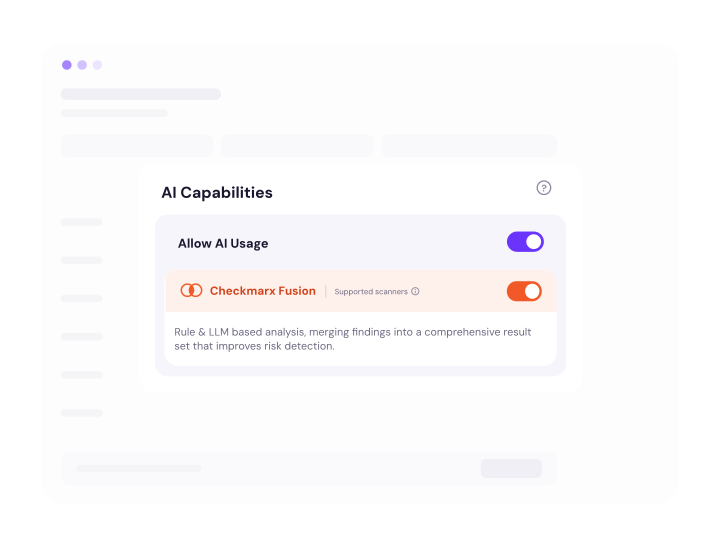
Scan source code directly from GitHub, GitLab, Azure, and Bitbucket with no compilation needed. Fusion SAST runs in the workflow your team already uses, so deeper analysis never means a second scanner to deploy.
See Multiple Results in One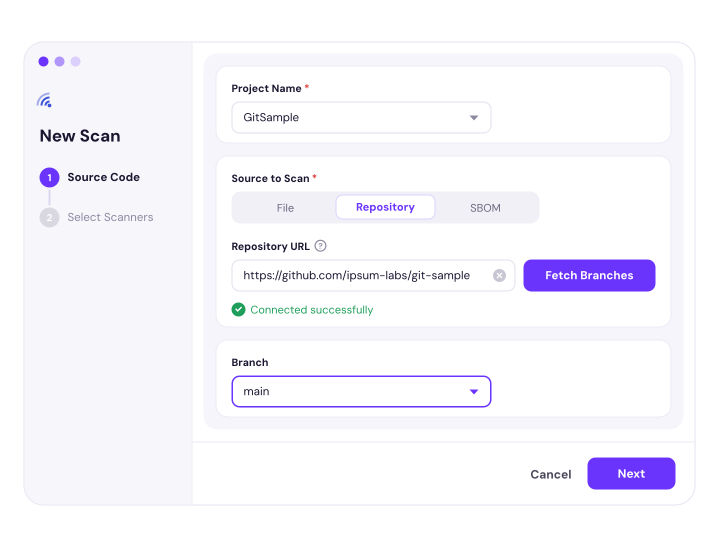
With AI generating unprecedented amounts of code, security has to be an enabler, not a bottleneck. This hybrid approach combining rules-based precision with AI-powered reasoning gives AppSec teams a way to scale while delivering high fidelity performance. The industry finally has an approach built for what AI demands.
Checkmarx Fusion SAST is part of the
Claude Marketplace
Checkmarx is a proud member
of the Cyber Verification Program
Proven Analysis. Frontier Reasoning.
One Higher-Fidelity Result.
Fusion SAST combines Checkmarx's established application security analysis with curated frontier reasoning from Anthropic via Amazon Bedrock. Findings Analysis reconciles the results into a single, higher-fidelity view of application risk.
Established application security analysis
Checkmarx Fusion SAST
- Rules and program analysis
- AI-based analysis where applicable
- Supported Anthropic models via Amazon Bedrock
- Reasoning across complex code and logic
- Additional discovery beyond established patterns
Selected model • lines of code scanned
Findings Analysis / Reconcilation
- Classify
- Reconcile
- Deduplicate
- Reduce noise
Predetermined Credit rates.
Economics you can forecast.
Checkmarx Fusion is a compelling example of what becomes possible when organizations bring frontier AI intelligence to bear within the kind of deep security context Checkmarx has spent decades building.
Every Language. Every Vulnerability. One Fusion SAST Scanner.
- Any language. Highest-fidelity findings. Zero compromises.
- Fusion SAST catches what AI-only tools miss and what rules-based tools can’t reach.
- One result set. Your existing workflow. Nothing new to learn.
Enterprise SAST Tool Built for the AI-DLC
AI is changing how code gets written and how vulnerabilities are found and fixed. Checkmarx Fusion SAST is built for that shift, combining high-fidelity analysis, broad coverage, and intelligent remediation across the AI-DLC.
AI-generated code ships faster than scanners can follow

Coverage Without Tradeoffs
AI-only scanners can return different results on each scan and miss new languages. Checkmarx delivers consistent results on every scan, across every language, without trading accuracy for breadth.
AI Scaled Your Code Faster Than You Can Keep Up
Close Security Gaps
AI generates code faster than security teams can scale. 81% of organizations already knowingly ship vulnerable code. Every gap is a finding that slips through. Checkmarx closes it, across every language, at every stage of the pipeline.
Noise kills adoption. False positives kill trust in your SAST results
Cut the Noise
Findings Analysis cuts false positives by 60%, automatically, classifying SAST scan results before they reach your team so the findings that matter get fixed.
Vulnerabilities found too late cost more to fix
Fix Where Developers Work
Checkmarx surfaces findings in IDEs, PR checks, and pipelines with fix guidance developers can act on earlier. Security stays inside the development flow, reducing rework and late-stage cost.
No one approach finds everything
End the tradeoff between proven analysis and frontier reasoning
Checkmarx Fusion SAST adds frontier-model reasoning on top of the proven hybrid engine, then reconciles every finding into one result your team can investigate and act on.
Find Source Code Vulnerabilities
Rules or AI Alone Miss
Checkmarx Fusion adds curated frontier AI models on top of the hybrid engine, closing blind spots no single model or ruleset catches alone.
Built for regulated environments and AI-era codebases.
Related Resources
 Solution Brief
Checkmarx Fusion SAST: AI-Powered Static Code Security Testing
Checkmarx Fusion SAST is purpose-built for how code is written today. With AI coding assistants accelerating code generation across multiple languages, organizations need comprehensive security scanning that covers every language.
Learn More
 Page
FOA Report
Learn More
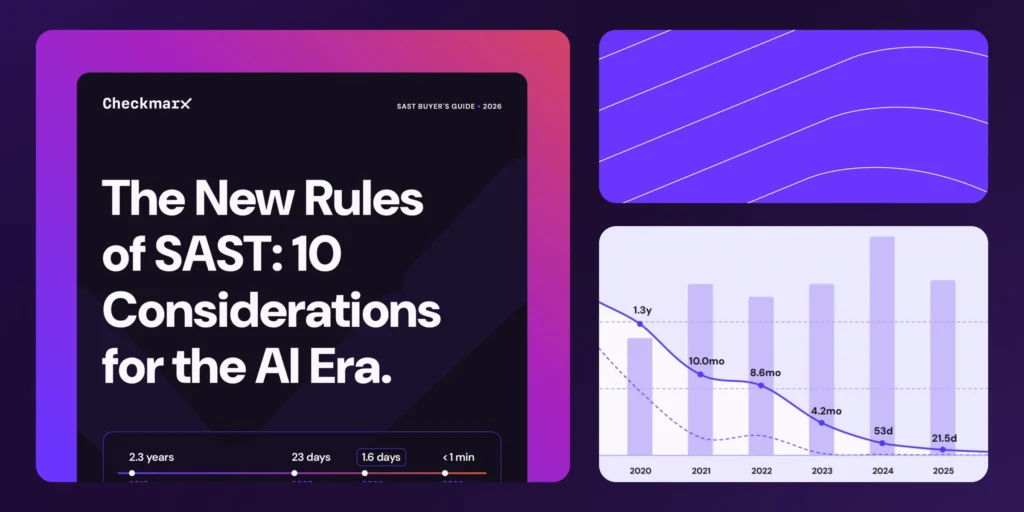 Whitepaper
The New Rules of SAST: 10 Considerations for the AI Era
Learn More
 Solution Brief
Checkmarx Fusion: Hybrid SAST for Higher Detection Accuracy
Learn More
 Customer Story
From Fragmented to Unified AppSec with Checkmarx
Learn More
Checkmarx SAST FAQ
Experience a High-Fidelity SAST Tool in Action
Checkmarx Fusion SAST scans source code, finds critical vulnerabilities, and gives teams the coverage and fidelity to deliver secure applications.
Find Critical Vulnerabilities
in Your Applications

Hybrid Engine Accuracy
A hybrid query-and-AI-based engine delivers precise results across your entire codebase.

Checkmarx Fusion
Checkmarx Fusion SAST – Curated AI models reason about your code from different angles.
-

Widest Coverage
The broadest language and framework coverage, from established enterprise languages to emerging ones.
-
Developer-First Remediation
Integrate SAST into the IDE and get AI-powered fix guidance right where developers work.


Find What Your
Current Scanner Is Missing.
Request a personalized demo and see what Checkmarx SAST finds in code your current tool cannot.


