Checkmarx Fusion SAST:
Find More Real Vulnerabilities
AI-generated code ships in more languages than most SAST tools support. Checkmarx Fusion SAST pairs proven analysis with frontier-model reasoning to find what either misses alone, at predictable cost.
More Signal. Less Noise.
A SAST Tool Built to Find Everything That Matters.
Different methods catch different risks. Checkmarx brings complementary strengths together in one fused SAST experience.
From source code scanning to remediation, Checkmarx Fusion SAST gives enterprise teams the accuracy, coverage, and AI-powered intelligence to secure code without slowing down delivery.
High Fidelity SAST Tool
A deterministic engine for core languages, plus LLM-based scanning with Fusion SAST for emerging languages and frameworks that rules alone don’t cover. If LLMs can code it, we can scan it.
Try Scanning in a Demo
Several curated frontier models reason about your code, each approaching it differently, to surface vulnerabilities with no known rule and no prior CVE. Choose the depth and cost you need.
Try Checkmarx Fusion SAST in a Demo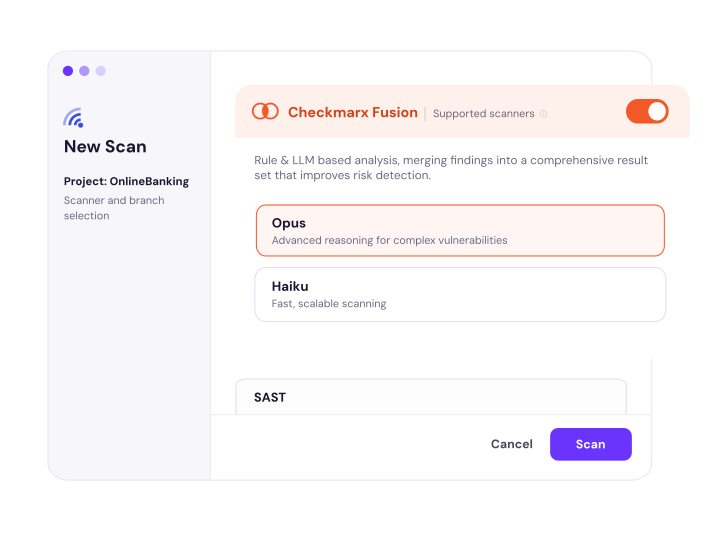
Fusion findings flow directly in Checkmarx One, where Risk Orchestration adds application, risk, policy, and ownership context. Triage Assist helps determine what needs action using reachability and exploitability, while Remediation Assist generates review-ready fixes for developers.
See AI-powered Triage & Remediation in Action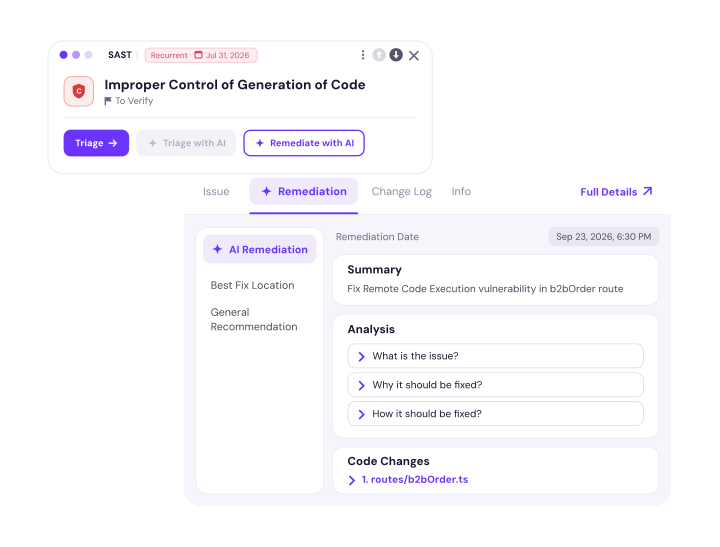
Full SAST scans for deep analysis, incremental scans for PR-level speed. Fusion is on by default in the Checkmarx SAST scanner. Run frontier-model reasoning when Credits are available, or turn it off and continue as before.
Try Code Scanning in a Demo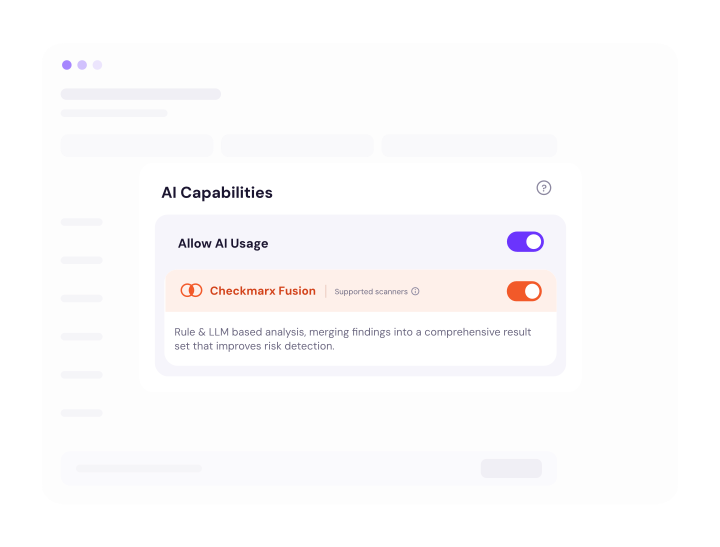
Scan source code directly from GitHub, GitLab, Azure, and Bitbucket with no compilation needed. Fusion SAST runs in the workflow your team already uses, so deeper analysis never means a second scanner to deploy.
See Multiple Results in One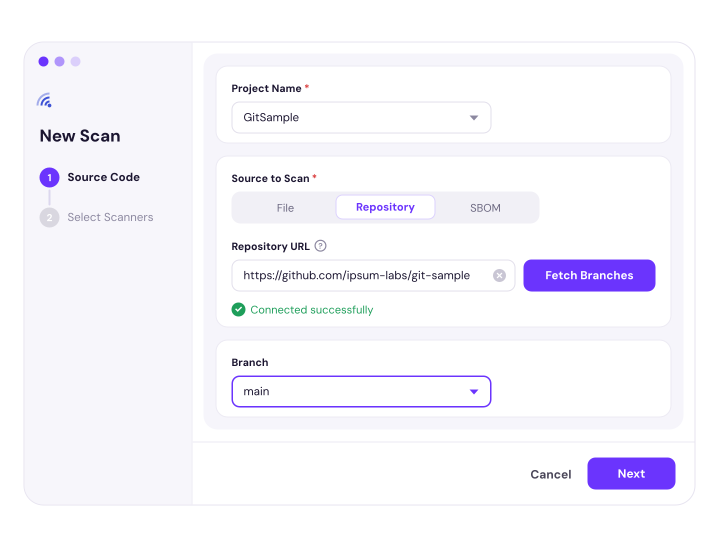
With AI generating unprecedented amounts of code, security has to be an enabler, not a bottleneck. This hybrid approach combining rules-based precision with AI-powered reasoning gives AppSec teams a way to scale while delivering high fidelity performance. The industry finally has an approach built for what AI demands.
Checkmarx Fusion SAST is part of the
Claude Marketplace
Checkmarx is a proud member
of the Cyber Verification Program
Proven Analysis. Frontier Reasoning.
One Higher-Fidelity Result.
Fusion SAST combines Checkmarx's established application security analysis with curated frontier reasoning from Anthropic via Amazon Bedrock. Findings Analysis reconciles the results into a single, higher-fidelity view of application risk.
Established application security analysis
Checkmarx Fusion SAST
- Rules and program analysis
- AI-based analysis where applicable
- Supported Anthropic models via Amazon Bedrock
- Reasoning across complex code and logic
- Additional discovery beyond established patterns
Selected model • lines of code scanned
Findings Analysis / Reconcilation
- Classify
- Reconcile
- Deduplicate
- Reduce noise
Predetermined Credit rates.
Economics you can forecast.
Checkmarx Fusion is a compelling example of what becomes possible when organizations bring frontier AI intelligence to bear within the kind of deep security context Checkmarx has spent decades building.
Every Language. Every Vulnerability. One Fusion SAST Scanner.
- Any language. Highest-fidelity findings. Zero compromises.
- Fusion SAST catches what AI-only tools miss and what rules-based tools can’t reach.
- One result set. Your existing workflow. Nothing new to learn.
Enterprise SAST Tool Built for the AI-DLC
AI is changing how code gets written and how vulnerabilities are found and fixed. Checkmarx Fusion SAST is built for that shift, combining high-fidelity analysis, broad coverage, and intelligent remediation across the AI-DLC.
AI-generated code ships faster than scanners can follow

Coverage Without Tradeoffs
AI-only scanners can return different results on each scan and miss new languages. Checkmarx delivers consistent results on every scan, across every language, without trading accuracy for breadth.
AI Scaled Your Code Faster Than You Can Keep Up
Close Security Gaps
AI generates code faster than security teams can scale. 81% of organizations already knowingly ship vulnerable code. Every gap is a finding that slips through. Checkmarx closes it, across every language, at every stage of the pipeline.
Noise kills adoption. False positives kill trust in your SAST results
Cut the Noise
Findings Analysis cuts false positives by 60%, automatically, classifying SAST scan results before they reach your team so the findings that matter get fixed.
Vulnerabilities found too late cost more to fix
Fix Where Developers Work
Checkmarx surfaces findings in IDEs, PR checks, and pipelines with fix guidance developers can act on earlier. Security stays inside the development flow, reducing rework and late-stage cost.
No one approach finds everything
End the tradeoff between proven analysis and frontier reasoning
Checkmarx Fusion SAST adds frontier-model reasoning on top of the proven hybrid engine, then reconciles every finding into one result your team can investigate and act on.
Find Source Code Vulnerabilities
Rules or AI Alone Miss
Checkmarx Fusion adds curated frontier AI models on top of the hybrid engine, closing blind spots no single model or ruleset catches alone.
Built for regulated environments and AI-era codebases.
Related Resources
 Solution Brief
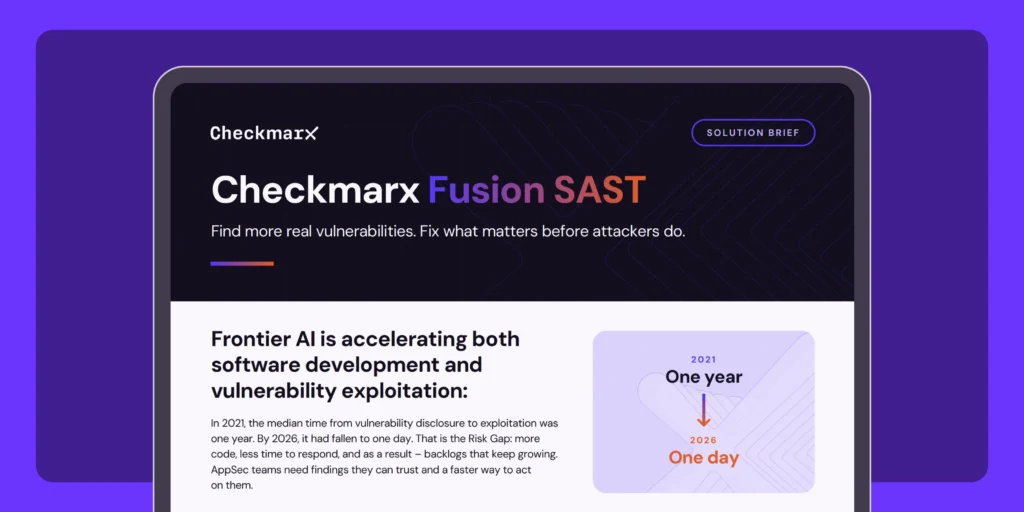
Checkmarx Fusion SAST: AI-Powered Static Code Security Testing
Checkmarx Fusion SAST is purpose-built for how code is written today. With AI coding assistants accelerating code generation across multiple languages, organizations need comprehensive security scanning that covers every language.
Learn More
 Page
FOA Report
Learn More
 Whitepaper
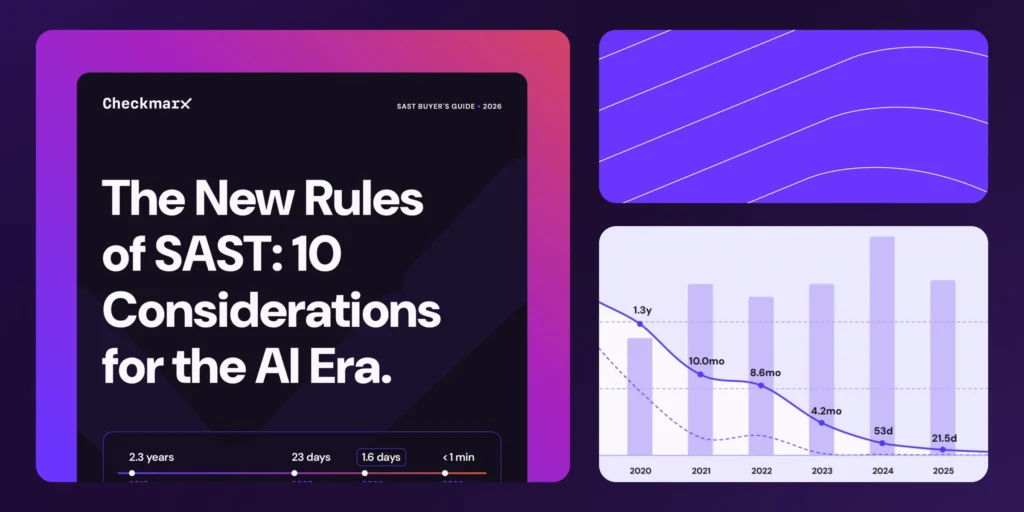
The New Rules of SAST: 10 Considerations for the AI Era
Learn More
 Solution Brief
Checkmarx Fusion: Hybrid SAST for Higher Detection Accuracy
Learn More
 Customer Story
From Fragmented to Unified AppSec with Checkmarx
Learn More
Checkmarx SAST FAQ
Checkmarx Fusion SAST is Checkmarx’s highest-fidelity static application security testing experience. It combines established Checkmarx application security analysis with curated frontier-model reasoning to produce one fused, higher-fidelity result.
It is designed to find more real vulnerabilities, including novel and contextual risks established detection may miss, without turning broader discovery into a larger backlog of noise.
Checkmarx Fusion SAST improves detection without increasing noise. In SAST testing, F1 accuracy score increased to 0.74, meaning Checkmarx found more real vulnerabilities while preserving precision.
The core SAST foundation does not consume frontier-model Credits. Additional frontier reasoning in Fusion SAST is metered through Checkmarx Credits at a predetermined rate based on the selected model and lines of code scanned, visible before the scan runs.
Checkmarx SAST already provides a high-fidelity hybrid analysis foundation using rules analysis plus AI-based analysis where applicable. Fusion SAST adds curated frontier-model reasoning for deeper discovery.
F1 measures precision and recall together: how effectively a scanner finds real vulnerabilities while avoiding false positives.
Fusion SAST supports a curated set of frontier models, including models from Anthropic. Available models can evolve as Checkmarx validates new capabilities, so teams benefit from advances in frontier reasoning without tying their application security architecture to a specific model version.
The models used within Fusion SAST are enabled through Amazon Bedrock, which protects customer source code and data from being shared back with Anthropic. All exchanges stay contained within the customer’s own cloud environment or tenant.
No. Fusion SAST operates within the Checkmarx One workflow. Teams use their existing repositories, scan configuration, and application-security processes rather than deploying a separate frontier-AI scanning system.
Most SAST tools rely on pattern matching against predefined rules. Checkmarx SAST uses a hybrid approach: deterministic, auditable analysis for core languages, an AI-powered engine for emerging and AI-generated code, and automatic classification that cuts noise by 60%. The result is 70% better fidelity than traditional SAST. Coverage, precision, and signal in the same scan.
Findings Analysis is an AI-powered capability that evaluates scan results and classifies each finding as a likely true positive or false positive before it reaches your team. It reduces noise automatically so engineers focus on findings worth fixing.
Frontier models can identify vulnerabilities, reason across complex code, and propose fixes. Fusion SAST combines that reasoning with Checkmarx’s established security analysis and findings validation in one enterprise SAST workflow. Through Checkmarx One, teams can also apply security policies, manage findings in context, and connect detection to triage and remediation.
The advantage is a complete governed security workflow rather than building and maintaining these capabilities around a standalone frontier model.
AI-generated code can accelerate development, but it does not guarantee secure output. Checkmarx Fusion SAST scanner validates generated and human-written code with hybrid analysis, broad language coverage, and Findings Analysis to reduce noise.
Checkmarx Fusion SAST is part of the Checkmarx One platform. This allows a complete enterprise application security program to run on a single platform, reducing total cost of ownership and allowing for correlation and better actionable insights. The Checkmarx One platform includes SAST security scanning, DAST security scanning, AI Supply Chain Security, AI BOM, SCA, SCS, API Security, IaC Security, and Container Security.
On-premises SAST uses a rules-based scanning engine. SAST on Checkmarx One includes the AI-based engine, the Findings Analysis Engine, and Checkmarx Fusion. None of which are available on-premises. If you’re running on-premises today, moving to Checkmarx One is how you access the full hybrid scanning architecture and the F1 gains that come with it. Learn more in the on-prem to cloud migration brief.
Checkmarx SAST supports a broad range of modern, enterprise, and legacy languages, including Java, JavaScript, TypeScript, Python, C#, C/C++, Go, PHP, Ruby, Swift, Kotlin, COBOL, PL/SQL, and more.
With Fusion SAST, LLM-based scanning extends detection to emerging languages and frameworks that deterministic rules don’t cover.
A SAST security scan reviews source code, looking for vulnerabilities in static code – it doesn’t require the application to be running. In contrast, a dynamic application security testing (DAST) scan evaluates a running application, testing how it behaves in real-time by simulating attacks. While SAST finds issues in the code, DAST focuses on identifying runtime vulnerabilities like authentication or input validation problems.
Checkmarx Professional Services offers the Checkmarx Application Security Assessment & Remediation Service. This is a focused engagement with Checkmarx. We map and prioritize exploitable vulnerabilities in your code, help confirm it, provide the best course of action for the code fixes that matter most, and document the remediation.
Yes. Checkmarx SAST scans source code directly from repositories such as GitHub, GitLab, Azure, and Bitbucket, without requiring a build. As an enterprise SAST tool, it adds security analysis, workflow integration, fix guidance, and risk context beyond basic source code scanning.
Experience a High-Fidelity SAST Tool in Action
Сheckmarx Fusion SAST scans source code, finds critical vulnerabilities, and gives teams the coverage and fidelity to deliver secure applications.
Find Critical Vulnerabilities
in Your Applications

Hybrid Engine Accuracy
A hybrid query-and-AI-based engine delivers precise results across your entire codebase.

Checkmarx Fusion
Checkmarx Fusion SAST – Curated AI models reason about your code from different angles.
-

Widest Coverage
The broadest language and framework coverage, from established enterprise languages to emerging ones.
-
Developer-First Remediation
Integrate SAST into the IDE and get AI-powered fix guidance right where developers work.


Thank You!
Your Custom Checkmarx Demo Request was Successfully Sent!
A member of our team will contact you shortly to set up your demo.
During the call, one of Checkmarx AppSec experts will review your current application security situation and give you a tour of Checkmarx Solutions.
Find What Your
Current Scanner Is Missing.
Request a personalized demo and see what Checkmarx SAST finds in code your current tool cannot.


